99%
noise reduction
3 min
AI agent investigations
↓60%
triage + notification time
Meet the AI Agents behind Zscaler MDR
Generates threat hunting recommendations based on analyzed security incidents.
Analyzes threat data to determine how highly to prioritize the alert.
Investigate and triage identity-based security alerts from the Falcon Identity Protection platform.
Investigate and triage alerts from Microsoft Entra Identity Protection.
Investigate and triage identity security alerts from Microsoft Cloud App Security.
Investigate and triage security alerts from Okta Workforce Identity.
Investigate and triage security alerts from Cisco Duo Trust Monitor.
Investigate and triage identity events from Zscaler's detection engine.
Investigate and triage security alerts from AWS GuardDuty.
Investigate and triage security alerts from Microsoft Defender for Endpoint.
Investigates and triages CrowdStrike Falcon endpoint alerts.
Investigate and triage security alerts from SentinelOne Singularity Platform.
Investigate and triage security alerts from Cortex XDR.
Investigate and triage EDR events from Zscaler's detection engine.
Investigates and triages Wiz security alerts across both endpoint (WIZ_SENSOR) and identity-based threat detections.
Analyze login patterns over a 30-day period, identify anomalies, and generate concise reports.
Consults your organizational preferences and security context to recommend whether an alert should be suppressed.
Analyzes emails and attachments to generate comprehensive reports and analysis.
Identify phishing emails and provide comprehensive reports.
Provide summaries, recommendations, and narratives about a threat to aid understanding and response.
Provides prioritized remediation guidance for containment, eradication, and hardening directly in the threat timeline.
Analyzes security alerts, enriches them with context, and routes them to specialized platform-specific agents.
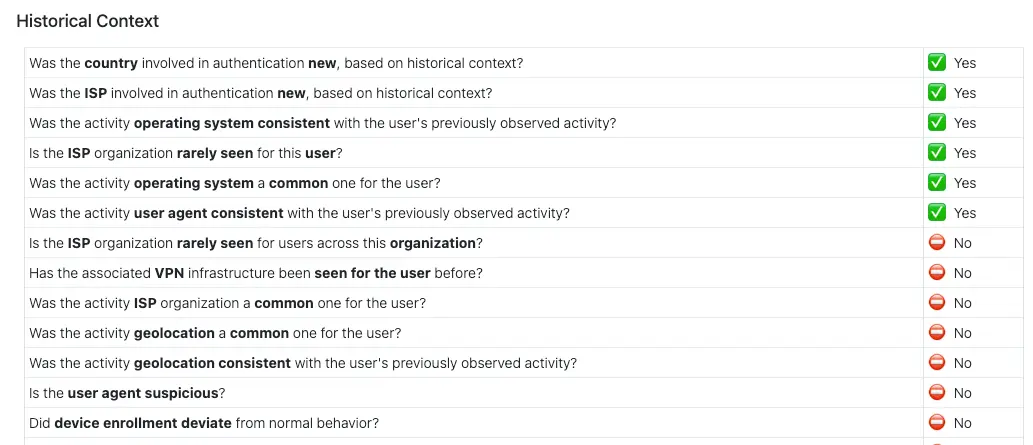
Add context to threat timelines related to user activity vs typical baseline behavior.
Provide detailed threat intelligence context for ongoing security investigations, including profiles.
Provide knowledge to SOC personnel regarding MDR product and features.
Analyzes security alerts from various platforms and generates structured summaries and recommendations.
Reviews user-provided tuning instructions and provides feedback on whether they need changes before being implemented.
Generates a concise explanation comment for why a security alert was considered non-malicious.
Generates system hardening recommendations based on threat indicators.
Generates concise 1-3 sentence threat summaries from cybersecurity incident data.
Coordinates sub-agents to produce comprehensive threat reporting.
Supported Integrations

How Our Agents Work
Our AI agents dynamically interact with data and systems to execute a specific job based on real-time inputs and context. Powered by AI models like LLM, these agents adapt their behavior based on tasking – a massive upgrade from rigid automated workflows.

Our Approach
Most AI agents chase breadth at the expense of reliability. Our AI agents are specialized, focusing on a narrow set of tasks that they perform flawlessly.
- Imbued with a decade+ of real-world security operations experience
- Guided by narrowly-scoped, expert-crafted standard operating procedures
- Managed and tuned by elite human operators
- Continuously optimized with feedback and new intelligence

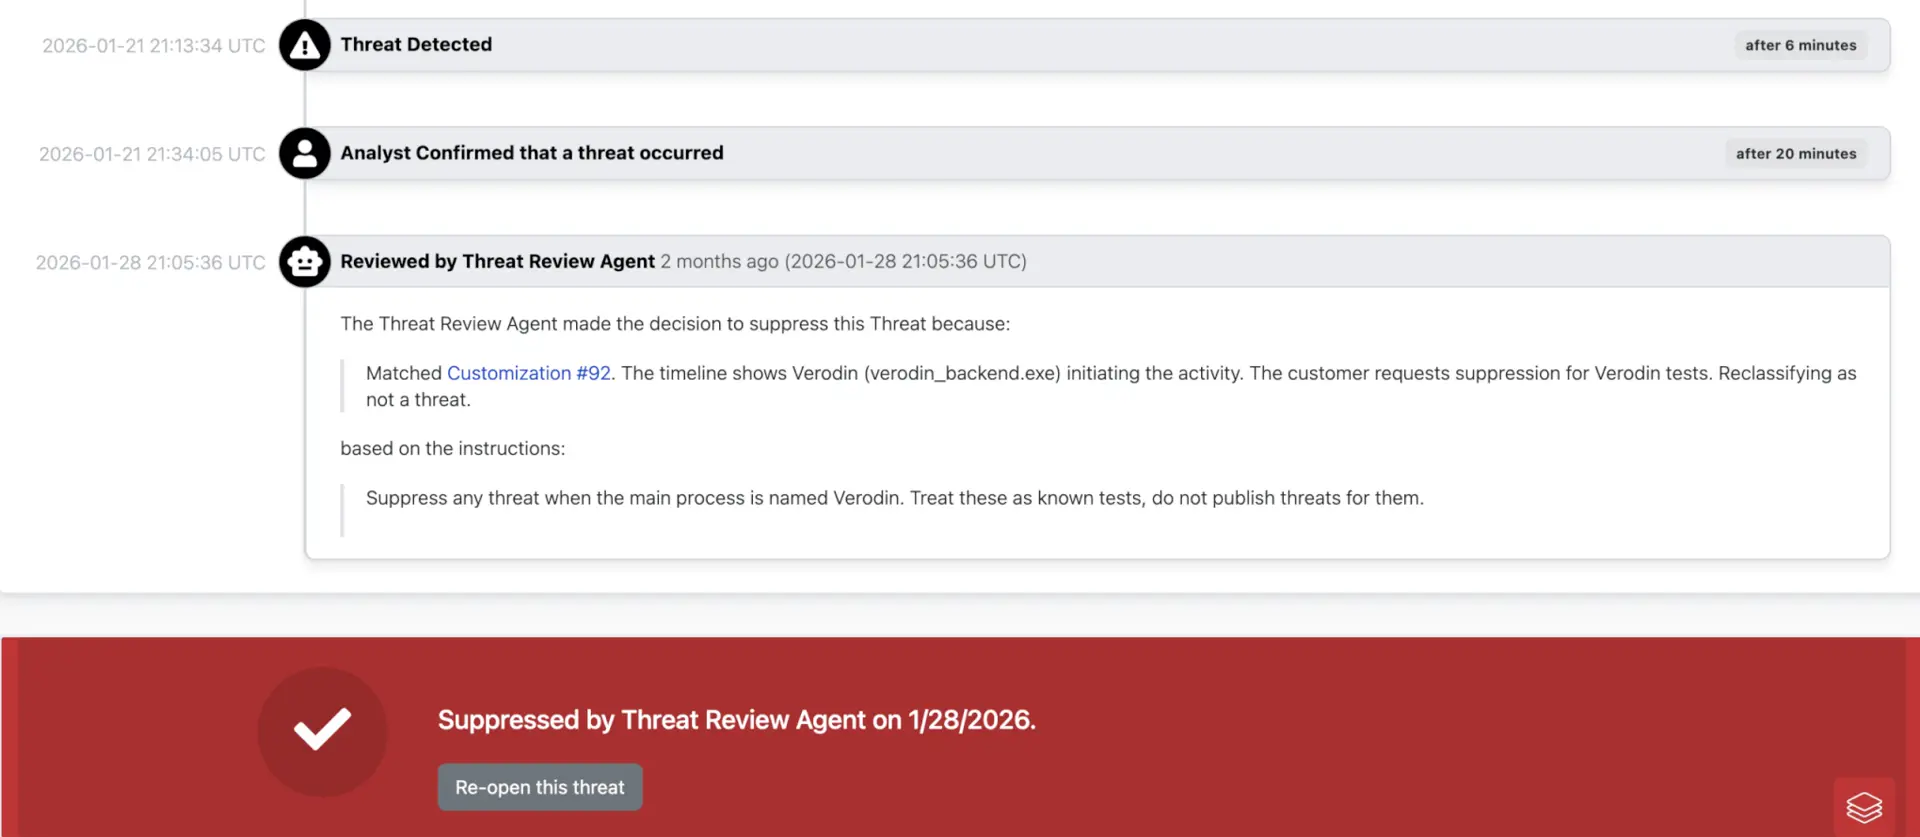
Agentic Tuning
Filter out highly specific and difficult-to-tune alerts with a few plain-language sentences.
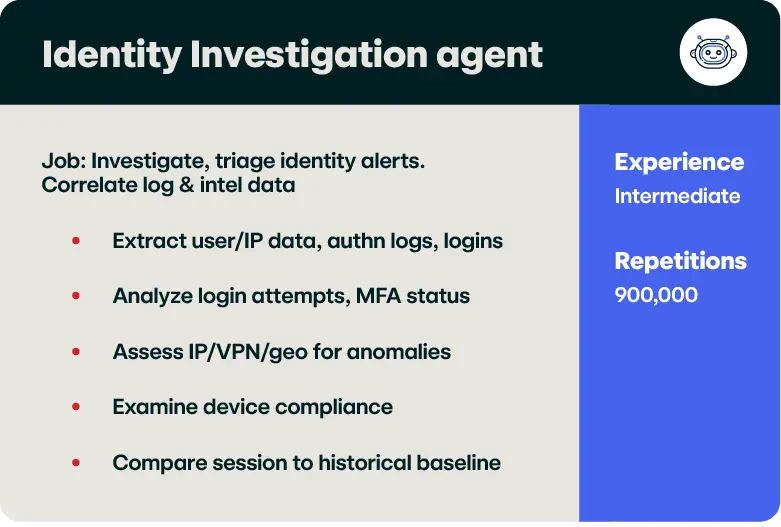
Specialized AI agents
Specialization makes each agent reliable and highly-skilled.
Agent visibility
See exactly what your AI agents are doing and why.
FAQs
Zscaler MDR customers already have expert AI agents working on their behalf. We are actively exploring pricing and packaging models, alongside MCP server options, for future customers looking to access these AI agents directly.
Our AI agents are trained on 11+ years and counting of high-fidelity threat detection, investigation, and incident response data and industry-leading security operations workflows. The richness and reliability of the training data is what contributes to a 99.7% threat accuracy rating and rapid responses times when they collaborate with our human experts.
Data utilized by our AI agents never leaves controlled infrastructure for processing, storage, training or any other reason. Your data is (1) not available to other customers, (2) not available to third parties, (3) not used to train external AI models, and (4) not used to improve any third-party products or services. The underlying AI models do not interact with other external services, such as ChatGPT.
We solicit customer feedback–’thumbs up, thumbs down’ on outputs–in our product and manually review all off-target feedback. We also continuously measure the impact of AI agents on our accuracy, completeness, and timeliness of threat notifications. We only use AI agents to the extent that they benefit our overall performance for our customers.
We validate trustworthiness of AI agent performance via extensive functional testing in which all outputs that vary beyond 10% of our ideal output are manually inspected. And as mentioned in the prior question, we continuously measure the impact of AI agents on our accuracy, completeness, and timeliness of threat notifications. We only use AI agents to the extent that they benefit our overall performance for our customers.