
Since its inception, Zscaler has remained dedicated to protecting our customers—it’s at the very core of everything we do. In our first decade, we focused intently on providing users secure access to applications, first to the internet and SaaS with Zscaler Internet Access (ZIA) followed by private applications with Zscaler Private Access (ZPA), both of which are rooted in zero trust. I’m proud to say we’ve been successful on this front and will continue to aggressively innovate to keep users, workloads, devices, and data safe.
But zero trust is most effective when approached as a holistic strategy applied not only to users but also across the entire organization, including workloads in the cloud. Our vision for cloud security focuses on protecting any workload—whether traditional VMs or cloud-native applications—with a broad set of solutions powered by the Zero Trust Exchange. These offerings draw from our strengths in cloud posture, entitlements, data loss and threat prevention, and workload communications. With today’s introduction of Workload Communications, we’re delivering on a major component of our commitment to help our customers extend zero trust to secure their public cloud workloads.
As organizations increasingly adopt multi-cloud and hybrid-cloud strategies, building multi-cloud networks by simply extending the corporate WAN increases risk and introduces operational complexity. With workloads being deployed in multiple regions of multiple cloud providers, these mesh networks drive up costs and are also difficult to implement, scale, and manage. Many organizations have relied on a castle-and-moat approach to securing the cloud, yet this uses legacy VPN and firewall solutions which increase the attack surface and facilitate lateral threat movement, putting company data and applications at risk.
Zero trust security architecture is superior to network security. Instead of relying on a routable network with firewalls, you connect the right entity to the right entity through a secure exchange. Zscaler’s Zero Trust Exchange uses identity and context to directly connect entities such as users, devices, and applications to create a seamless and secure experience. Zscaler pioneered the Zero Trust Exchange by securely connecting users to apps from anywhere.
Today, I am happy to announce that Zscaler is extending zero trust to the public cloud with Workload Communications. Enabled by the Zscaler Zero Trust Exchange, Workload Communications extends the capabilities of ZIA and ZPA to clouds, allowing workloads to communicate with other workloads in any region of any cloud provider, over any network. Zscaler has partnered with major cloud providers such as AWS and Microsoft Azure to deliver a network-agnostic zero trust fabric that works over the Internet, Direct Connect, and Express Routes to meet the specific communication needs of cloud workloads in single and multi-cloud environments.
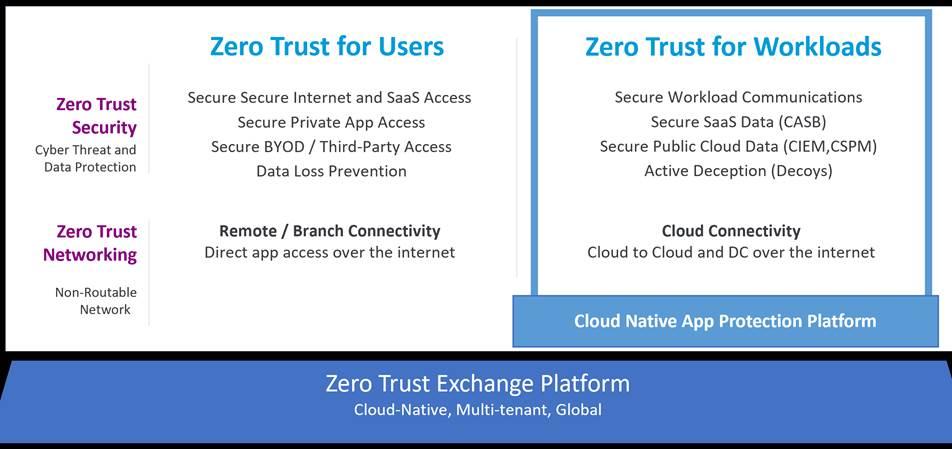
We're very excited with the response from our customers who have already implemented Zscaler’s Zero Trust for Cloud Workload solution. I’d like to invite you to learn more about their success as well as the solution by watching our Zero Trust Your Cloud Workloads launch event live in your region or on-demand. To learn more, please also visit the Workload Communications page on our website.



