Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
CSA AI Summit keynote: The art of the possible with zero trust

RSA Conference 2024 kicked off in San Francisco yesterday with the Cloud Security Alliance holding its annual summit, this time themed around AI. The industry association, which is celebrating its 15-year anniversary, invited Jay Chaudhry, founder and CEO of Zscaler, and Ricardo Lafosse, CISO, The Kraft Heinz Company to deliver the first morning keynote.
From “lift and shift” to “transform and improve”
Chaudhry covered the major transformations underway in IT and cybersecurity, pointing out that applications that have moved to the cloud from the data center are not just “lift and shift” but are instead being transformed. Yet many organizations are still lifting and shifting network appliances to the cloud and lifting and shifting security to the cloud. He explained: “They move the firewall to the cloud as a VM [virtual machine] and they move the VPN to the cloud as a VM and they call it zero trust cloud security,” he explained. “It's still the same mesh network, it's the same routetable management. And it's the same attack surface, because any IP address that's exposed to the intranet is your attack surface. And it's the same lateral movement because a single infected machine in a branch from the cloud traverses laterally and infects everything.”
Zero trust advancements and the role of AI
Chaudhry then launched into a vision for a modernized alternative based on a zero trust architecture. Applications are not exposed to the internet because they use inside-out connections that, in this case, terminate in the Zscaler cloud, thereby eliminating attack surface and lateral movement. “I would love to see a day when all CISOs can proudly say. ‘I have no public-facing IP address,’” he said.
The zero trust pioneer then explained how to overcome the challenges of segmentation and SD-WAN, before moving onto AI/ML. Chaudhry said that the technology gained from Zscaler’s recent acquisition of Avalor means rather than creating a new data lake, you can ingest logs without creating a copy of it and automate many AI-driven data-intensive activities such as reporting, zero-copy analytics, incident mitigation, and auto-data discovery and classification.
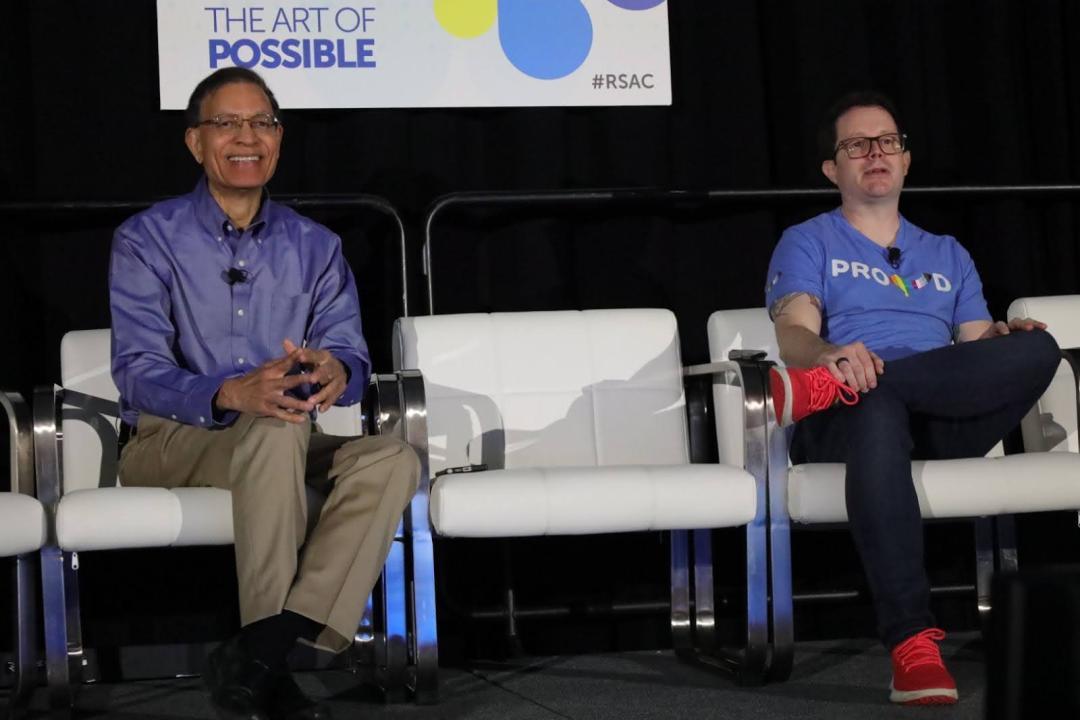
Transformation utopia within reach at Kraft Heinz
Next, Ricardo Lafosse joined Chaudhry for a candid account of the zero trust journey at Kraft Heinz. The first phase, he explained, was to remove VPNs and move to the coffee shop vision where access control was based on MFA and identity and followed users wherever they went. “We had about five to ten thousand users per day active on VPN. So just imagine five to ten thousand bridges active all throughout the day. That could be an attack point across the board.”
Then came shifting user access to applications from layer-three to layer-seven zero trust, which was when end users started to really notice improvements. “It was one of the few solutions where people are like, ‘this is ten times easier. I log in once it is tied into my Office 365, it's tied into the identity and the fabric of my everyday life and it's in the background,’' said Lafosse. Employees had a unified direct access experience to apps, and, as a plus, Kraft Heinz got rid of its traditional gateway URL filter since it was already covered by the Zscaler agent.
This year, Lafosse is piloting role-based access with finance and HR, which have vocal users but can't easily define what apps and data they need to access. Working with Zscaler, they are finding ways to quickly identify common access trends for individuals and segment accordingly.
Reducing risk with Zscaler Branch Connector
The company is exploring the Zscaler Branch Connector to enable the same policy-driven access controls to assets and locations where an agent can’t be installed, such as a badge, a printer, or a camera. Separating a plant or a warehouse from a network and still having zero trust connectivity, is a huge work in progress, said Lafosse, but he sees the value of doing micro and macro segmentation, including from a cyber insurance perspective.
“You're reducing a significant amount of risk from the organization and a risk from the underwriting perspective that can actually increase your coverage and reduce your premiums, which is a win-win across the board.”
Lafosse left the audience of several hundred attendees with key learnings including; the journey does not happen overnight; have small wins that help you get bigger ones; take a modular approach, everyone's journey to zero trust is different; and build the collaboration between security and network teams up front.
What to read next
The golden triangle of secure transformation: when cost, usability, and security come together
Zscaler CEO talks secure digital transformation & AI with Evanta, a Gartner Company

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


