Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Woogle: The fake merger that proves we need zero trust

A few weeks ago, Google dropped a bombshell: a $32 billion move to acquire Wiz.
That’s billion with a “B”—the kind of money where you could buy a 2025 Ford Raptor R in every color, then still have enough left over to buy Reddit and give it a long-overdue personality transplant.
As I was recording my PEBCAK podcast, I had a thought: what if, instead of acquiring Wiz, Google just merged with them in a glorious branding mashup? I started tossing around names like Wizgle, G-Wiz, and my personal favorite—Woogle.
Then, like any reasonable adult with an internet connection and a sense of mischief, I thought to myself: What would happen if I posted a fake announcement on LinkedIn saying Google and Wiz had merged?
So I did.
Using the dark arts of ChatGPT and a suspiciously professional-looking fake logo, I fired off a spoof announcement at 5:00 a.m. on a Monday: you know, peak “executive reads LinkedIn on the toilet” hours.
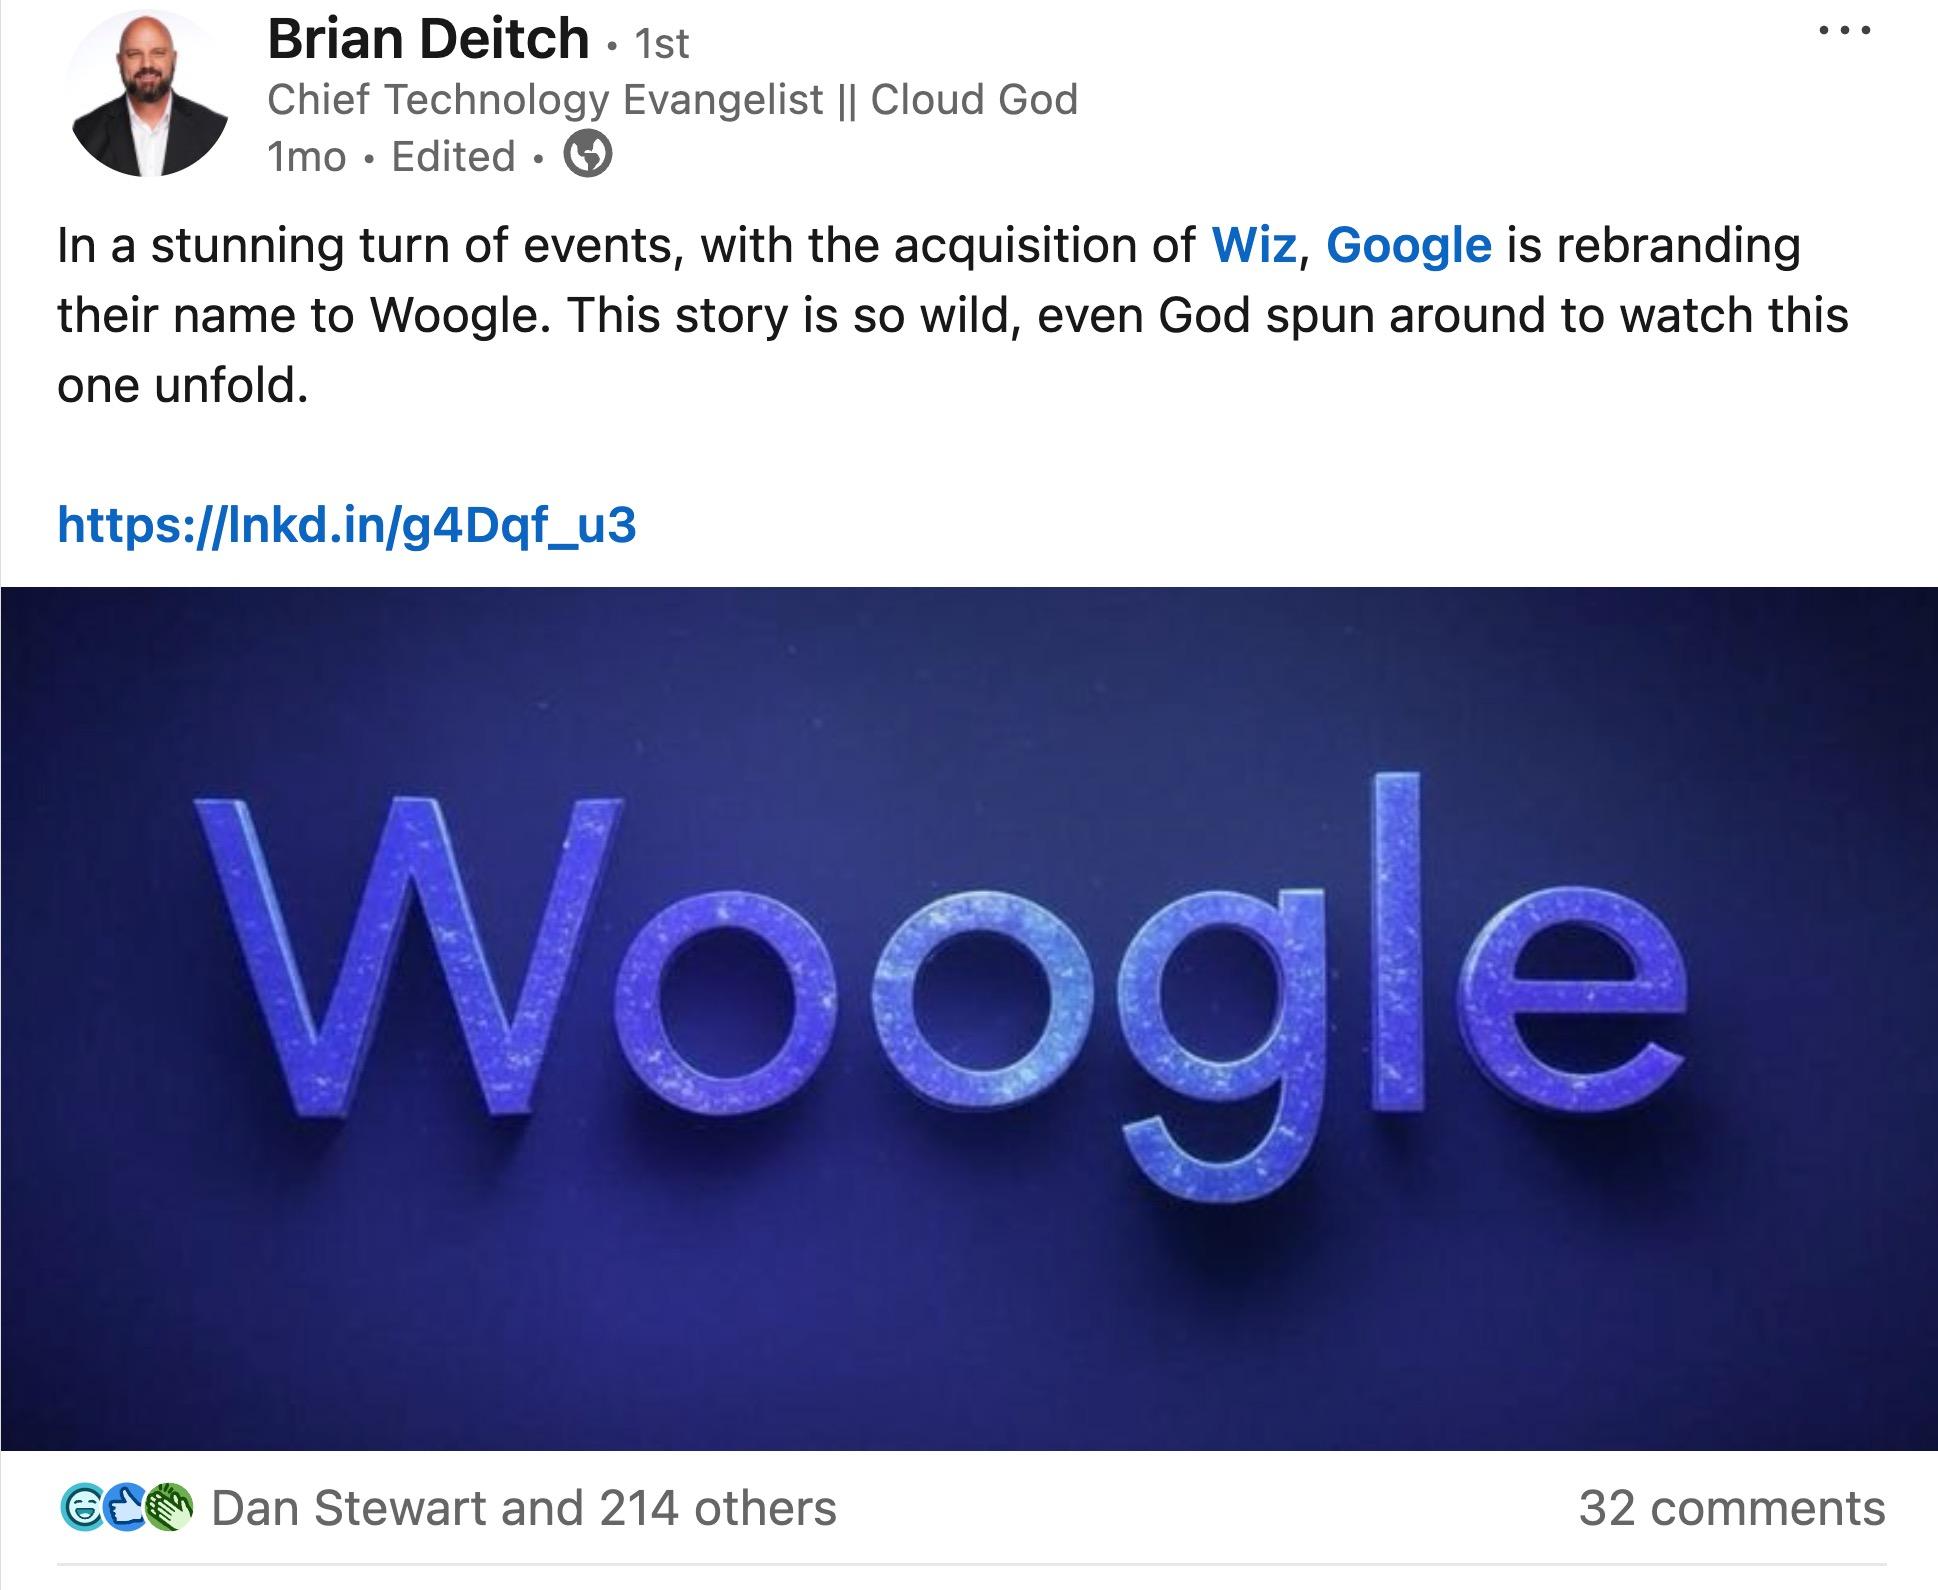
And then I watched.
The Experiment
I embedded a harmless (but external) link just to see what kind of traction it would get. It wasn’t phishing. It wasn’t malware. It wasn’t even a rickroll. Just a decoy. A social engineering honeypot.
Within three days, the link was clicked 1,813 times. By week four, over 2,500.
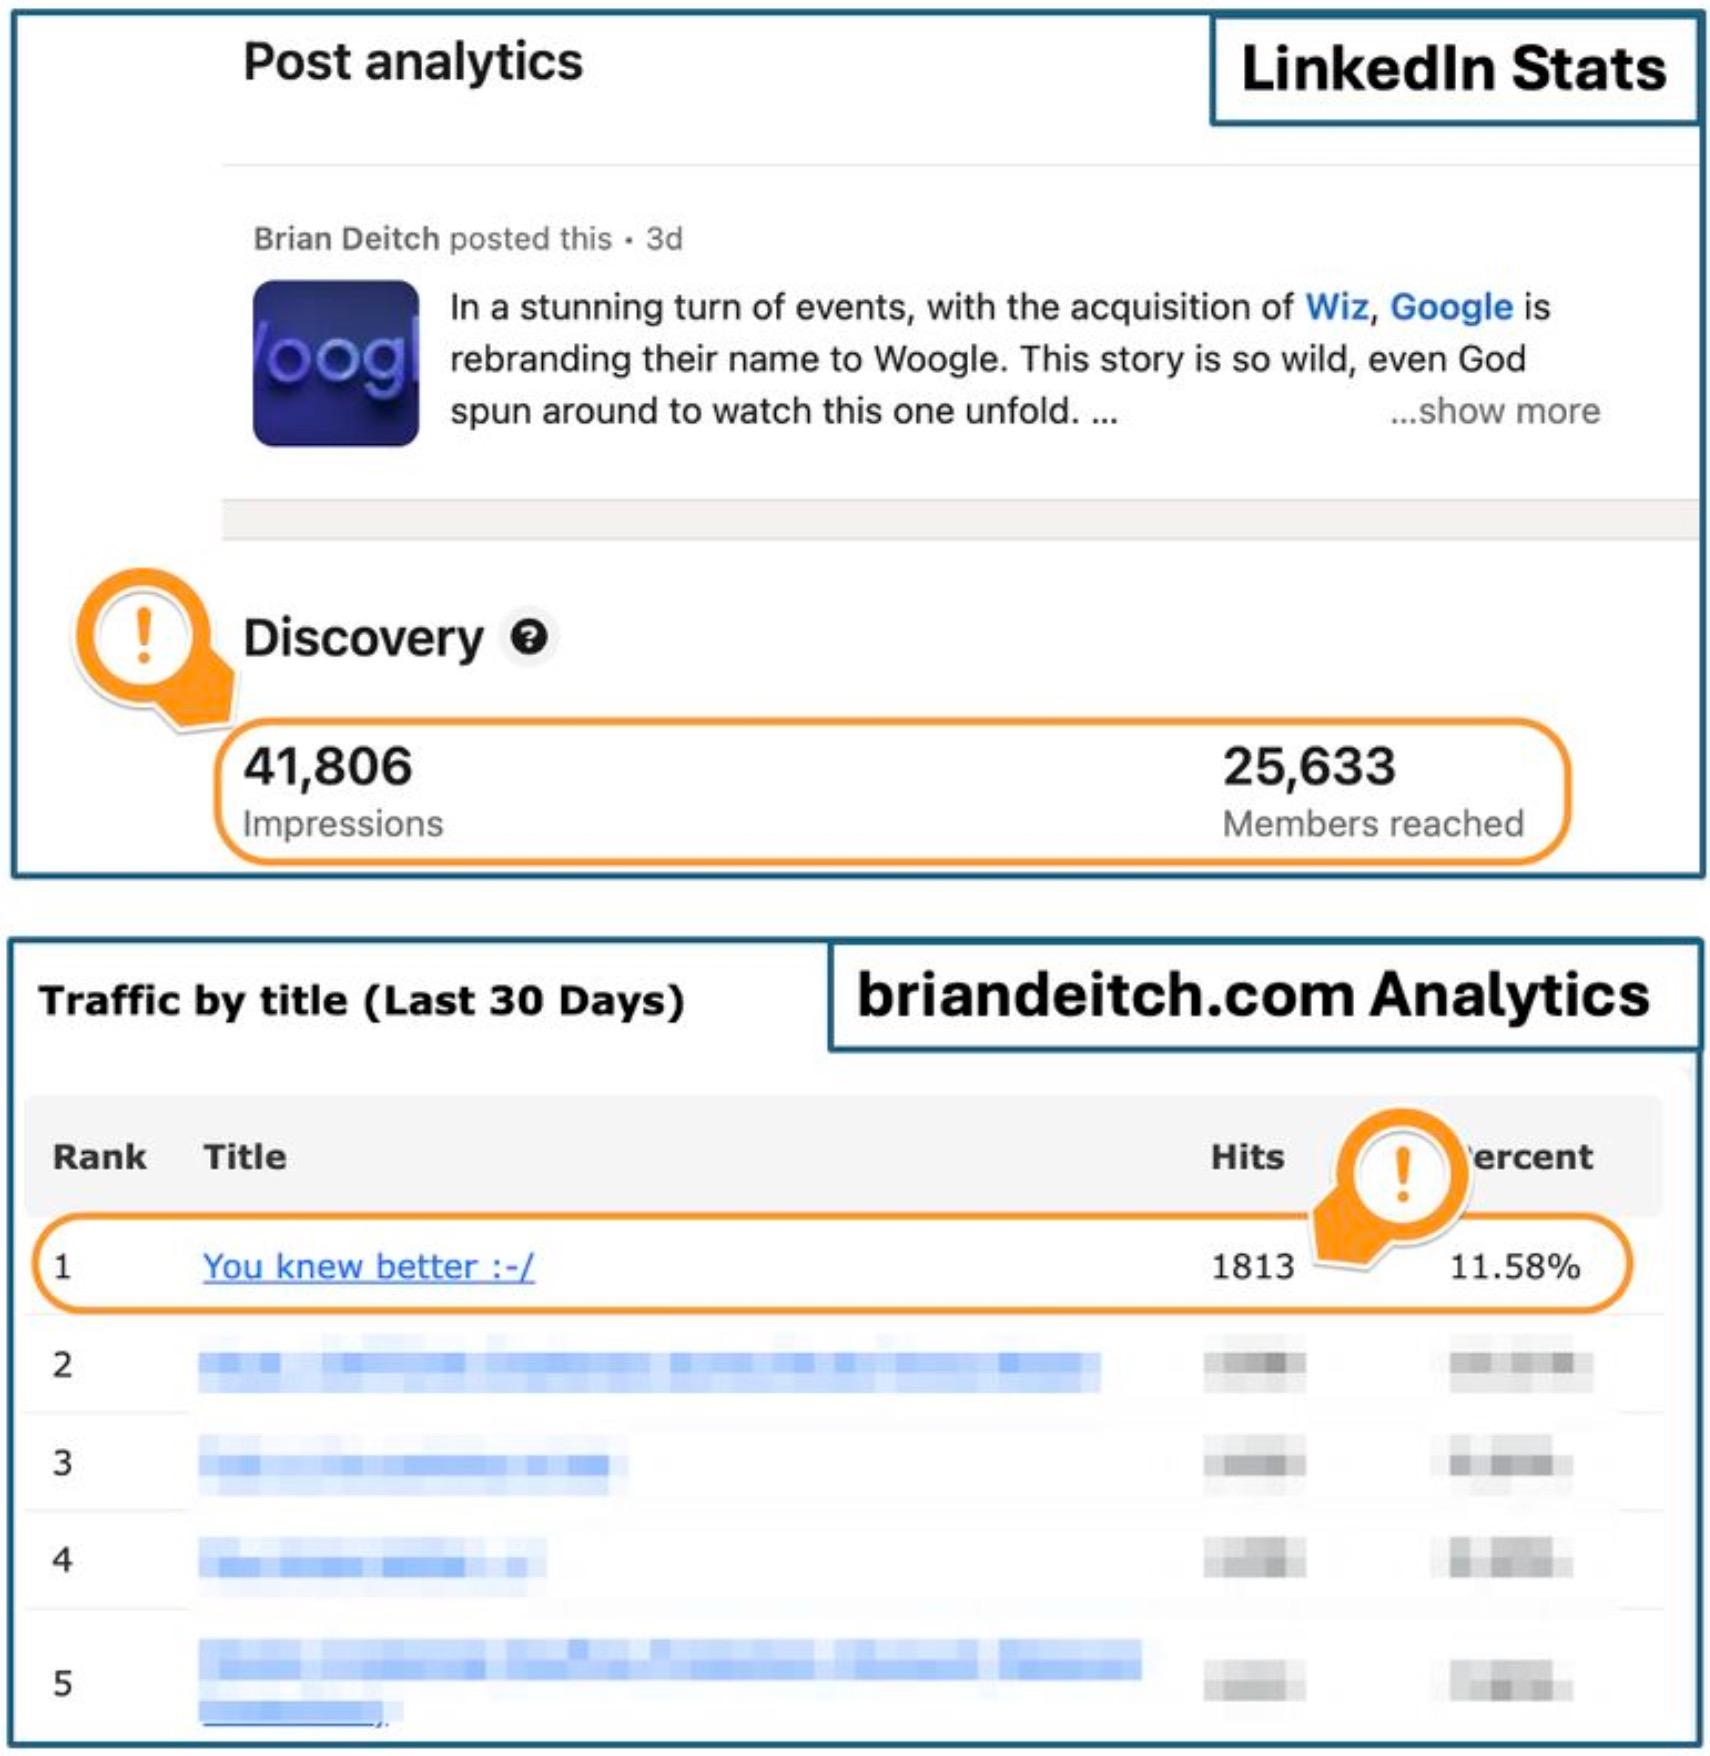
Imagine for a second that this wasn’t some playful hoax. Imagine that link had been laced with malware, cross-site scripting, or an actual credential harvester.
This wasn’t a test environment. This was LinkedIn, a platform that professionals trust implicitly. But here’s the problem: trust is not a control.
Lessons from Woogle
- Even the best of us click dumb links. Titles like “BREAKING: Google merges with Wiz in $32B ‘Woogle’ Deal” are catnip.
- User training is still your first and last line of defense. You can’t patch human curiosity, but you can make people pause before clicking.
- TLS inspection is non-negotiable. Just because something is encrypted doesn’t mean it’s safe—it might just be a very secure Trojan horse.
- Zero Trust isn’t a vibe—it’s the equation for not getting owned. One user. One click. That’s all it takes. 1800+ fell for it, and this wasn’t even real. Trust nothing, inspect everything.
So what started as a joke turned into a proof point: if your security strategy hinges on "nobody here would fall for that," then congratulations—you’re already compromised. The Woogle isn’t just a mythical merger. It’s a mirror.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


