Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Beyond The Crown Jewel Fallacy: Making Segmentation Work for Your Business
In Zero Trust conversations, there’s a familiar story many organizations tell themselves.
It starts with identifying the most critical applications, the “crown jewels”, and surrounding them with some ZTNA solution. Access is locked down, dashboards turn green, and on paper, least-privilege access looks like a mission accomplished.
But this story is incomplete.
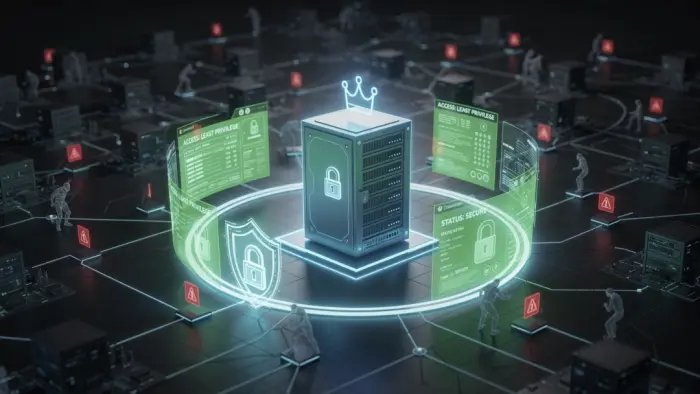
Focusing only on crown jewels is one of the most dangerous and pervasive myths in cybersecurity today. It gives the false sense of security while leaving the majority of your environment exposed to lateral movement.
Securing your most valuable assets is a critical first step, but it’s a dangerous fallacy to believe that this alone delivers a complete segmentation strategy.
The Fallacy: Partial Protection is a Full-Time Risk
Think of your enterprise network like a house. The crown jewel approach is like installing a state-of-the-art vault door on the master bedroom while leaving the front door, windows, garage, and the back door wide open.
An attacker won’t waste time trying to breach the vault. They will simply walk in through an open window instead, targeting certain “non-critical” applications that are unprotected. Once inside, they have free rein to move laterally across your network, turning a small breach into a catastrophic data leak. They can locate and steal your intellectual property and business records, while also establishing a foothold for a future ransomware attack.
Modern attacks rarely start where you’ve invested the most security. They start where you’ve invested the least. By concentrating your efforts solely on a small set of crown-jewel applications, you often leave open the vast majority of your potential attack surface:
- Unsegmented – Users and workloads can reach far more than they should
- Under-monitored – “Low-value” apps get less visibility and fewer controls
- Ideal launchpads – Perfect footholds for ransomware and data exfiltration
The Operational Nightmare: Why Manual Segmentation Fails at Scale
If pervasive segmentation is the goal, why does everyone get stuck at the crown jewels? Because for most organizations, the operational reality of scaling segmentation is an absolute nightmare.
When AJ Sofia, our CTO in Residence, meets with security leaders and customers, he often starts with a simple question:
"How many applications are in your environment?"
The answers are revealing. A CISO might say 400. Someone on their network team might say the real number is closer to 4,000.
This ten-fold gap highlights the three core reasons why manual segmentation is a failing strategy:
- The Discovery Problem: You can’t secure what you can’t see. Manually identifying every application and mapping every user-to-app affinity across a dynamic enterprise is an impossible task.
- The Policy Problem: Even if you develop some tools and manage to discover everything, manually writing and vetting thousands of granular, identity-based policies leads to "segmentation by spreadsheet", which is a process so slow, painful and error-prone it’s often abandoned very early.
- The Maintenance Problem: In a modern business, users change roles, new apps are deployed, applications also scale horizontally–meaning new instances spin up and down automatically, and old ones are retired daily. Manually created policies are outdated the moment they’re written, creating security gaps or breaking user access.
The Paradigm Shift: From Manual Effort to Automated Intelligence
This is not a problem you can solve with more people, more processes, more spreadsheets, or bigger change-control meetings. What’s needed is a shift in how we think about segmentation itself, from a manual project to a strategic, automated, continuous process.
Instead of asking:
“How can my team write and manage thousands of policies?”
We should be asking:
“How can my platform automatically discover every application, use AI to help segment access and generate policy at scale, and continuously strengthen my security posture?”
That’s where an autonomous approach to segmentation comes in.
In this model, segmentation stops being a one-time initiative and becomes a native capability of your secure private access platform—constantly learning from your real user traffic and adapting as your environment changes.
The answer lies in an architecture where segmentation isn’t a one-time, manual project, but an automated, continuous process. In this model, an AI engine helps you:
- Automatically discover all the unmanaged and unknown applications across your environment
- Intelligently segment applications and generate policy recommendations based on business context and risk
- Continuously optimize through live insights dashboards that highlight gaps, trends, and opportunities to strengthen your posture. A key determinant of segmentation success is your ability to continuously monitor access and enforce true least-privilege at all times.
This flips the model from one of overwhelming human effort to one of intelligent, autonomous control, finally making enterprise-wide segmentation a practical reality.
Go Deeper: Join the Webinar
The move from partial protection to total segmentation is the most critical step in maturing your Zero Trust architecture. In our upcoming webinar, Beyond the Datasheet: The Autonomous Journey to User-to-App Segmentation, we will take a deep dive into the architectural principles that make this possible.
We’ll explore the AI engine in action, discuss the future roadmap for autonomous policy, and provide a CTO's perspective on building a security posture that is both more comprehensive and far simpler to operate.
The era of partial, manual segmentation is over. The future is autonomous.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.