Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Enable Secure Access to VoIP and other Server to Client Applications with ZPA

Accelerate the transformation towards Zero Trust access by bringing VoIP, Server to client and other legacy applications over to Zscaler Private Access (ZPA).
The Problem: Why VoIP, SCCM, and Legacy Server-to-Client Apps Break with Zero Trust and VPN Replacement
- The traditional architecture of on-premises VoIP systems ( Cisco Jabber, Genesys, and Avaya Call Manager), Server-to-Client applications (SCCM) and other network-connected applications(follow-me printer and active FTP), fundamentally relies on direct IP-to-IP communication. This architecture requires the source and destination IP addresses to interact without intermediaries like proxies or NAT devices. However, this approach stands in contrast to the principles of zero trust security models.
- Organizations require dedicated time and resources to effectively migrate or modernize their applications while ensuring secure access to these resources.
- Relying on legacy VPN solutions to meet these needs often results in increased operational costs, added complexity, and heightened security risks.
Introducing ZPA Service: Zero Trust Access for Legacy VoIP and Server-to-Client Applications
Introducing the VPN service (for legacy apps) designed to manage exception traffic, specifically for VoIP and S2C applications, while facilitating the transition to a zero trust network architecture.
This solution ensures continued access to applications that are not immediately adaptable to zero trust access, thereby minimizing disruption during the migration process to critical applications.
The Zscaler Private Access (ZPA) achieves this by establishing an alternate path (Second Tunnel) from the Zscaler Client Connector (ZCC) to the Zero Trust Exchange (ZTE).
ZPA Architecture for VoIP and Server-to-Client Apps: Network Connectors, Secondary Tunnel, and Zero Trust Exchange
High-level solution design:
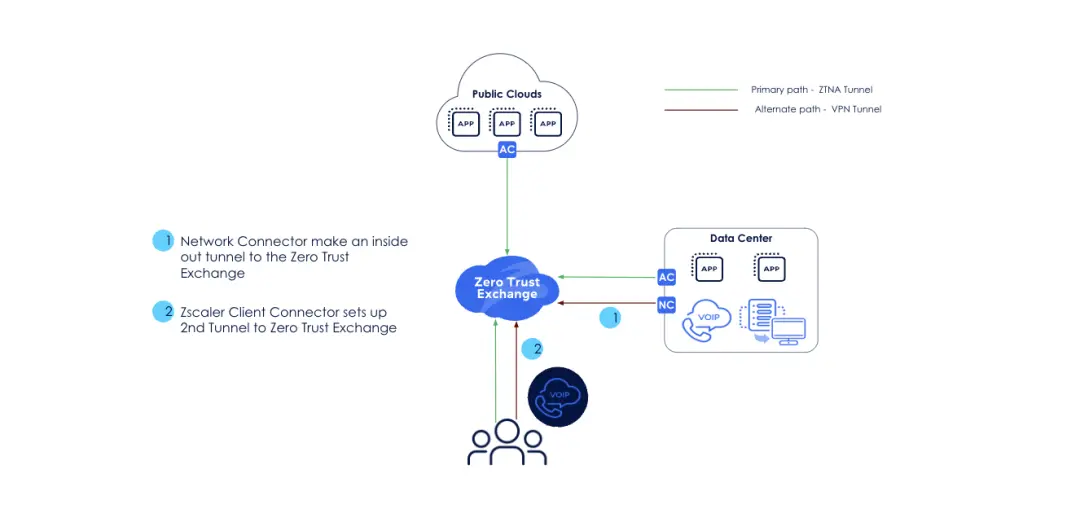
- Network Connectors (NC) can be deployed in datacenter/campus locations hosting VoIP servers and other server-to-client (S2C) systems. These connectors initiate an outbound connection to the ZTE, establishing a secure tunnel between the connector and the ZTE.
- Zscaler Client Connector (ZCC) builds a secondary tunnel specifically for users authorized for VPN services, also connecting to the ZTE. The ZCC is configured to forward traffic through this alternative path based on the configuration parameters set by the administrator.
- ZTE integrates the connection between the ZCC and the NC, creating an end-to-end encrypted pathway that facilitates secure communication for these applications.
Get Started: ZPA Trial for VoIP and Legacy Application Zero Trust Migration
ZPA now supports VoIP and other server-to-client (S2C) applications. This enables customers to move all their applications and streamlines operations by consolidating their secure remote access solution with Zscaler Private Access.
Check out the latest product innovations with ZPA in addition to network connectivity. And read the Forrester Total Economic Impact study to learn how ZPA customers have realized 289% ROI.
Contact your regional sales team to learn more about the solution and get a free 30 day trial to explore the solution, or take a quick tour.
FAQs
Yes. Zscaler Private Access (ZPA) now supports VoIP and server-to-client (S2C) applications including Cisco Jabber, Avaya Call Manager, and Genesys through a dedicated secondary tunnel. The Zscaler Client Connector (ZCC) establishes this alternate path to the Zero Trust Exchange, which integrates with Network Connectors deployed at the datacenter or campus hosting the VoIP infrastructure — creating an end-to-end encrypted pathway without requiring direct IP-to-IP communication or legacy VPN.
Server-to-client (S2C) applications initiate connections from the server side to the client — the reverse of typical client-to-server traffic. Examples include VoIP systems (Cisco Jabber, Avaya), SCCM (Microsoft Configuration Manager), follow-me printing, and active FTP. Traditional zero trust and ZTNA solutions are designed for client-initiated connections, making S2C applications a challenge: they require the server to be able to reach the client directly by IP, which conflicts with zero trust principles of no direct network access. ZPA's VPN service for legacy apps addresses this with a secondary tunnel that maintains S2C connectivity without exposing the client to the network.
ZPA's secondary tunnel creates an alternative encrypted path specifically for users authorized to access VoIP and server-to-client applications. Network Connectors deployed at the datacenter or campus establish outbound connections to the Zero Trust Exchange (ZTE). The Zscaler Client Connector (ZCC) builds a secondary tunnel to the ZTE based on administrator-defined configuration parameters. The ZTE then integrates the ZCC and Network Connector connections, creating a complete end-to-end encrypted pathway — allowing S2C and VoIP traffic to flow securely without direct network access or VPN.
ZPA provides a structured migration path by introducing a VPN service layer specifically designed to handle exception traffic — VoIP, S2C applications, and other network-dependent legacy apps that cannot immediately be adapted to zero trust access. This allows organizations to consolidate their secure remote access onto the ZPA platform without disrupting access to critical legacy applications during migration. As applications are modernized or replaced, the exception traffic is progressively moved to full zero trust access, eliminating VPN entirely over time.
According to the Forrester Total Economic Impact study, ZPA customers have realized a 289% return on investment. This ROI is driven by reduced operational costs from VPN elimination, consolidated secure access infrastructure, lower complexity in managing remote access policies, and reduced security risk from eliminating implicit network trust. The study provides a detailed breakdown of cost savings and productivity gains that enterprise organizations can expect from a full ZPA deployment.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.