Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Extending Zero Trust for Workloads in Google Cloud and China Region

Global enterprise organizations are rapidly expanding their application footprints across multiple public clouds to leverage the unique capabilities of each cloud provider and mitigate lock-in risks. However, this multicloud adoption significantly expands the security risks. Unfortunately, legacy security architectures that retrofit on-premises models for multicloud are outdated and obsolete.
To address these challenges, Zscaler has extended its zero trust architecture to provide secure connectivity for the cloud workloads in Amazon Web Services (AWS) and Microsoft Azure. Today, we announce the availability of our Zscaler workload communications in the Google Cloud Platform, Azure public clouds in the China region, and AWS GovCloud along with our FedRamp certification. Customers can now confidently extend their deployments and benefit from the world’s largest inline cloud security platform with consistent security and segmentation policies.
China Region Support
Many industries such as technology, life sciences, and financial services are undergoing accelerated business transformations. They require deploying application workloads in public clouds closer to their employees for enhanced innovation and productivity. As organizations tap into the global footprint for resources and talent, we see a rapid rise in expansion into countries like China. They aim to provide consistent access and user experience to employees, regardless of their location. However, deploying workloads in public clouds for the China region poses the following challenges:
- Strict Great Firewall inspection (GFW)
- Random bandwidth throttling
- Spurious DNS injections for compliance enforcement
- Poor connectivity often with high packet loss and latency
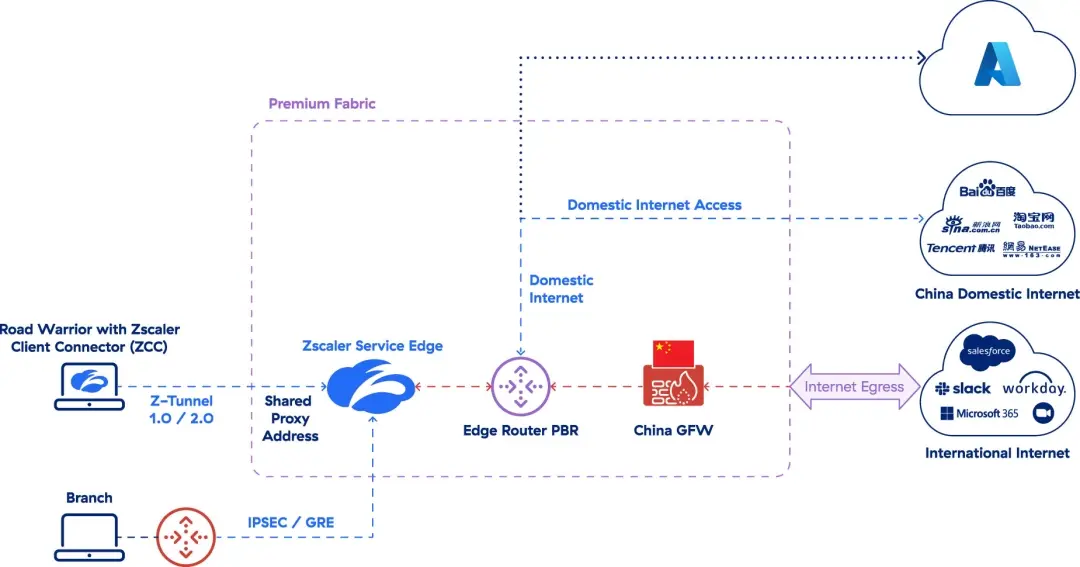
In response, Zscaler launched China premium access to help customers with enhanced connectivity and security. Many of our customers sought an extension of zero trust architecture for workloads deployed in public cloud regions of China, especially Microsoft Azure. Today, with this announcement, customers can now seamlessly extend cloud workloads to Azure Beijing and Hebei regions with the benefits of:
- Purpose-built workload communications for China regions adhering to all local compliance mandates
- Centralized and granular policy for workload egress traffic to domestic China or an international website
- Additional monitoring to maintain the country-specific risk and compliance requirements
GCP Support
Business transformation acceleration is happening across industry verticals with the adoption of modern application frameworks like microservices, serverless, and the new epoch of applications with Generative AI. One of Zscaler’s largest financial services customers embarked on a multicloud expansion with workloads deployed in Azure and GCP. Key drivers for the expansion were:
- Adopting GCP’s shared VPC architecture with granular workload egress security
- Enhancing the website chatbots based on Gen AI co-pilot with better security
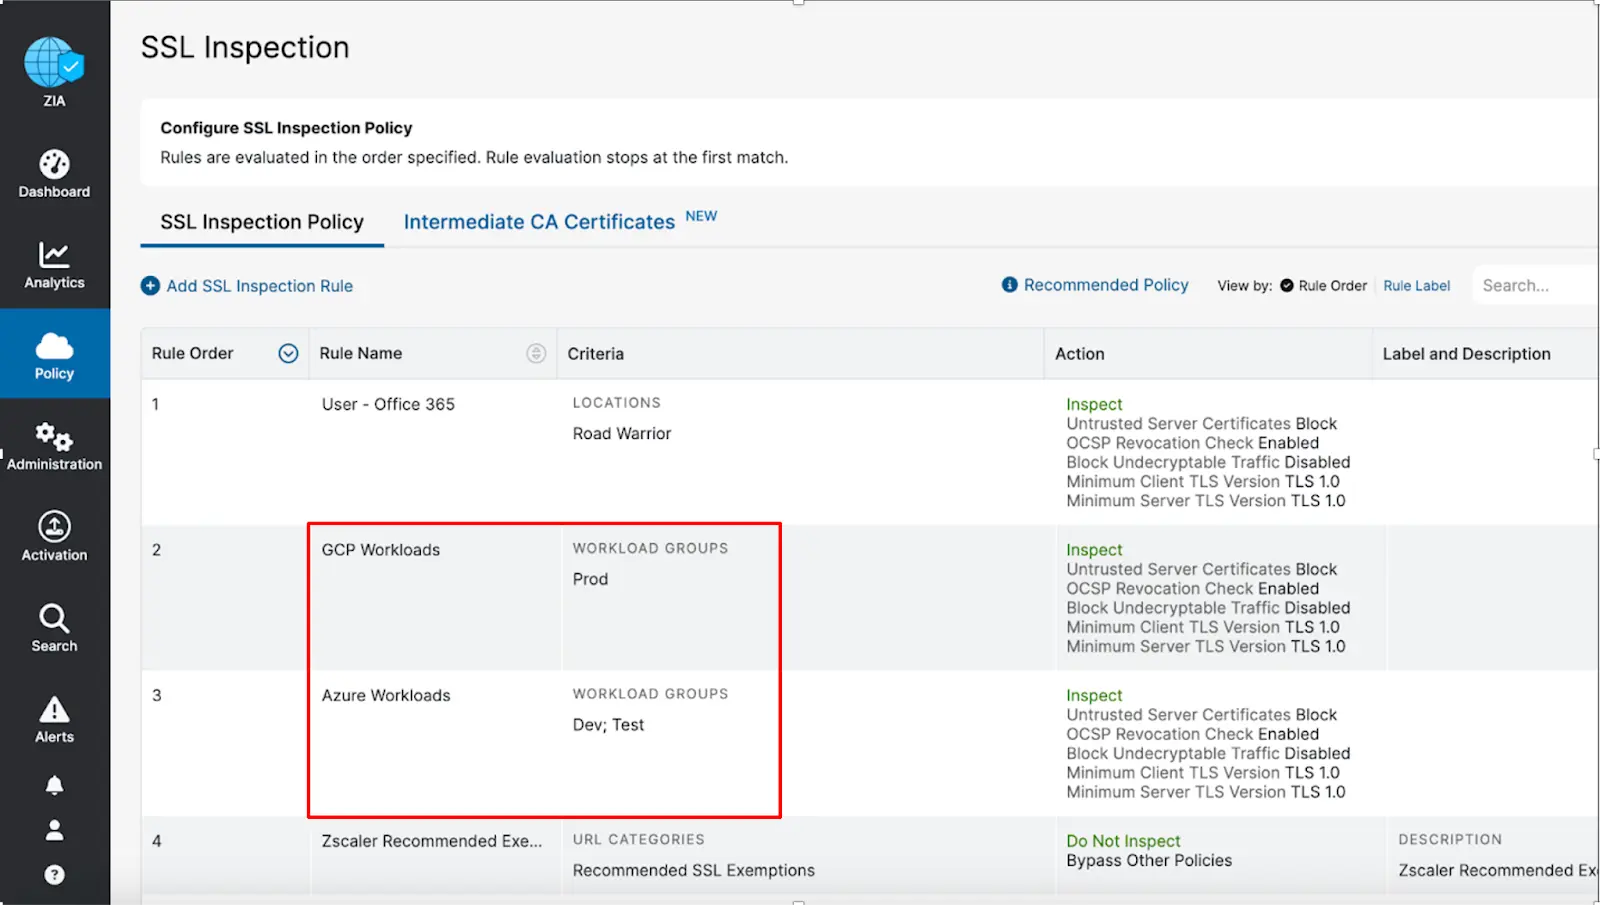
- Extending threat protection and SSL inspection capabilities
This customer has now deployed Zscaler Workload Communications in Azure and GCP with the single shared VPC and centralized infrastructure design. This flexible design enables workload deployments across multiple regions. They have benefited from minimal changes to existing network routing configurations, advanced policy-based SSL inspection, and strict data protection policies with inline SSL decryption for full visibility into Gen AI user queries and downloaded content.
In summary, these innovations and platform expansion for Zscaler Workload Communications will significantly improve business agility, end-user experience, and security for our customers’ workloads in multicloud.
To learn more about the capabilities of Workload Communications, visit the product page here.
Watch our launch event to hear more about our extended cloud support here.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.