Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Stop account compromise with Red Canary MDR and Okta
Red Canary detects identity-based threats and can respond automatically in Okta Workforce Identity.
This article was originally published by Red Canary, which is now part of Zscaler.
Stolen credentials were the most common path to a breach in 2021, according to the Verizon Data Breach Investigations Report. Requiring multi-factor authentication (MFA) during login significantly decreases the risk that stolen credentials will result in a breach. However, adversaries can still circumvent MFA—both in sophisticated ways as Microsoft observed recently, or by just overwhelming the user with push notifications, as detailed by Recorded Future.
To help you detect and respond to credential compromises before they result in a breach, Red Canary is excited to reveal an expanded integration with Okta Workforce Identity.
Detecting credential compromise using Okta Workforce Identity
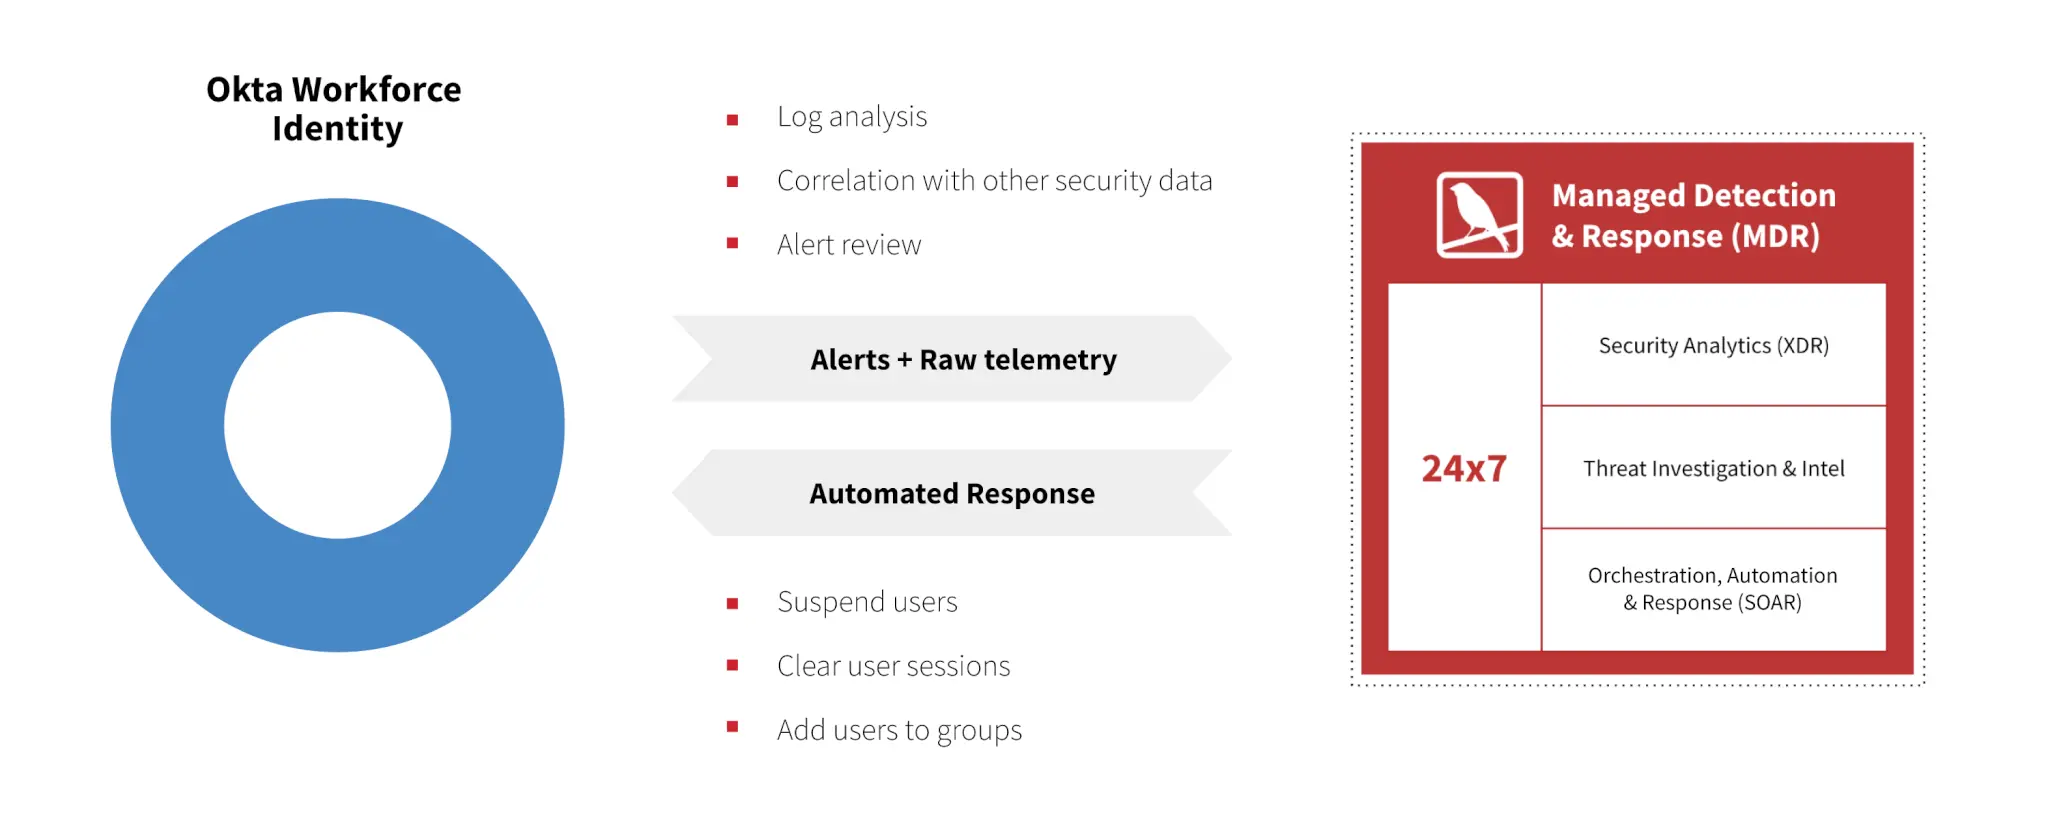
Red Canary detects credential compromise using Okta Workforce Identity in multiple ways. First, we’ll correlate information from your Workforce Identity alerts with relevant data from your other security tools. Maybe we detect that the identity that just initiated a password reset also recently clicked a phishing email. Or maybe one of your Okta admins escalates privileges to an identity that recently tried to access banned applications per your firewall. Because our XDR platform correlates information from across your enterprise, our detection engineers can review events with the proper context to quickly determine what alerts are benign or could indicate a threat.
We know the limitations of out-of-the-box alerts, which is why we now write our own detections specifically applied to Okta logs. We’ve already written detections to detect MFA fatigue intrusion attempts, and we will continue writing Okta-specific detections to catch threats that Workforce Identity alone would miss.
Responding to credential compromise using Okta Workforce Identity
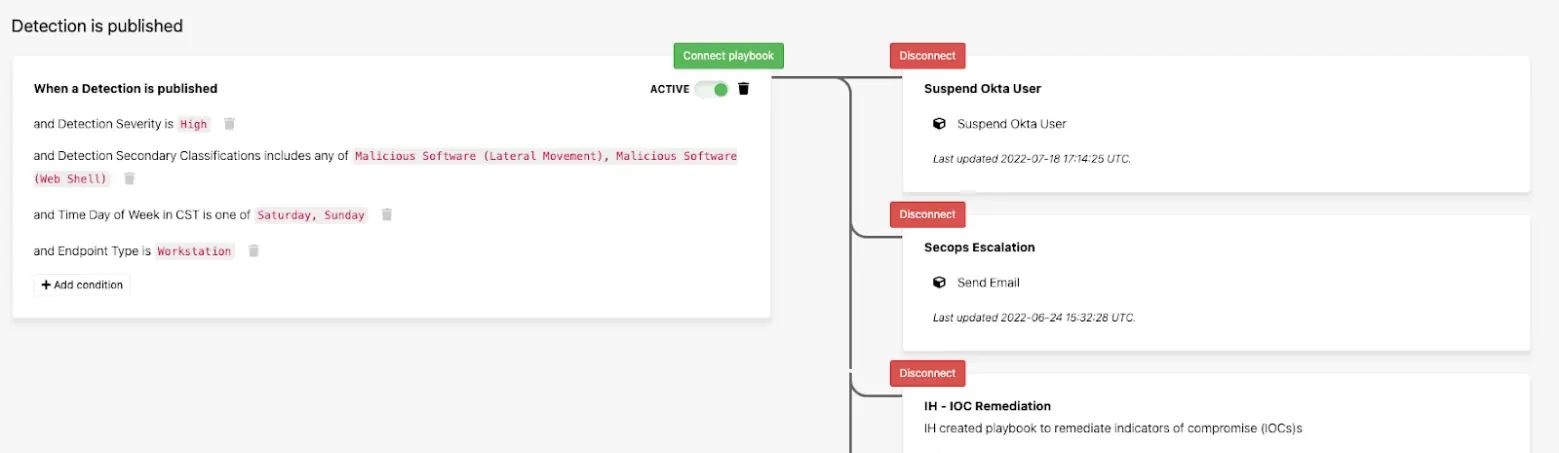
When we determine that a user’s credentials are stolen our built-in SOAR platform allows you to easily configure automated responses in Okta. No coding is needed: you can set up the responses entirely with Boolean logic and visual playbooks. We enable you to configure automated responses in Okta Workforce Identity for any Red Canary detection in which an Okta identity is implicated, not just detections we confirm via Workforce Identity alerts or logs. For example, you could set up a playbook such that anytime Red Canary detects malicious software on a device, the associated Okta user is suspended and added to an Okta group with access restrictions. It’s also easy to set up a playbook that clears a user’s sessions, forcing them to authenticate on their next operation anytime Red Canary associates an Okta user with a threat of any severity level.
Red Canary MDR ensures that you’re staying ahead of credential abuse in your environment by detecting account takeover threats early and helping you respond automatically in Okta. To learn more about Red Canary and how we work with Okta and other identity technology providers, feel free to schedule a demo or talk to one of our experts.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.
더 많은 Zscaler 블로그 살펴보기

New: Use response actions to update Zscaler policies and block threats
The key of AI: How Agentic Tuning can make your detection strategy sing
Accelerate investigation and response with Red Canary and Zscaler Internet Access
Clear skies ahead with Wiz visibility and Red Canary MDR
