Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
The Productivity and Protection of Cloud Sandbox

In today's cybersecurity landscape, the challenge of new threats from unknown files is ever-growing, especially with targeted phishing, sophisticated malware, and attackers targeting newly published vulnerabilities. Many customers understand the critical need for scanning unknown files but often resort to alert-only actions due to productivity concerns while awaiting verdicts from Sandbox analysis. Recognizing the importance of robust defenses, Zscaler has enhanced its Sandbox with advanced quarantine, AI Instant Verdict, and isolation features to provide comprehensive protection against unknown files without compromising user experience by delivering disarmed content files immediately.
A fully patched VM for new threats
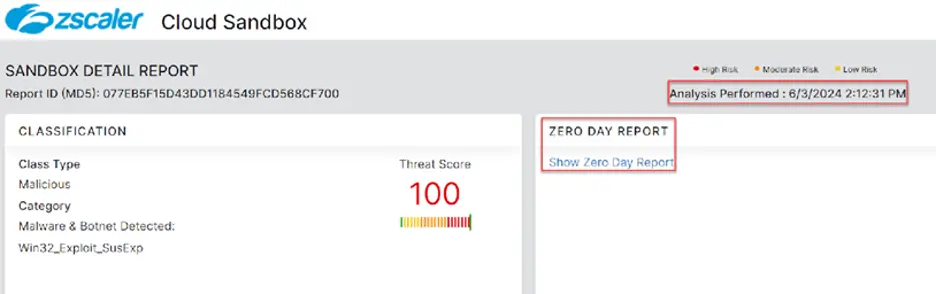
One of the standout features from our latest updates is the provision of two Sandbox reports for detonating unknown files. Initially, the file is detonated in a partially patched OS. If malware is detected with specific ThreatLabZ-maintained signature matches, the same malware is then rerun in a fully patched OS. This process ensures that the SOC team is alerted to critical detections that may be targeting newly announced vulnerabilities by Microsoft. The second report can easily be reviewed as show below from Sandbox reporting.
Enhanced Content Disarm and Reconstruction with Quarantine Action
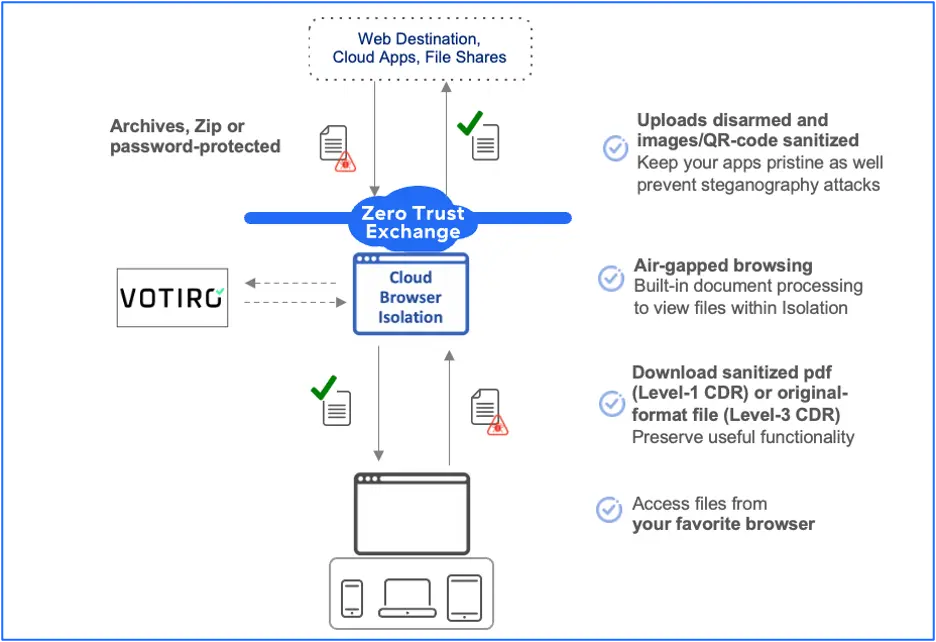
Zscaler recently announced an integration with Votiro, who deliver Content Disarm and Reconstruction (CDR) technology. This integration entails regeneration of file content by stripping out potential threats and reconstructing only safe, known good content. This guarantees the resulting original-format file is safe and fully functional for end users and apps to use. Even without Votiro, Zscaler will allow for flattened PDFs to be downloaded natively with Zscaler to eliminate file-based risk.
Cloud-Native Scalability
Consistent with our commitment to provide scalable solutions, the Zscaler Sandbox has been optimized for cloud-native environments with data centers the world over. This ensures that as your organization grows, our sandbox can effortlessly scale to meet increasing demands, without compromising on performance or security.
Enhanced File Analysis Capabilities
Our latest update includes expanded file analysis capabilities with larger file size limits, supporting a wider range of file types and formats. This allows for more comprehensive scanning and detection, ensuring that no potential threat goes unnoticed.
Sandbox file detonation flow
The Sandbox can be easily fine-tuned with flexible actions for various criteria, to offer enhanced coverage for files originating from suspicious sites and those sent to targeted employees. This ensures a more robust and adaptive security posture, effectively mitigating potential threats.
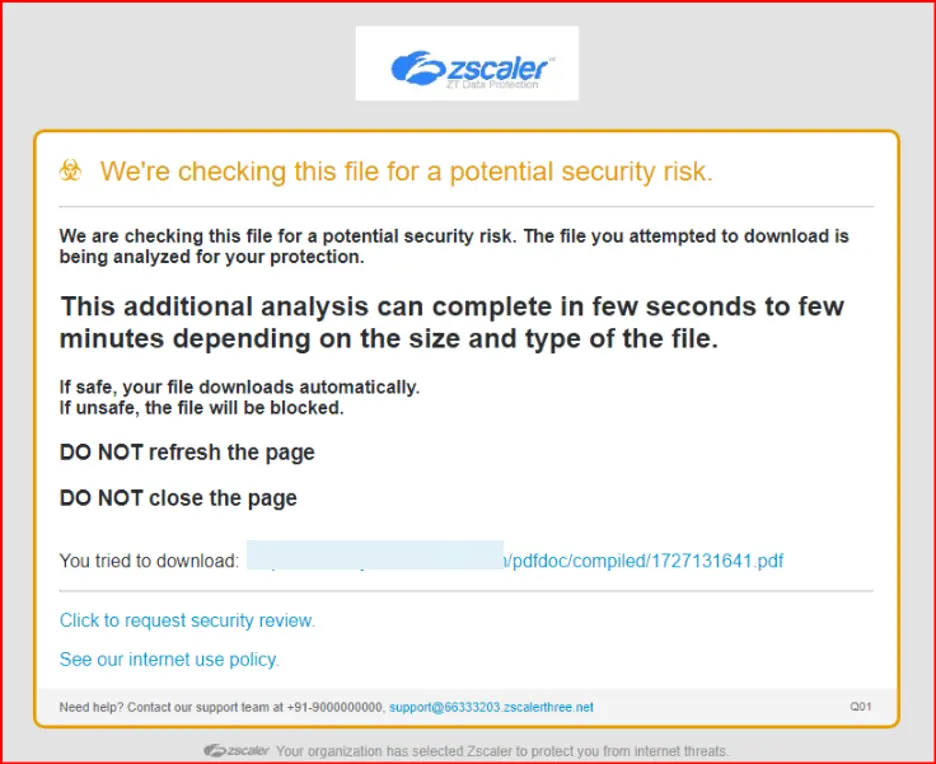
Let's focus on the flow with the Sandbox-Browser Isolation flow. Once the unknown file matches quarantine action, a customizable end user message appears to employees (seen below noting potential analysis wait time), making them aware of the pending sandbox verdict before the file is allowed to be downloaded. At this point the user is waiting for the file that they need for work, which is why a flattened PDF can be used immediately for productivity. If found benign, the original file is allowed to be downloaded.
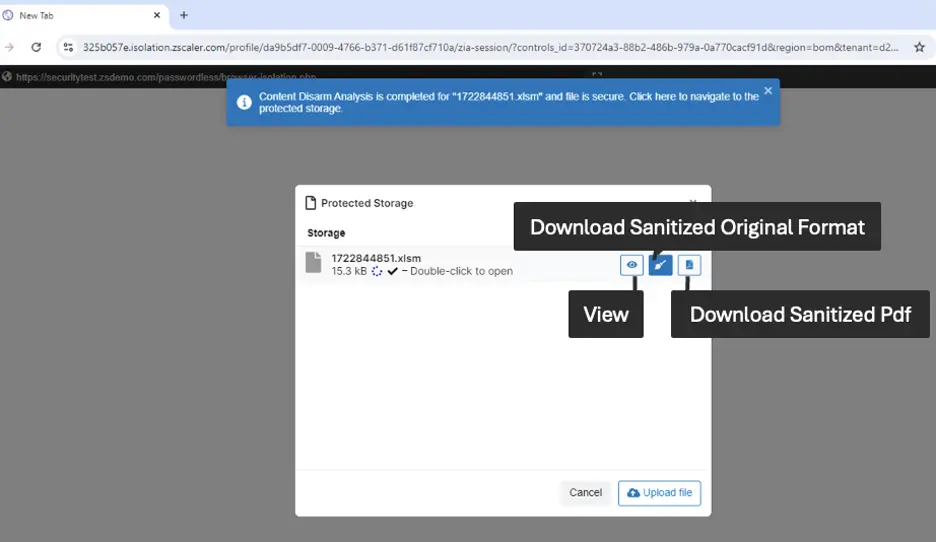
While this solution is great for comprehensive protection from unknown files, customers requested immediate sanitized file downloads to continue work rather than wait on the original file verdict from the Sandbox. Zscaler added the Isolation integration flow to ensure the Microsoft Office supported and PDF files are content disarmed for immediate download--and productivity. Recently, as mentioned, Zscaler also added the Votiro Integration to provide the industry-leading CDR, covering more file types and to bring the original file to users with malicious content removed for complying to best practices against file-based ransomware protection.
The end-user gets the full flexibility to choose among different options, within the Browser Isolation session, depending upon the use case requirements. Once the file is Sandbox scanned and found to be benign, the original file can be downloaded to ensure productivity with comprehensive protection against targeted attacks.
AI Instant Verdict and Isolation
How do Isolation and AI instant verdict working together help? AI Instant Verdict immediately detects high confidence malicious files (AI/ML threat Score 91-100) and blocks them in real-time. This increasing both the security and user experience in handling new file-based threats resulting to fewer Patient0 incidents for SOC teams. Immediate Access to flattened PDF file or content disarmed original file without waiting for final sandbox verdict or malware risk with Isolation making user productive without compromising security best practices.
The benefits of new enhancements
The enhancements to the Zscaler Sandbox are not just incremental improvements; they represent a significant leap forward in our ability to protect against sophisticated cyber threats. Here’s why these updates are crucial for your organization:
- Productive and Proactive Threat Detection: Advanced behavioral analysis and enhanced threat intelligence integration allow for earlier detection of threats, enabling proactive defense measures.
- Operational Efficiency: The improved user interface and reporting tools streamline the workflow for security teams, enhancing operational efficiency and response times.
- Scalability: The cloud-native architecture ensures that our solution can grow with your organization, providing consistent protection regardless of scale.
EDR and Inline Sandbox
EDRs like CrowdStrike offer sandboxing functions when an end user or device comes across a file their AI or algorithm deems suspicious. Combined with an inline cloud-gen sandbox, security and IT teams can leverage the Swiss Cheese Model to significantly reduce their risk posture. Now with tighter closed-loop integrations through CrowdStrike, newly detected threats or suspicious activity found within CrowdStrike Falcon Insight XDR will trigger workflows to change user group membership and apply adaptive access control policies through Zscaler. Network telemetry from Zscaler provides rich, continuous context for investigations. Instead of competing with one another, the bidirectional threat intelligence enables inline and endpoint sandboxes to complement each other.
Conclusion
At Zscaler, we understand that the cybersecurity landscape is constantly changing, and we are committed to evolving our solutions to meet these challenges head-on. The latest innovations in the Zscaler Sandbox are a testament to our relentless pursuit of excellence in cybersecurity.
Stay ahead of the curve and protect your organization with the enhanced Zscaler Sandbox. For more detailed insights and to see how these updates can benefit your security posture, visit our product insights blog.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


