
As more enterprises make the move to the public cloud, one of the most significant security threats to cloud infrastructure are often insider threats. They’re an inherent risk given the obvious reason that they are already part of the organization and they are considered to be trusted. The fundamental basis of how insider threats apply to a cloud environment relatively remains the same for a cloud environment, but given the dynamic and ephemeral nature of the public cloud, it opens up new opportunities for exploits. Given that enterprises now host mission-critical infrastructure in the cloud, the importance of protecting that infrastructure and mitigating the risk of insider threats is now high on security teams’ radar. In this blog post, we’ll describe and explore how using a cloud native application protection (CNAPP) and Secure Services Edge (SSE) platforms work in tandem to protect the cloud infrastructure from insider threats.
Insider risk and why they pose a risk to the cloud
One of the main challenges with insider threats to cloud security is that they are harder to detect and respond to given that they’re inherently considered to be “internal” or “trusted” resources. To avoid painting everyone with negative intent, there can certainly be instances where there is no perceived malicious intent, rather just negligence around how cloud resources are being configured. However, malicious insiders can be motivated by intentional data theft and they have the benefit of having the luxury to conduct reconnaissance without setting off alarms for the most part.
How do CNAPP and SSE platforms help in this scenario?
Consider a simple scenario where an organization stores critical sensitive data in cloud-hosted storage buckets such as S3, and Azure blob on private buckets with access control policies in place. There are several ways to address these out of the box using tools such as Terraform, Cloudformation, Control Tower, and AWS SCPs to ensure that the cloud resources being spun up meet these guardrails and they’re outside the scope of this blog, but we can certainly ensure the resource itself is deployed and secured.
However, with privileged credentials, these resources can be modified to be made publicly available.
This is where a Cloud Native Application Protection Platform (CNAPP) such as Zscaler Posture Control is critical where we’re continuously monitoring cloud resources for changes to their security posture and are able to alert and notify the appropriate teams.
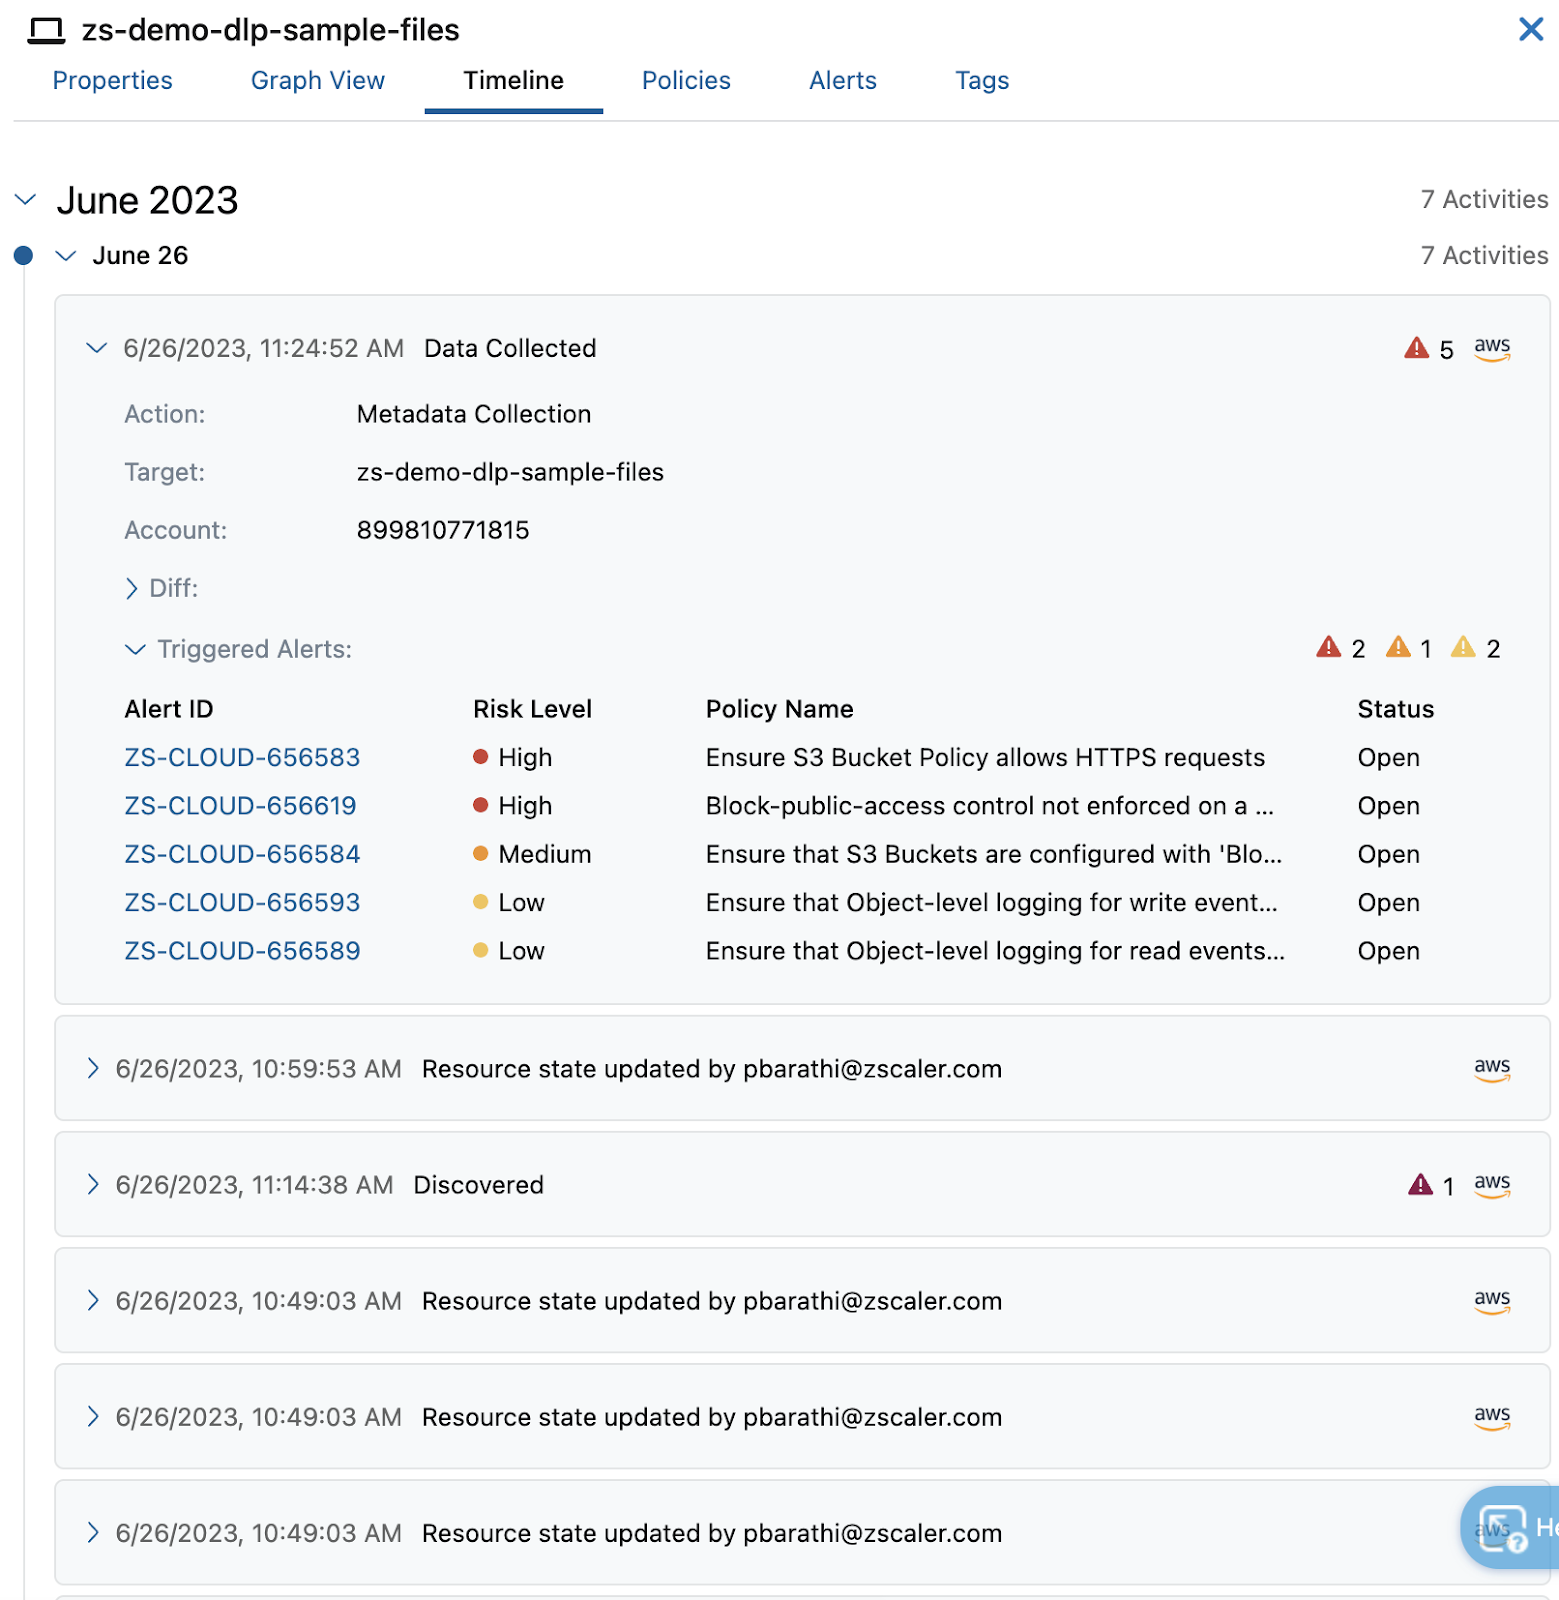
Fig 1. Asset information and timeline from Zscaler Posture Control
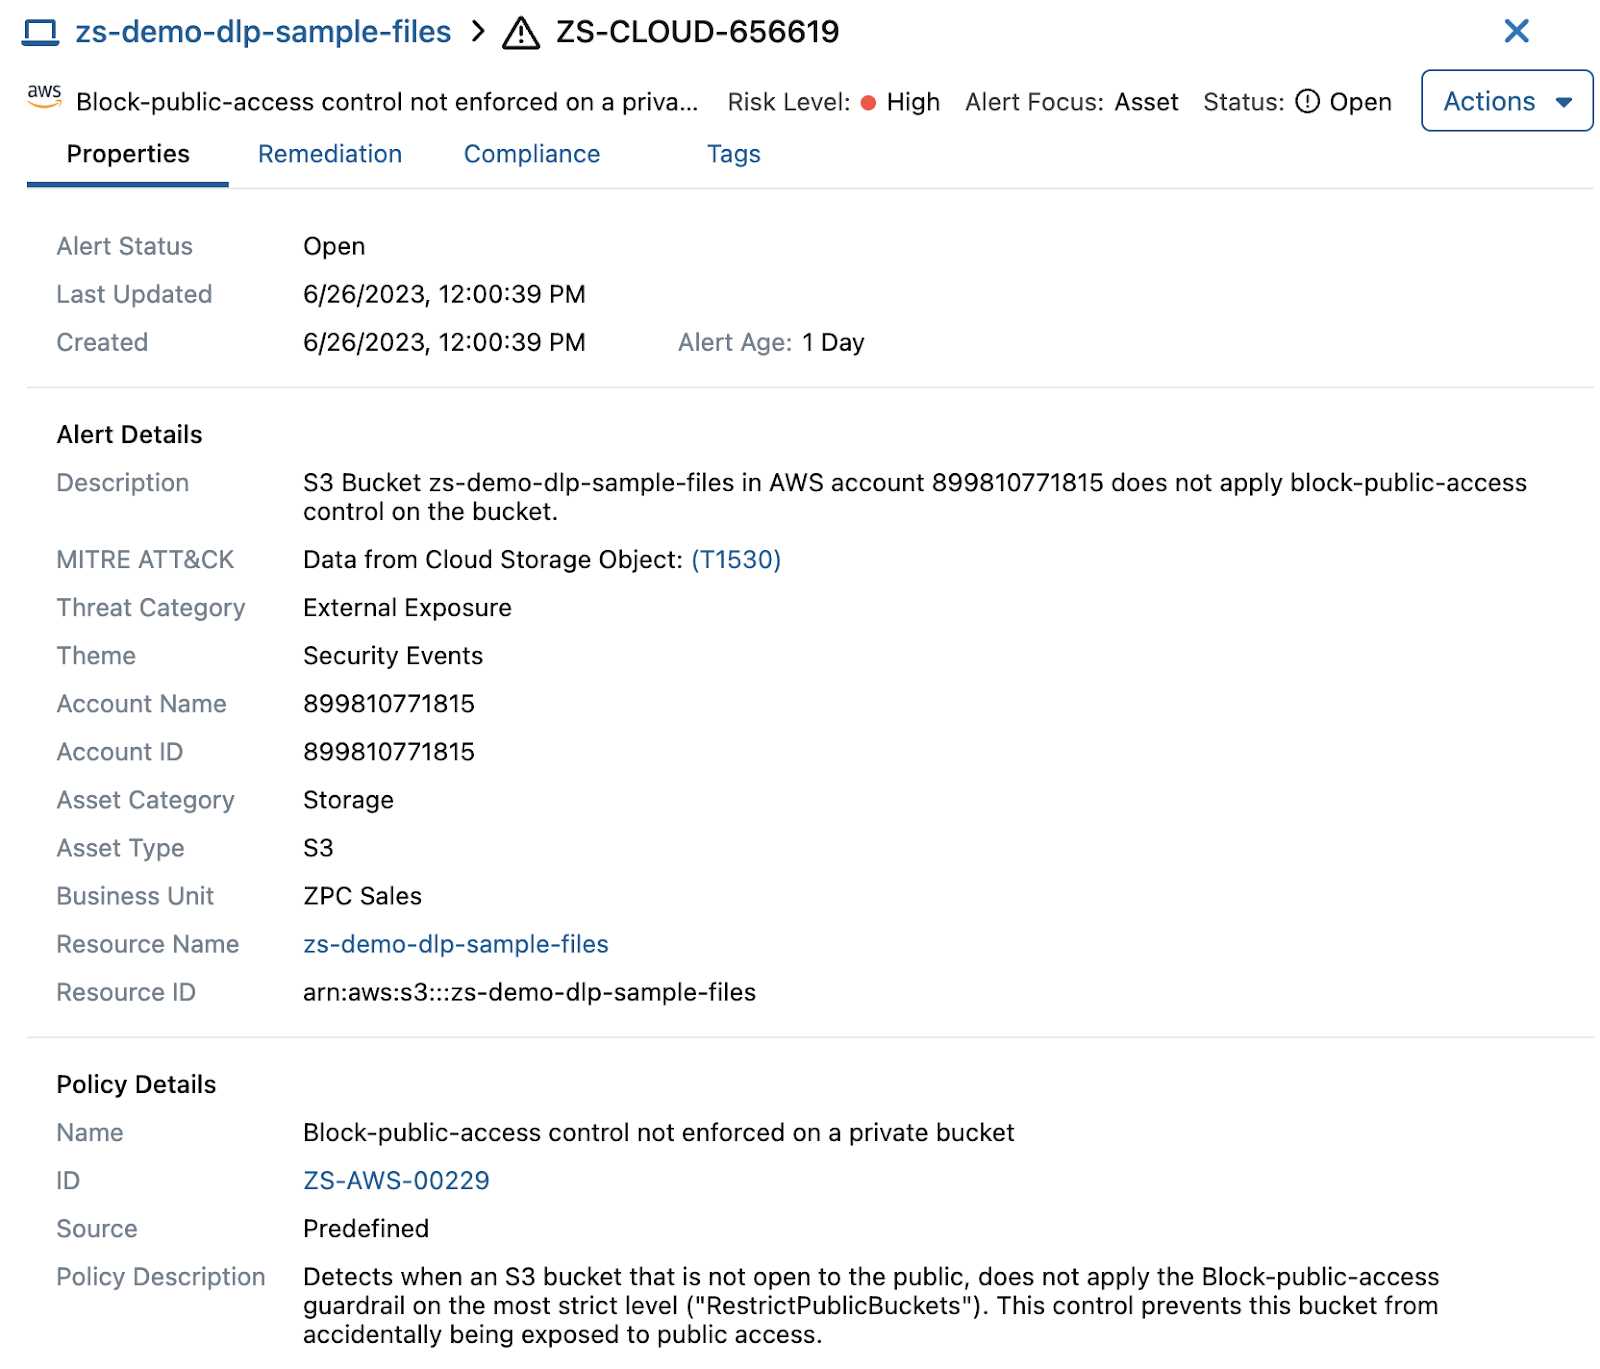
Fig 2. Alert details from Zscaler Posture Control
Not so quick!! Let’s not forget the next step of data exfiltration though. Once the bucket is publicly accessible, we now have the ability to download these sensitive files and potentially upload the files to external file hosting websites.
This is where an SSE platform comes into play to ensure that we’re offering inline data and threat protection for users and workloads. With the world's largest inline Security Cloud that Zscaler offers, we’re able to detect and block file uploads to external websites transparently.
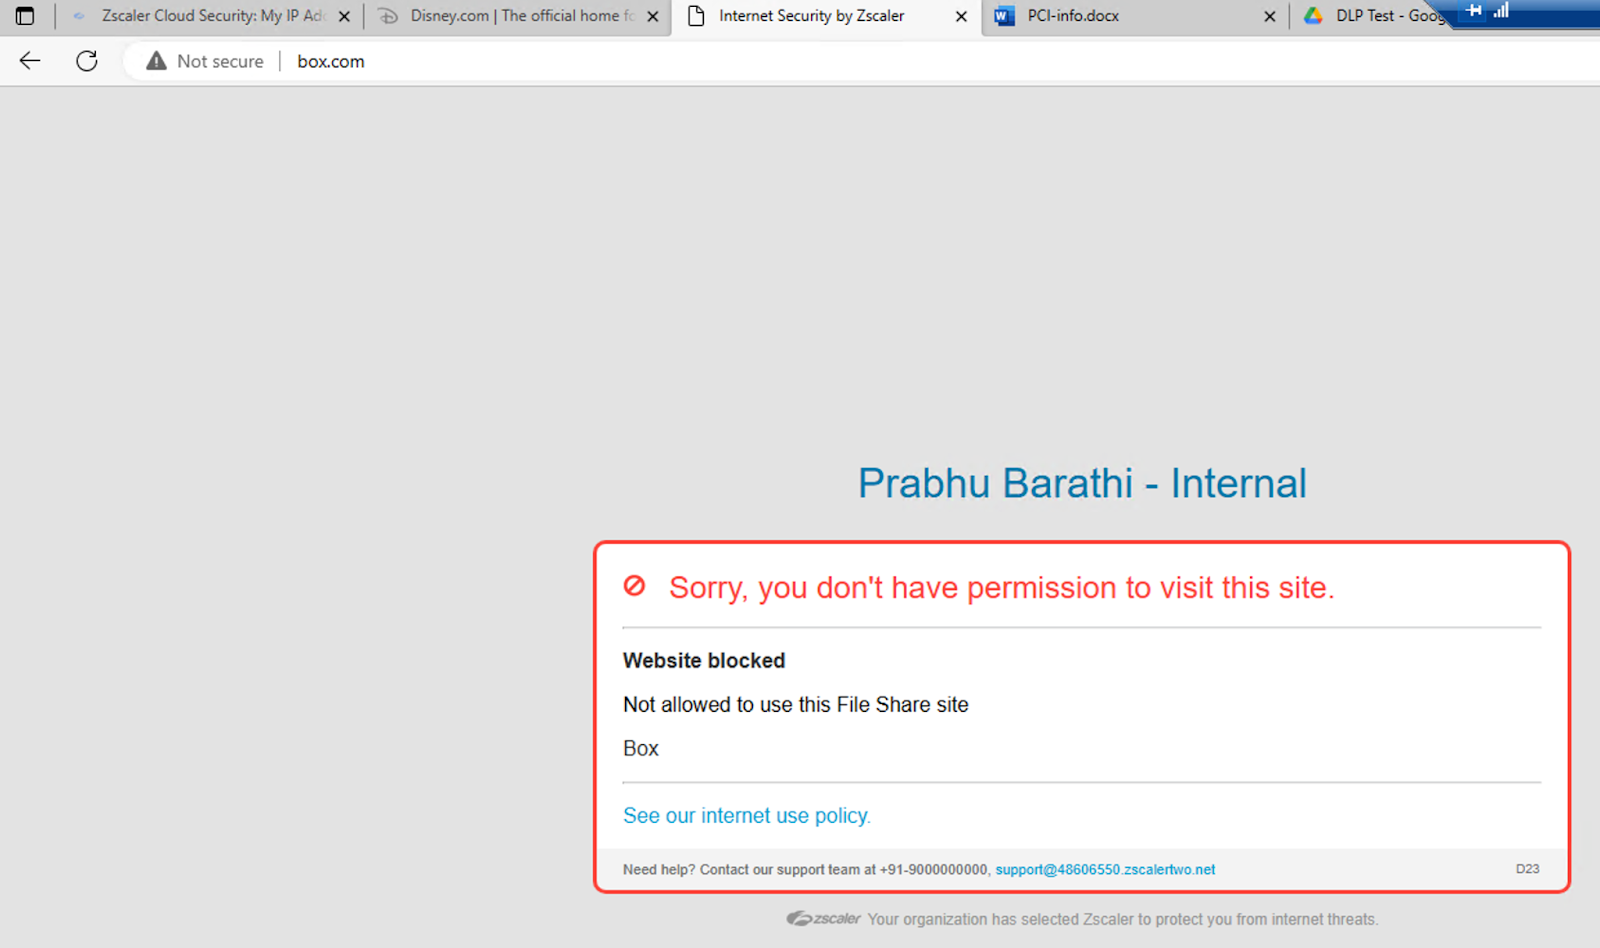
Fig 3. URL Filtering to block uploads to box.com
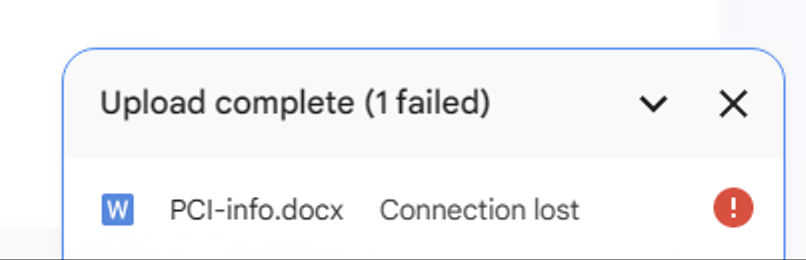
Fig 4. G-drive is allowed, however, we can block file uploads with PCI information on it.
To learn more about Zscaler Posture Control, download at a glance sheet or sign up for Free Cloud Risk Assessment to see Zscaler Posture Control in action.


