Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Reduce Your IT Anxiety: Secure Your Network with Zscaler Zero Trust Firewall

After more than a decade in the networking and security industry, I’m still amazed (and frankly, frustrated) by the constant news of hackers breaching organizations. Every other week, there’s a CVE vulnerability report from a next-gen firewall (NGFW) vendor, with a patch and a shrug, leaving it up to organizations to “do their part” to fix things.
Meanwhile, cybercriminals are thriving with AI-driven cyberthreats and subscription-based attack services on the darknet. Yes, for $50, anyone can buy an attack kit targeting well-known vulnerabilities. These threats exploit gaps in security measures, exposing sensitive data and leaving organizations vulnerable to unauthorized access.
So, what are security teams supposed to do?
The Evolution of Firewalls: From Stateful to Next-Gen Firewalls
Let’s rewind a bit. Remember the good old stateful firewalls? They worked on IP addresses alone, deciding to allow or block incoming and outgoing traffic based on those rules. Then came next-gen firewalls (NGFWs), which gave us deeper visibility into data packets and potential threats. Back then, when applications lived in data centers and traffic flowed through hub-and-spoke models, NGFWs were revolutionary.
Fast forward to today, where apps live across multiple public clouds, and most enterprise traffic is HTTPS. Physical NGFWs are struggling with scalability, and virtual NGFWs in the cloud aren’t much better. Both rely on limited computational resources, and spinning up more VMs doesn’t address the network perimeter challenges or improve network segmentation.
Here’s the kicker: whether physical or virtual, NGFWs expose your IP addresses to the internet, effectively giving hackers a map to your network. That’s not just a vulnerability—it’s an open invitation for unauthorized access.
Why Cloud Native Security Solutions Are the Cure for Modern Cyberthreats
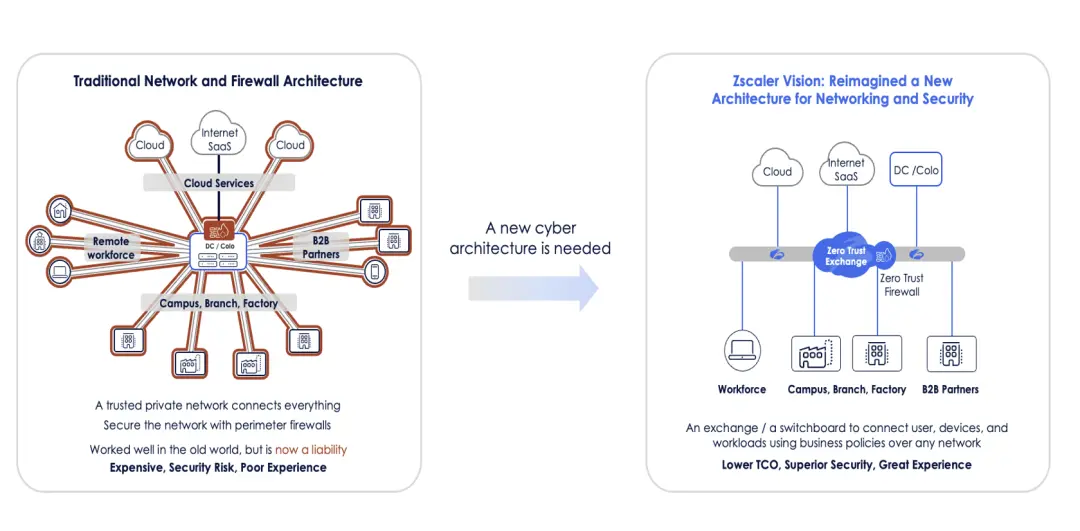
So, how do we fix this? The answer isn’t adding more firewalls or spinning up more VMs. It’s rethinking the approach entirely. A true solution is a cloud native security solution—built for the cloud from the ground up—not a virtual machine clumsily ported to the cloud. It should hide your IP addresses from the internet, stripping hackers of the information they rely on to attack your network.
And let’s not forget zero trust network access (ZTNA) principles. A firewall should continuously verify every connection, allowing only those explicitly permitted. This isn’t just about technology; it’s about reducing your stress, helping you get better sleep, do yoga, and maybe even take that vacation you’ve been putting off.
Enter Zscaler Zero Trust Firewall (ZTFW). ZTFW overcomes the constraints of NGFWs with a Zero Trust Firewall approach, removing implicit network trust and enforcing strict access control policies.
Unlike NGFWs, ZTFW does not rely on network-centric trust. Instead, it evaluates each access request based on user or device, context, and identity before allowing connections. The Zscaler Zero Trust Exchange (ZTE™) platform enables SSL inspection at scale and maintains performance by leveraging multitenant architecture, which supports over 500 billion transactions daily, 90% of which are encrypted. Moreover, Zscaler minimizes the attack surface by hiding public IPs of an organization. Applications and resources are hidden behind the Zscaler cloud, making them completely invisible to the internet.
The Zscaler Zero Trust Firewall Difference
Standard vs. Advanced ZTFW
Zscaler offers two types of firewalls under the ZTFW license tiers:
- Standard: Basic security measures with up to 10 firewall rules and 64 DNS rules.
- Advanced: Full-scale protection with 1,000+ rules, deep packet inspection (DPI), intrusion prevention system (IPS), DNS tunnel detection, and more.
If you’re serious about security, the Advanced license is the way to go.
Why Advanced ZTFW Stands Out
Here’s why Advanced ZTFW is worth the upgrade:
- DNS protection: Stops DNS-based threats like tunneling and spoofing with machine learning-driven insights.
- Intrusion prevention system (IPS): Protects against non-web threats like brute-force attacks and file-sharing exploits.
- Granular rules: Customize over 1,000 firewall and DNS rules for specific use cases (e.g., financial data compliance).
- Deep packet inspection: Detects hidden malware and phishing attacks.
- Logging and compliance: Offers detailed logs for audits, incident responses, and regulatory compliance.
Why Upgrade to Advanced Zscaler Zero Trust Firewall
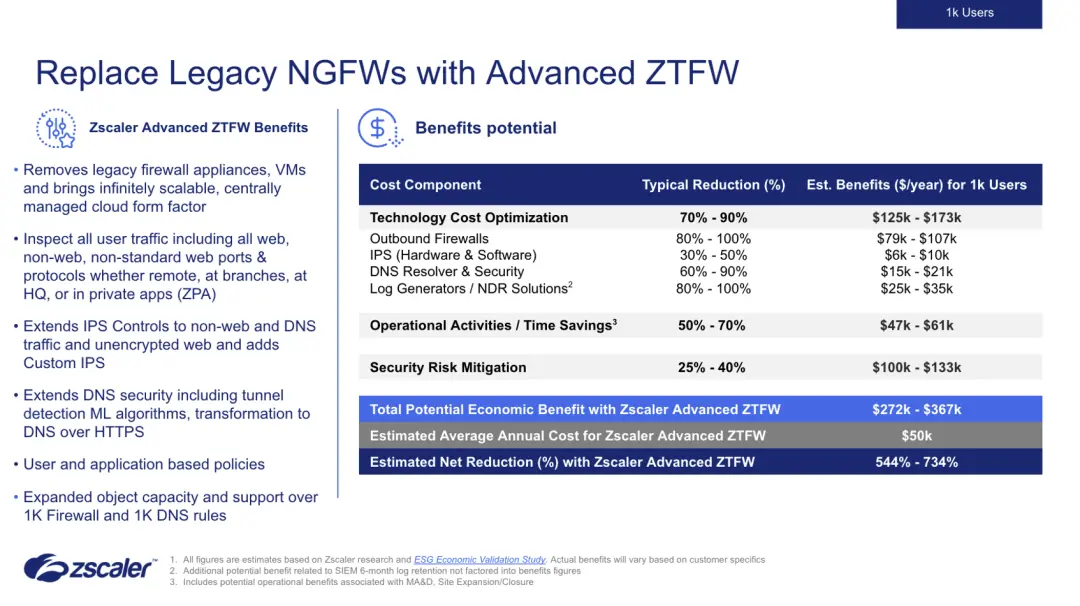
Beyond superior security, Advanced ZTFW can streamline your operations and cut costs. By consolidating legacy firewalls into a unified, cloud-based solution, organizations with 1,000 users can save anywhere from $272,000 to $367,000 annually.
Advanced ZTFW is particularly beneficial for modern enterprises that have embraced remote work. It ensures privileged access to resources, protects sensitive data, and enforces network segmentation to restrict lateral movement of threats. Whether it’s securing users and devices or inspecting incoming and outgoing traffic, the Advanced ZTFW delivers unmatched protection.
Conclusion
As enterprises adopt cloud-first strategies, traditional NGFWs just can’t keep up. Zscaler Advanced ZTFW offers the modern, scalable, and secure solution organizations need. By combining a cloud native architecture with Zero Trust Firewall principles, it ensures comprehensive protection, seamless scalability, and reduced complexity.
To schedule a demo of Advanced ZTFW, please visit here.
If you are interested in taking the Advanced ZTFW for a test drive, visit the link above and click on “Take an interactive firewall tour” at the top of the page.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


