Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Secure Shadow Data in the Cloud with New Innovations on Zscaler DSPM

A dark journey for data in the cloud
As we approach the end of 2024, the cloud and security landscape continues to evolve dramatically. Taking a walk down memory lane, I keenly remember the start of the cloud era back in the early 2000s. Fast forward to present day, the public cloud market is now projected to reach $1 trillion by 2026 with direct spend targeted at the big four: AWS, Microsoft Azure, Google Cloud, and Alibaba.1 This cloud journey comes with massive benefits with continual adoption, but it also comes with significant risks.
Data has become more distributed than ever, especially in multicloud environments, leaving room for sensitive data to go dark. In fact, according to research, 35% of breaches this year involved data stored in unmanaged data sources, or “shadow data.” This is due to the fact that cloud data is not being classified, managed, and protected properly. Breaches involving shadow data also took 26.2% longer to identify and 20.2% longer to contain, averaging 291 days. This resulted in higher breach costs averaging $5.27 million where shadow data was involved.2
Introducing new AI-powered innovations in Zscaler Data Security Posture Management (DSPM)
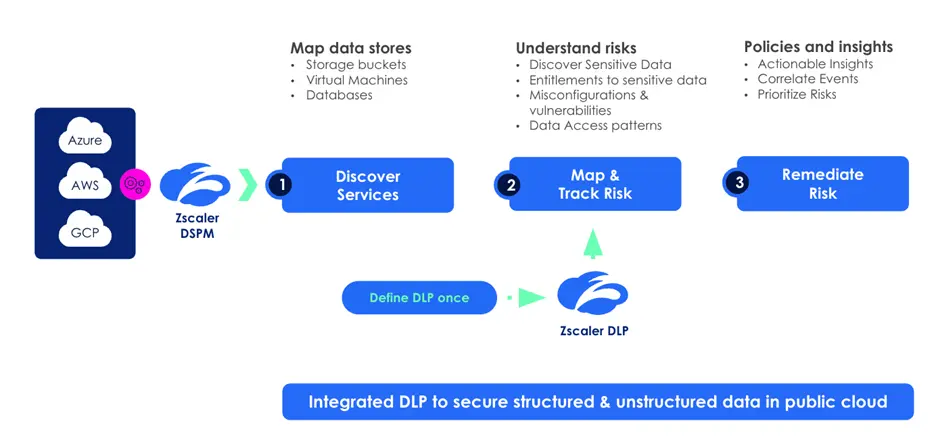
Figure 1: Zscaler DSPM
To combat today’s threats against shadow data in the cloud, we are excited to announce new AI-powered innovations within Zscaler DSPM.
With our new innovations, customers can:
- Automatically discover AWS shadow accounts: With zero-touch deployment, security teams can easily identify shadow AWS accounts and get a complete data classification view of all your data stores. You’ll get visibility of what data your teams are hosting in the cloud, which data stores they are using, and where the data is located from a geographical perspective. This allows IT teams to consolidate accounts to decrease cost and ensure any shadow data in dark accounts remain secure.
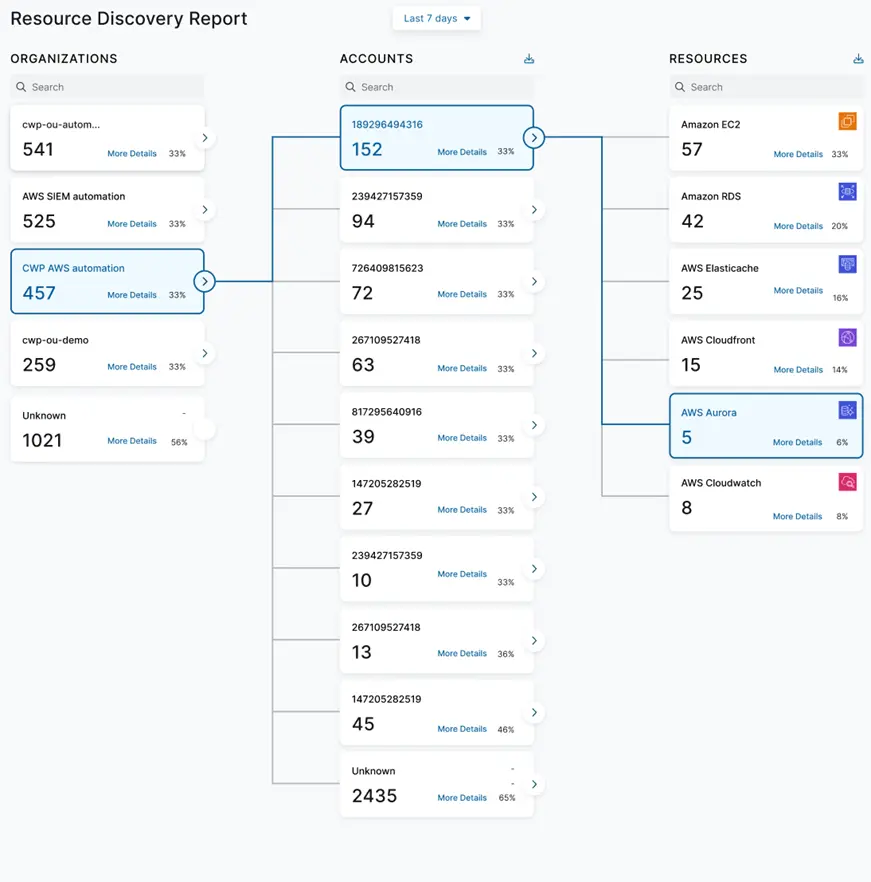
Figure 2: AWS resource discovery reporting
- Easily identify excessive entitlements and public exposure with AI: With AI-powered identity and access management (IAM), Zscaler DSPM can more seamlessly identify excessive and risky access paths for users and services and map sensitive data exposed to the internet. Zscaler DSPM now provides greater visibility to see who can access your sensitive data, who has accessed the data previously (with historical data), and get guided remediation steps to ensure secure access for all your sensitive cloud data.
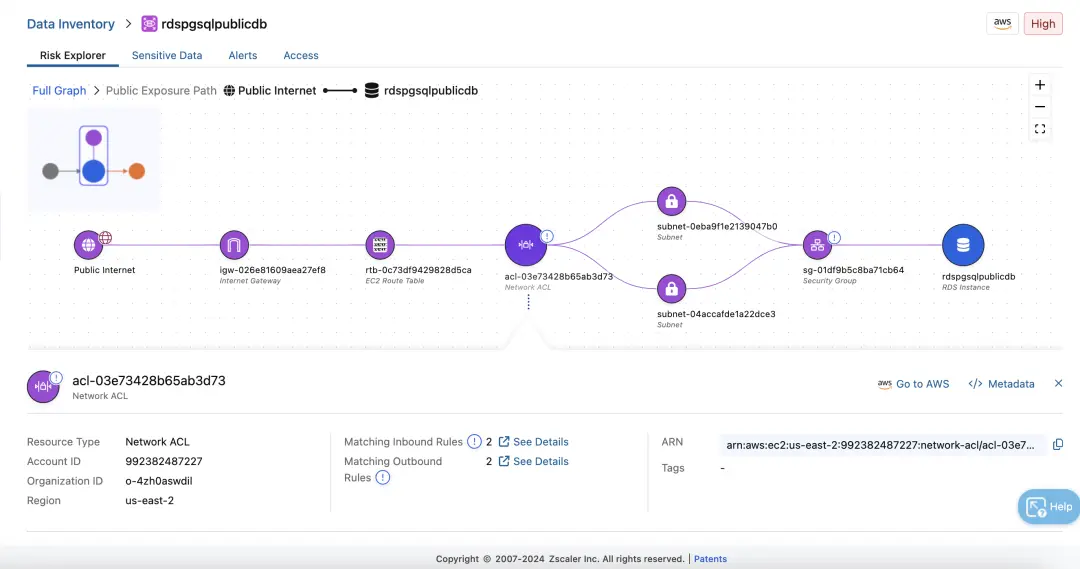
Figure 3: Public exposure mapping
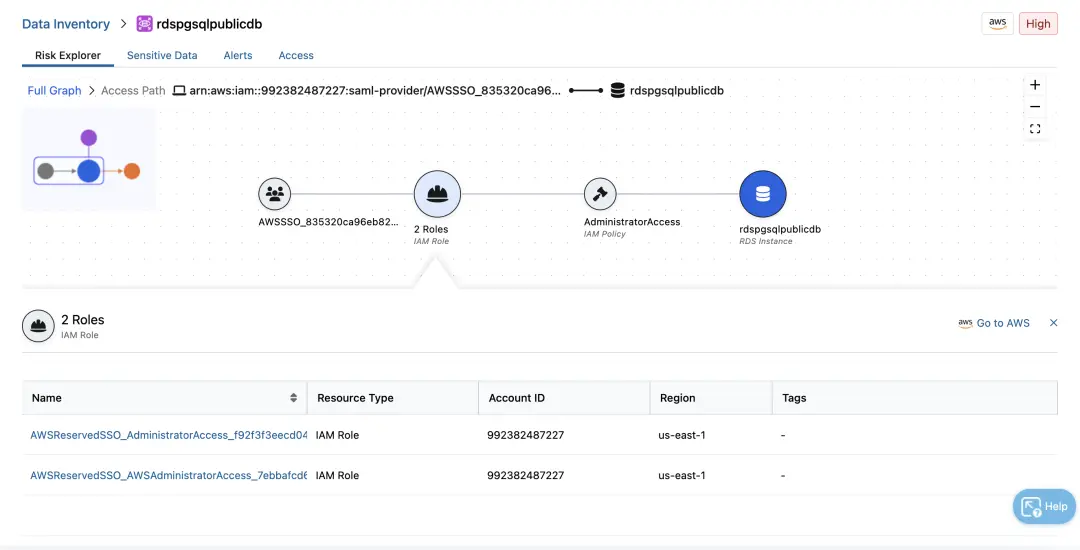
Figure 4: Access path
- Get expanded cloud services and platform coverage: Zscaler DSPM now extends its AI-powered data discovery capability to AWS’s top service DynamoDB, a fully managed, serverless, and highly scalable NoSQL database. We also expanded our cloud platform to support Google Cloud, one of the leading cloud providers in the world. With this new expanded coverage, we have the ability to secure structured and unstructured data stores in the top public clouds and services along with SaaS platforms.
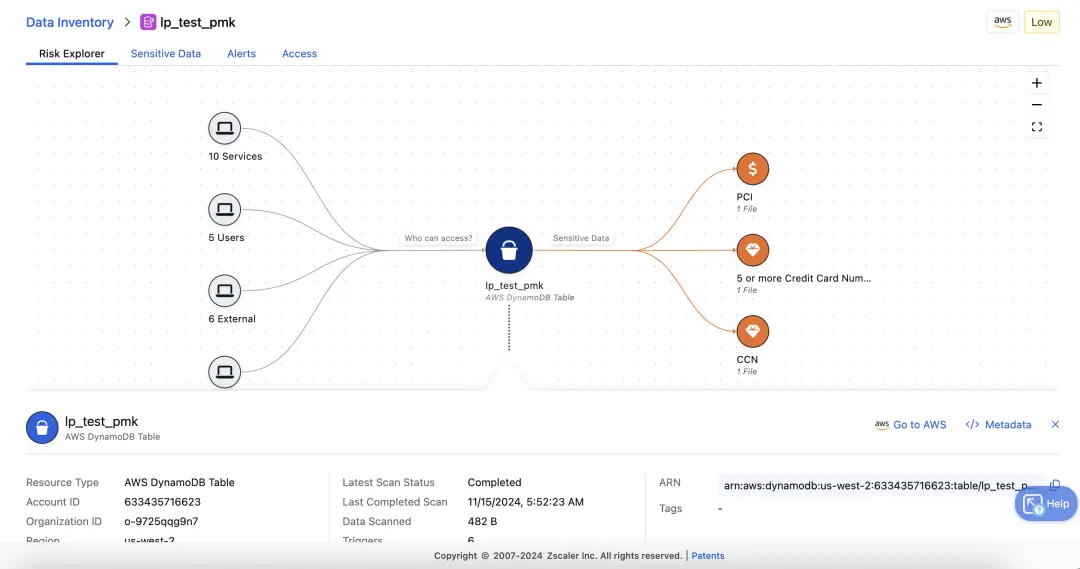
Figure 5: AWS DynamoDB table
Zscaler DSPM is fully integrated to the world's most comprehensive data protection platform that secures structured and unstructured data across web, SaaS, public clouds (AWS, Azure, GCP), private apps, email, and endpoints. Zscaler DSPM provides granular visibility into cloud data, classifies and identifies data and access, and contextualizes the exposure and security posture of data, empowering organizations and security teams to prevent and remediate cloud data breaches at scale. It uses a single, unified DLP engine to deliver consistent, best-in-class data protection across all channels and all types of data for in-motion, at-rest, and in-use.
Come visit the Zscaler booth at AWS Reinvent 2025 (Booth: 2057) for an in-person demo on our DSPM solution. Or join our upcoming webinar with AWS to hear more about our recent innovations on Zscaler DSPM. We can also set up a custom DSPM demo here.
References:
1 https://www.darkreading.com/cloud-security/rising-public-cloud-adoption-is-accelerating-shadow-data-risks
2 https://www.ibm.com/blog/hidden-risk-shadow-data-ai-higher-costs/

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


