Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Dive into the Red Canary Security Data Lake

Red Canary now offers cost-efficient data storage that improves your security posture
This article was originally published by Red Canary, which is now part of Zscaler.
Organizations need to achieve multiple objectives with their security data, with perhaps the most important being:
- threat detection
- threat investigation
- regulatory compliance
Threat detection often drives data storage decisions for the other two–if not all–security objectives, with SIEM products serving as a general security data storage hub. This approach to storage leads to common and recurring frustrations, such as:
- You need to comply with annual log retention policies, but your SIEM only retains logs for three months
- Most of the logs you’re storing in your expensive SIEM do not contribute to threat detection
- Neither your team nor your security service provider can efficiently query historical data during investigations and threat hunts
Not all data sources are equally valuable, and they shouldn’t be priced that way. That is why we are excited to announce the Red Canary Security Data Lake, a centralized and scalable repository for storing your high-volume, low-detection-value security data at a reasonable rate.

How it works
Set up integrations in minutes
If you can forward your logs to an AWS S3 bucket, or a Syslog server, you can add it to the Security Data Lake. We’ve tallied 200+ supported integrations spanning security products, cloud service providers, productivity software, and more.
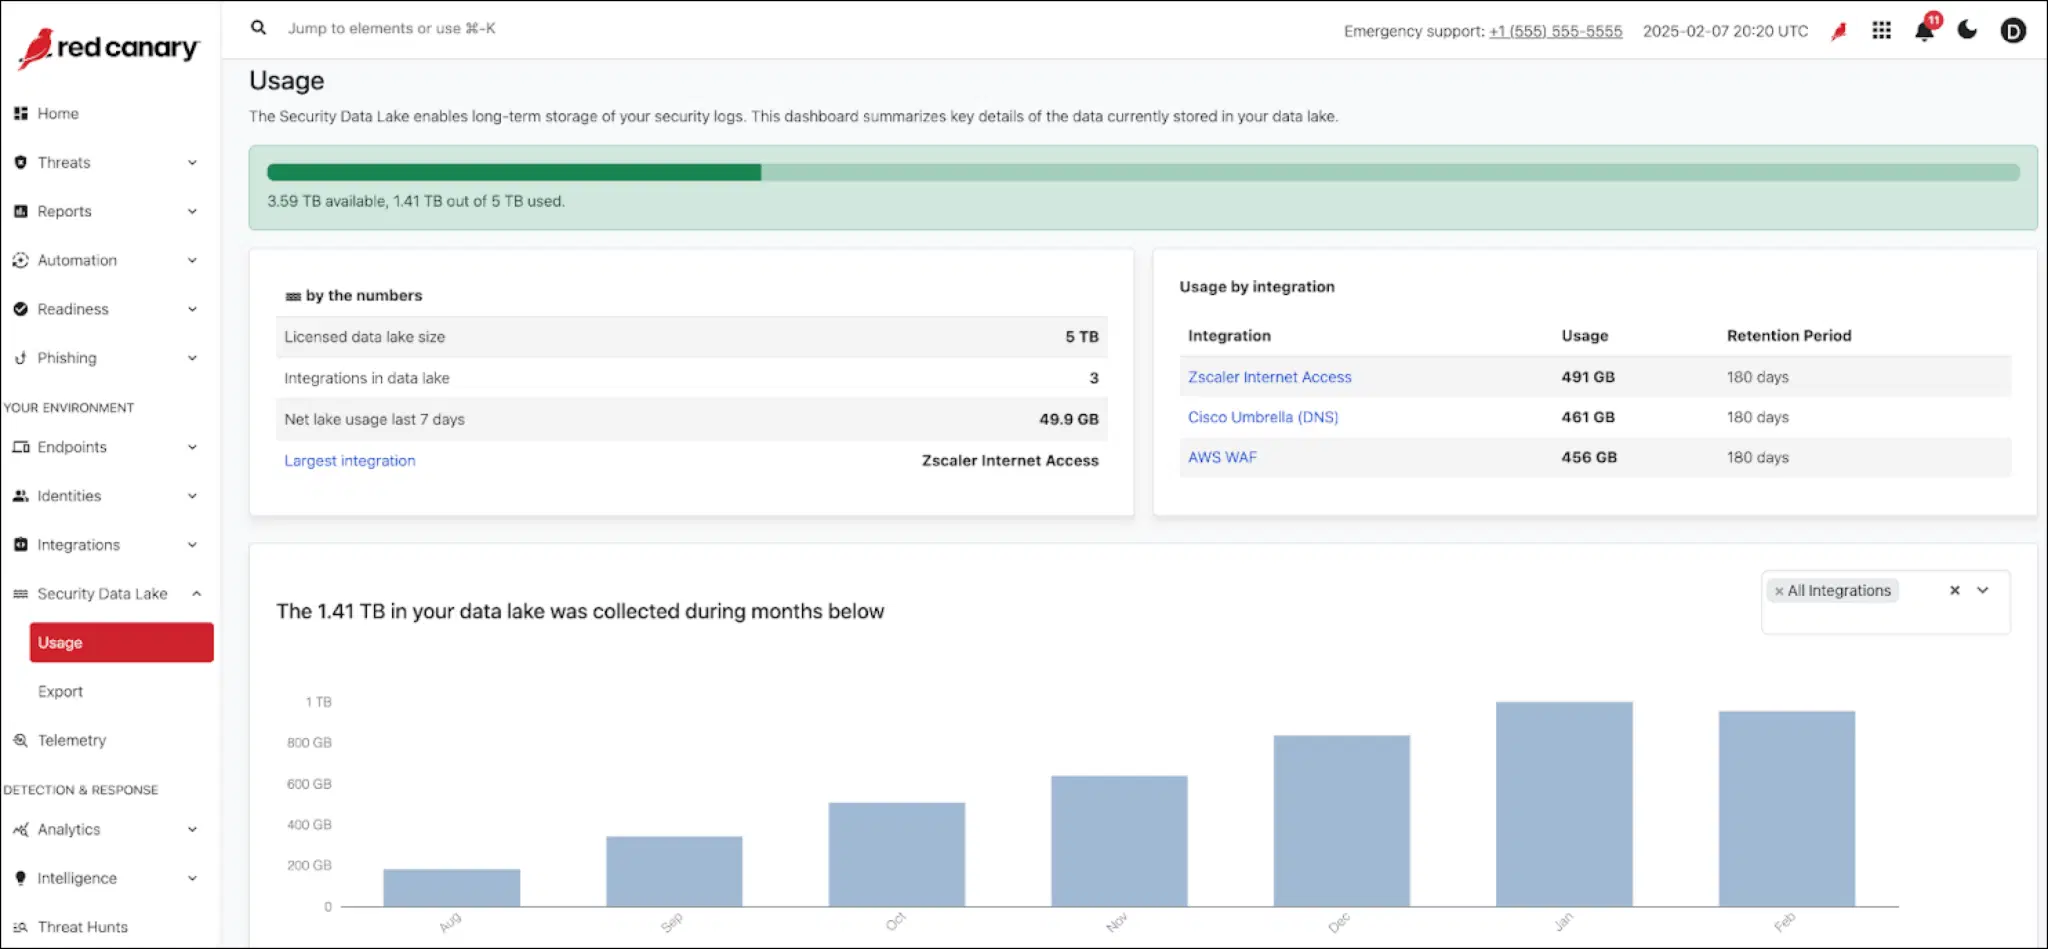
Demonstrate compliance
In many cases, just taking a screenshot is sufficient to prove certain logs are retained, but should you need to prove data retention to an auditor, we make it easy to find those logs and export.
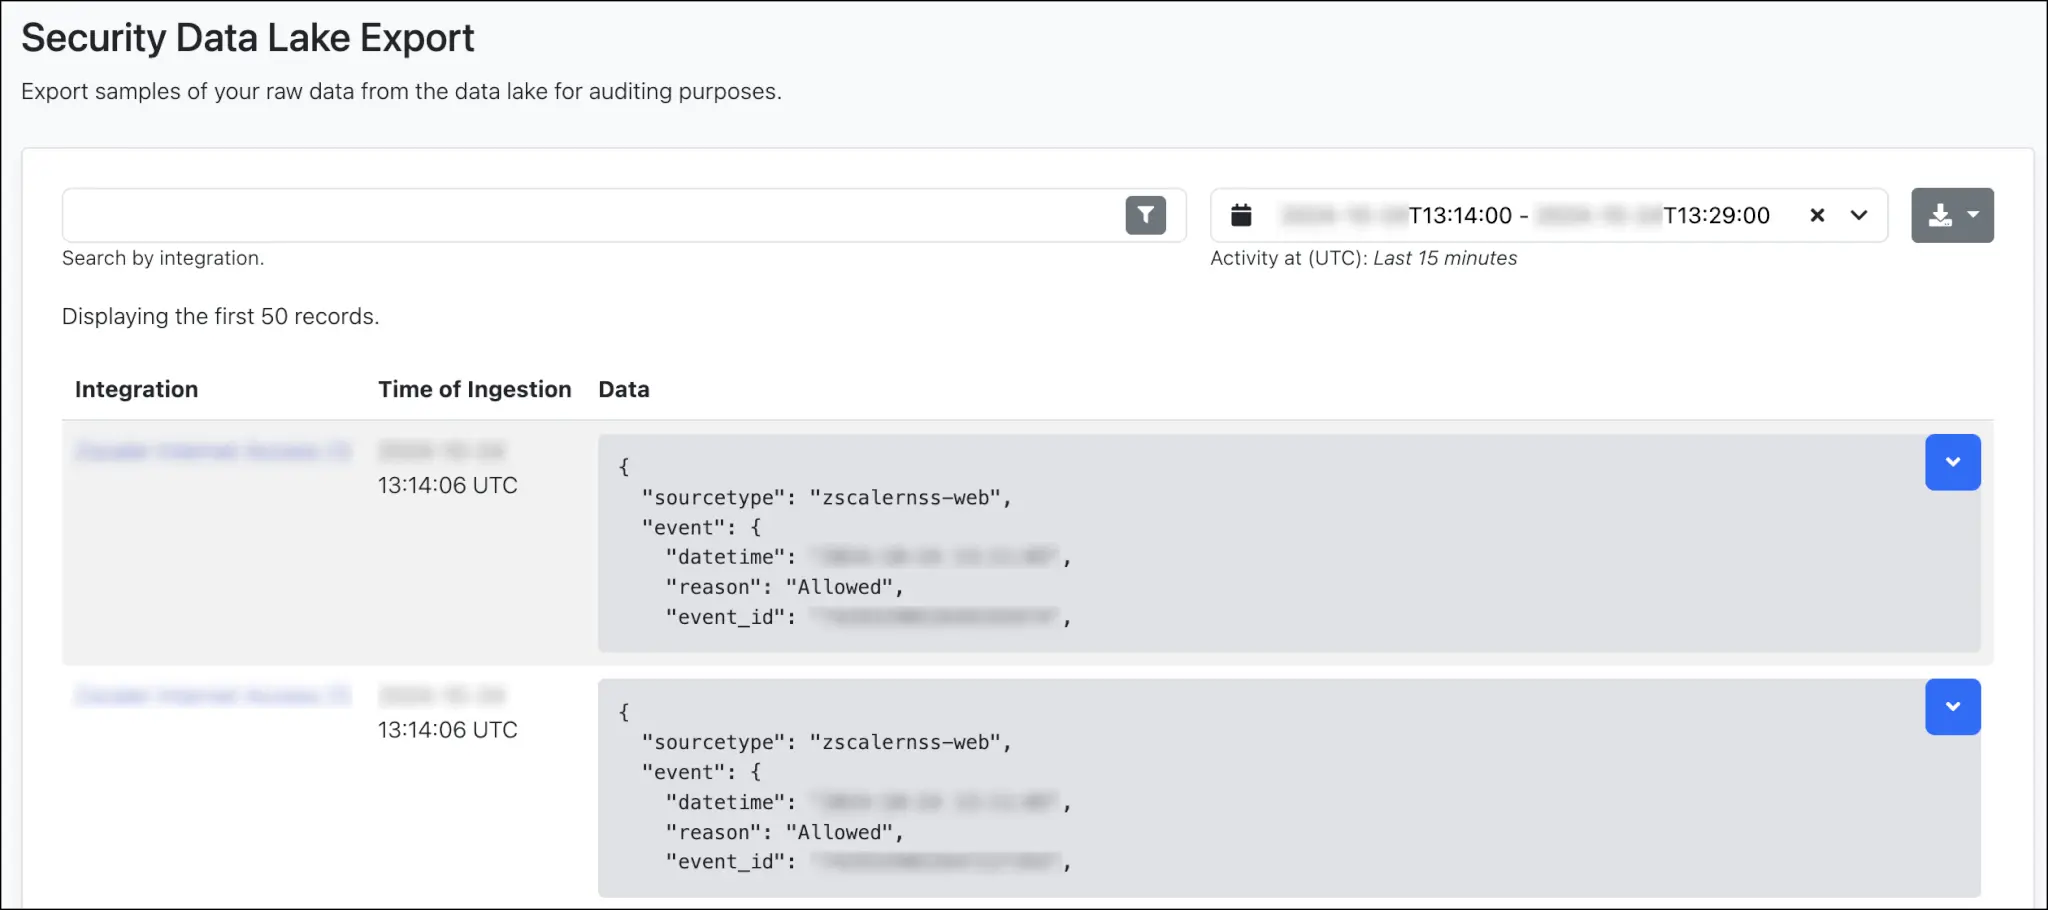
Investigate your data
You can write SQL queries directly against your supported data sources within the Red Canary platform. Search across all your logs for specific events, answer questions like “Is this normal or anomalous?”, aggregate data to identify trends, and perform complex analysis to uncover hidden threats—all with the familiar and powerful language of SQL.

Supercharge your MDR (coming soon)
Starting in Q3 in 2025, Red Canary analysts will be able to leverage your data in the Security Data Lake during MDR investigations. Over the course of this year, we will optimize our investigation workflows to leverage stored data throughout the detection and response lifecycle.
So what does this mean for you?
It means fewer dollars wasted. It means faster, more effective threat hunting and incident response. It means deeper, more actionable insights into your security posture.
see for yourself

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.
더 많은 Zscaler 블로그 살펴보기

New: Use response actions to update Zscaler policies and block threats
The key of AI: How Agentic Tuning can make your detection strategy sing
Accelerate investigation and response with Red Canary and Zscaler Internet Access
Clear skies ahead with Wiz visibility and Red Canary MDR
