
In my previous blog, we discussed how private equity companies swept in and bought end user computing (EUC) vendors. I highlighted how they raised prices, forced three-year contracts, and are still insecure to this day, even with the influx of cash flow from raising prices. Today we are going to explore the technical differences between virtual desktop infrastructure (VDI) and Zscaler.
Zscaler Client Connector is our single agent for all three of our Zscaler for Users products—one agent to rule them all. Client Connector is your gateway into our cloud, and we have more than 150 data centers worldwide so we can do SSL inspection, DLP, private application access, URL filtering, NGAV, and cloud firewall, just to name a few capabilities at scale. We ensure your users connect to the closest cloud vs. backhauling them to certain data centers. We can log in seamlessly and integrate with your SAML providers such as Okta or Azure Active Directory. We keep it simple so that your clinicians never have to worry about whether they logged in today, while you have the peace of mind of security always being on.
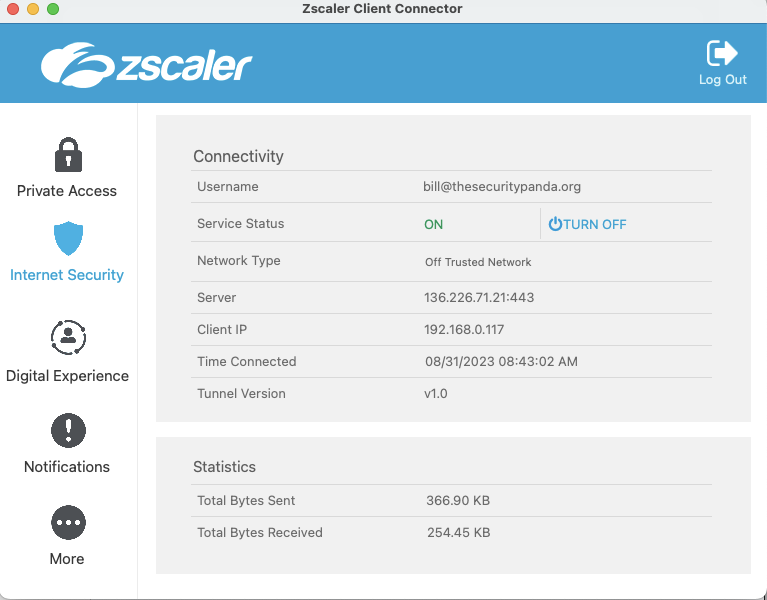
You don’t even need to do anything different when employees come into the office. No logouts like a VPN or switching profiles. Zscaler Client Connector dynamically switches policies based on your trusted and untrusted network postures. I don’t remember a single EUC vendor providing all of that in one single agent/connector.
Not only are we talking about replacing your VDI vendors, but also the possibility of consolidating your security tool stack. Sure, you may be thinking, "I have a lot of those IoMT devices that can’t have the Zscaler Client Connector installed on them." But you probably couldn’t get connectivity back with your VDI vendor either. We have a solution for that. We call it Zscaler Branch Connector—a lightweight appliance that allows your IoMT devices to talk back to your network no matter where they are located and, most importantly, keeps them secure. The best part is both of these give you zero trust capabilities. We do not connect your users to the network. Instead, we connect them directly to the application and they have no visibility into your underlying network.
Electronic health record (EHR) access is important, but so is your radiologists getting access to picture archiving and communication systems (PACS) to do diagnostic reads. I was told time and time again that VDI can do wet reads, and wet reads only, due to pixel compression, jitter, and a variety of other reasons why that can cause an image to get slightly skewed. VDI could not guarantee the images would be pixel-perfect, and the alternative was VPN, which was usually much slower than being on the network.
Zscaler Client Connector connects to our Zero Trust Exchange cloud while you have an App Connector at your data center or in the cloud that sits adjacent to your application. The App Connector talks outbound only to our Zero Trust Exchange and the cloud stitches the connections together. This means a faster connection as you no longer are traveling all the way to the data center, but meeting somewhere in the middle instead. It can’t be that much faster, right?
Zscaler not only has latency SLAs, but we also have another product called Zscaler Digital Experience that will tell you the exact latency between me and my application so IT can easily troubleshoot. You can finally know if it is your network, DNS, or your user's ISP that they didn’t know was having an outage. My lab is hosted in Texas and I live in Maine. On average, I get 20 ms or less latency. If you know anything about Maine, we are not known for blazing-fast internet. Again, one agent and I don’t remember EUC vendors only having one agent to do endpoint monitoring.
This is the power of Zscaler and why you should think about switching away from your VDI vendors.
Watch our recent webinar: Secure & Efficient EHR Delivery Without Expensive VDI/DaaS Contracts.
You can also find more information on our healthcare page.


