
Quikr Local Classifieds
 |
| Quikr app logo |
Price : Free
Category : Lifestyle/Shopping
Platform : iOS and Android
Updated : February 12, 2015(Android), 22 January 2015(iOS) Version : 7.42(Android), 2.8.2(iOS)
Size : 3.89 MB(Android),10 MB(iOS)
Language : English
Vendor : Quikr India
Background:
Quikr is India's largest online and mobile classifieds portal. Like Craigslist, Quikr provides the users with a platform to help them buy, sell, rent and advertise across multiple categories like real estate, jobs, entertainment, education, matrimonial, etc. Quikr also has a mobile app on both the Android and iOS platforms.
Application Chart (information retrieved from Appannie & xyo.net)
|
|
Android
|
iOS
|
|
Overall Ranking(India)
|
20
|
90
|
|
Category Ranking(India)
|
5 (Shopping)
|
8 (Lifestyle)
|
|
Total number of Downloads
|
12 Million
|
108 Thousand
|
|
Rating
|
4/5
|
3.5/5
|
A user is required to provide an email address and password when creating an account. After creating an account, the user can the post advertisements on Quikr. The application also provides functionality wherein different users can chat with each other.
Vulnerability - Clear text username/password
 The current version of Quikr mobile application has a serious data leakage vulnerability. It has been verified that both the current Android and iOS versions of the application are sending username and password information via the HTTP protocol in cleartext. This security vulnerability allows an attacker on the same network to capture the credentials sent by a Quikr user to the application server and thus compromise the user's account which may lead to posting fake ads on account owner's behalf, selling and buying products and sending spam messages via chat to other users.
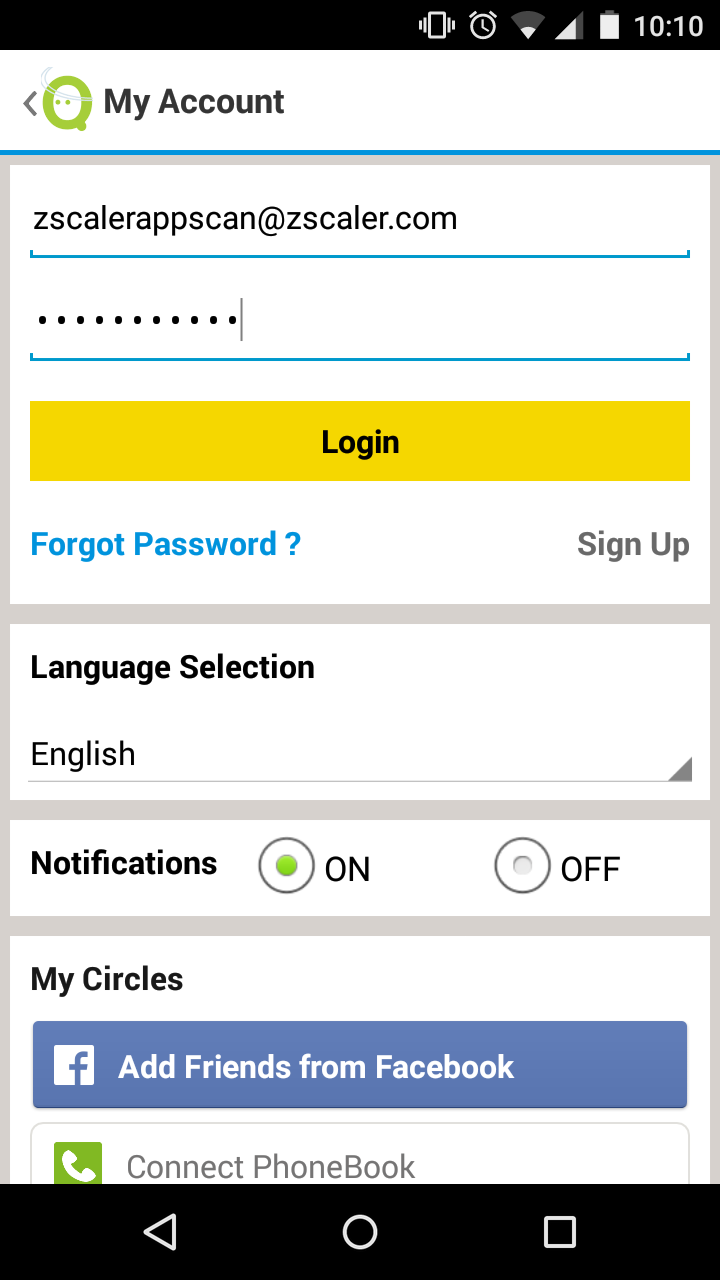 The current version of Quikr mobile application has a serious data leakage vulnerability. It has been verified that both the current Android and iOS versions of the application are sending username and password information via the HTTP protocol in cleartext. This security vulnerability allows an attacker on the same network to capture the credentials sent by a Quikr user to the application server and thus compromise the user's account which may lead to posting fake ads on account owner's behalf, selling and buying products and sending spam messages via chat to other users.
The flaw has been confirmed on versions 7.42 (latest versions available on Feb 12, 2015) on the Android platform and version 2.8 (latest version available on Jan 22, 2015) on the iOS platform.
Vulnerability in iOS version
When a user tries to register for an account in the Quikr application, an HTTP request is generated as shown below. In this request, the userid, password and mobile number of the user are sent in cleartext.
Account Registration:
[-] Method: POST
Url: http://services.quikr.com/api? method=registerUser&secCode=fd1f2276c71627c35e2a9c5f8838c09c&version=1.5
Host: services.quikr.com
User-Agent: Quikr/2.8.2 CFNetwork/711.1.16 Darwin/14.0.0
Request Body:cityId=23&userId=zscalerappscan%40zscaler.com&password=password123&mobile=9876543210&demail=969eac57dbfc4079a935fadf7ab261d6%40quikr.com
Server Response: AJBiY , N , .E]n3 , i^0%] , 1}qa , K;\OU4
Similarly, below is the traffic capture when an already existing user tries to login to their account. The userid and password are passed in cleartext.
Login:
[-] Method: POST
Url: http://services.quikr.com/api?method=login&secCode=fd1f2276c71627c35e2a9c5f8838c09c&version=1.5
Host: services.quikr.com
User-Agent: Quikr/2.8.2 CFNetwork/711.1.16 Darwin/14.0.0
Request Body: [email protected]&[email protected]&password=password123
Server Response: 1`QaL , B*RD , , ,
Vulnerability in Android version
We will first test the Quikr application installed on a Google Nexus tablet. The Quikr application version available in the Google Play store for the tablet was v6.9. Below is the sample traffic capture when a user tries to register a new Quikr account or login to their existing Quikr account.
Account Registration:
[-] Method: POST
Url: http://services.quikr.com/api?method=registerUser&version=1.5&secCode=zXcv80386Mdp1hs0q7o0p9uiLZV37TdF&consumerVersion=7.42&density=2.0&[email protected]
Host: services.quikr.com
User-Agent: QuikrConsumer
Request Body: --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="cityId" , , 23 , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="demail" , , [email protected] , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="mobile" , , 8234567890 , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="userId" , , [email protected] , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="opf" , , json , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="password" , , p@ssword123
Server Response: {"login":{"auth":1,"code":"usercreated","message":[{"direct":"New user created"}],"email":"[email protected]","mobile":"8234567890","city":"23","name":"","UserSession":"PGR8fU59OHVzOWMhfFI+fll0Qj5mdnIjRXd0Rm57T0dZPXw\/Q0RDYCE4amJ5L3R5PHVdTGpORSY6KDhjbl40LlliaztN","emailCRC":null,"cityName":"Bangalore","cityId":"23","app_notif_status":1,"sound_preference":1,"notif_alarmtime":"08:00 PM","userClassification":null,"isSharedPB":0,"isSharedFB":0,"userType":1,"numAlerts":0,"numAds":"0"}}
Login:
[-] Method: POST
Url: http://services.quikr.com/api?method=login&version=1.5&secCode=zXcv80386Mdp1hs0q7o0p9uiLZV37TdF&consumerVersion=7.42&density=2.0&[email protected]
Host: services.quikr.com
User-Agent: QuikrConsumer
Request Body: --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="demail" , , [email protected] , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="userId" , , [email protected] , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="opf" , , json , --s2retfgsGSRFsERFGHfgdfgw734yhFHW567TYHSrf4yarg , Content-Disposition: form-data; name="password" , , password123
Server Response: {"login":{"auth":1,"code":"success","message":[{"direct":"You are successfully logged in"}],"email":"[email protected]","mobile":"8234567890","city":"23","name":"","UserSession":"PGR8fU59OHVzOWMhfFI+fll0Qj5mdnIjRXd0Rm57T0dZPXw\/Q0RDYCE4amJ5L3R5PHVdTGpORSY6KDhjbl40LlliaztN","emailCRC":null,"cityName":"Bangalore","cityId":"23","app_notif_status":1,"sound_preference":1,"notif_alarmtime":"08:00 PM","userClassification":"0","isSharedPB":0,"isSharedFB":0,"userType":1,"numAlerts":0,"numAds":"0"}}
As you can see in the above requests, all communication between the mobile app and server is in sent via cleartext, which includes sensitive user information.
ZAP Analysis:
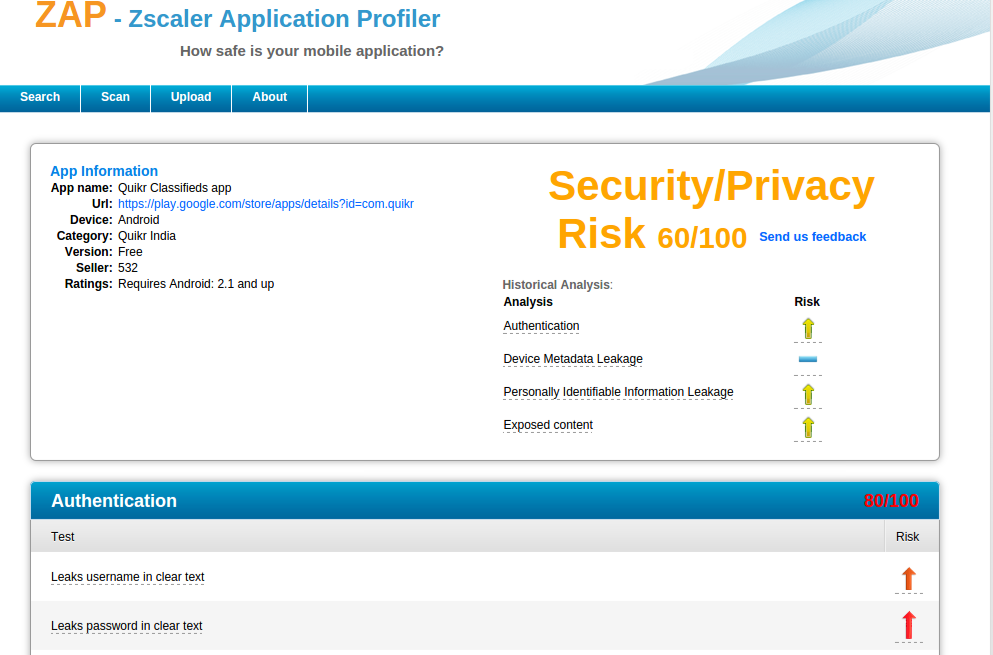 |
| ZAP in action - Android |
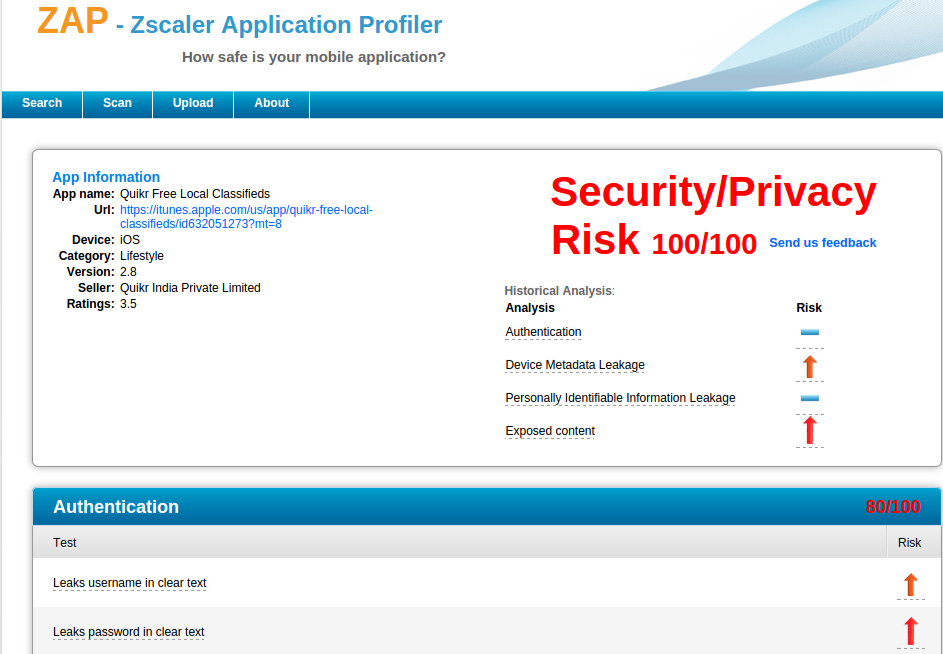 |
| ZAP in action - iOS |
Conclusion:
We continue to find new popular applications in the Apple and Google app stores that are leaking device data and sending out sensitive user information in cleartext. This is a good argument for the use of one time passwords when establishing accounts on mobile apps. As a user, you can never know with certainly if your credentials are being transmitted/stored securely. By leveraging a password manager and ensuring that passwords are unique for all apps, at least you can be assured that if your credentials are compromised due to poor app security, only that specific account will be impacted.
Credit: Lakshmi Devi.




