Overview
Give security practitioners and threat researchers easy access to policy-driven traffic captures and zero-trust telemetry for efficient security forensics and incident response—without requiring additional appliances.
- Unified visibility across hybrid environments
- Early threat detection with NDR
- Improve compliance and forensic readiness
THE PROBLEM
The cloud edge that protects your traffic also shields it from sensors meant to inspect it
Security teams need to understand the content traversing your environment to conduct effective forensic analysis, investigate incidents, and ensure compliance. Traditional PCAP solutions lose visibility when user traffic no longer crosses the physical sensors they depend on.

Cloud and remote traffic can create NDR blind spots
Remote and internet-bound traffic never reaches traditional corporate TAPs and sensors, limiting what NDR tools can analyze.
Fragmented context slows investigations
When packet data, identity, access, and security telemetry live in separate workflows, analysts spend time correlating evidence instead of investigating.

High capture and storage overhead drives up costs
Legacy PCAP solutions collect traffic indiscriminately, which increases bandwidth, storage, and infrastructure costs.
SOLUTION OVERVIEW
Feed high-fidelity traffic to your NDR of choice
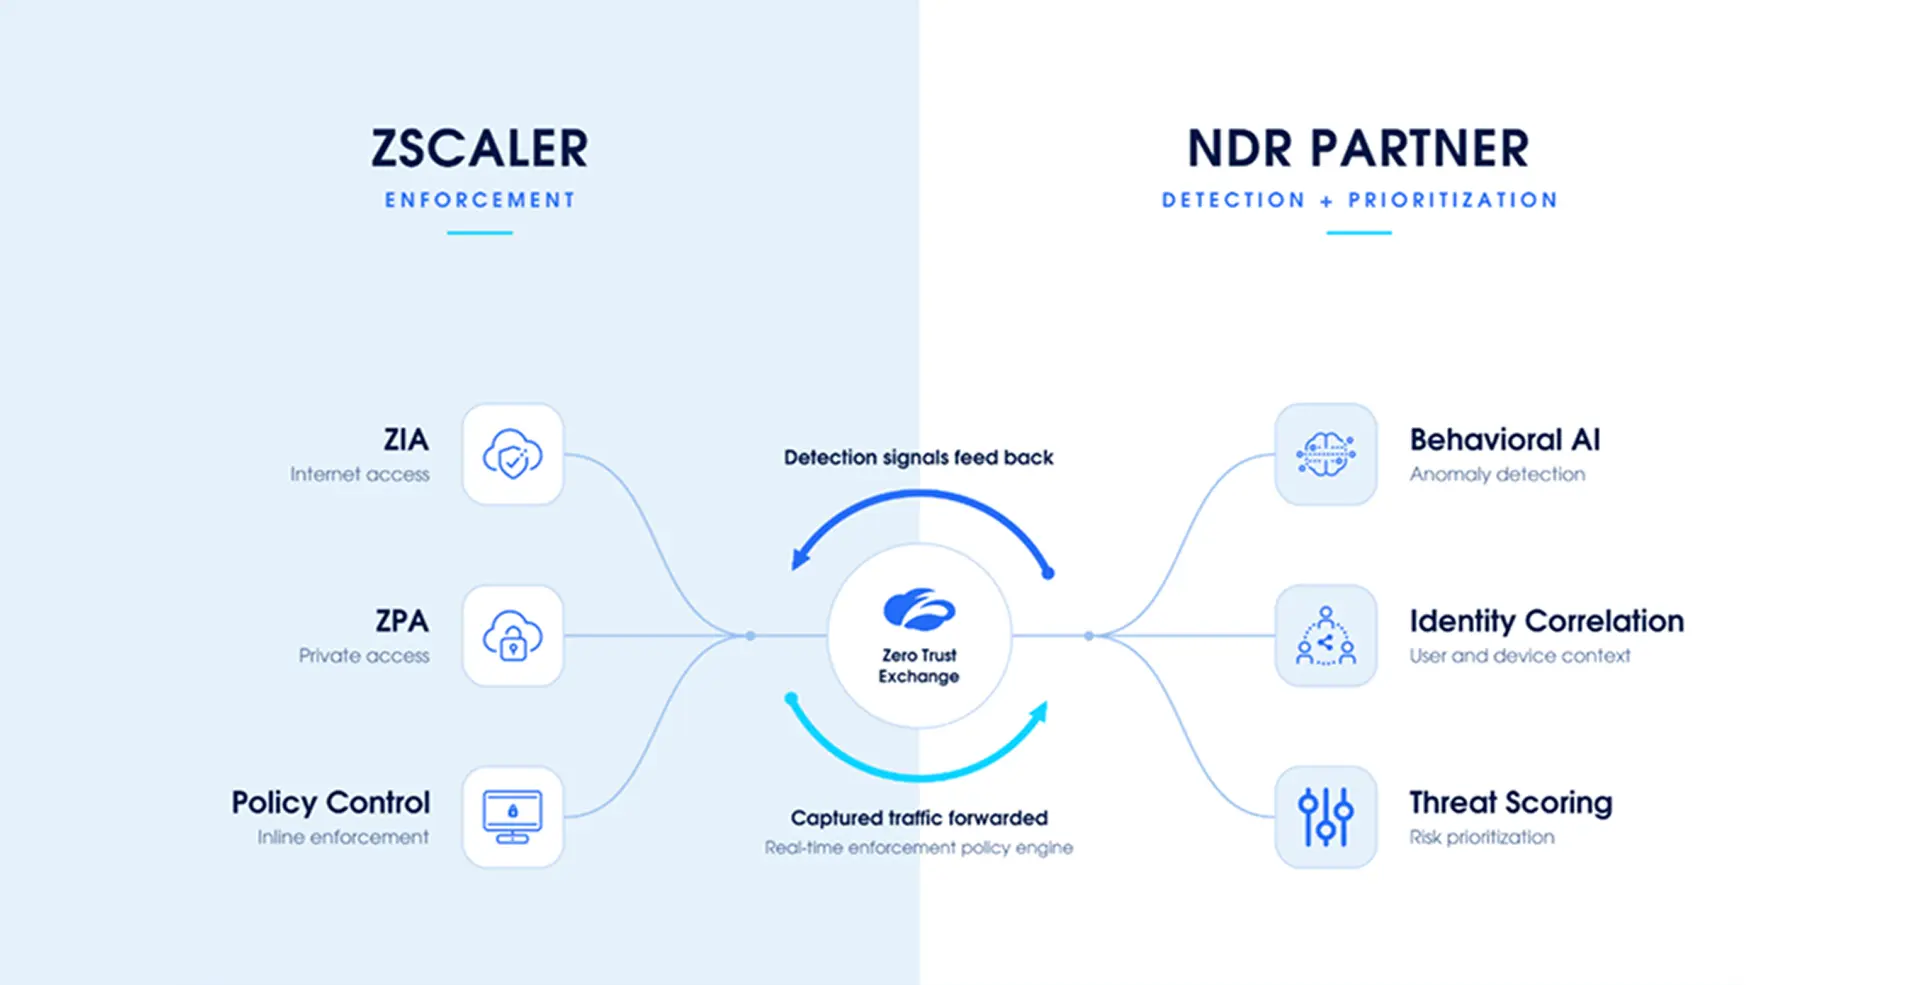
Using granular policies—by user, application, service, country, or destination IP—Traffic Capture forwards captured packets as PCAPNG files to your cloud storage, where supported NDR partners ingest them for deep analysis, threat hunting, and forensic investigation.
No packet data is ever stored in the Zscaler cloud
By correlating this traffic with ZIA and ZPA context, your NDR platform detects the early threat indicators that need continuous traffic capture for anomaly and time series analysis, including slow and hidden C2 traffic, lateral movement, and compromised identities. The platform associates detections with the relevant user and device context.

ZIA traffic
User and internet traffic with identity and access context

Policy-driven capture at the edge
Selective capture applies inline. No hardware to deploy

Your cloud storage
AWS, Azure, or GCP. You own and retain the data

NDR platform of choice
Detect, hunt, and investigate with enriched evidence
For teams with NDR, policy-driven traffic captures from ZIA provide SOC and IR analysts with on-demand, replayable evidence for investigations and help support retention requirements—all from capture data you own.
Turn Internet Blind Spots Into Evidence
As the hybrid workforce moves to cloud-based security, SOC teams need traffic visibility so NDR can still run behavioral and heuristic playbooks for AI-assisted hunting.
The Outcome
Your NDR and SOC teams get instant policy-triggered PCAP evidence, accelerating forensic investigations and compliance audits without hairpinning traffic to on-prem TAPs.
Configure granular policies to selectively capture traffic by criteria, content scan signatures, or app logic.
Prolonged traffic retention for threat hunting and incident response, validating detections and ruling out false positives.
Capture and Investigate east-west App Traffic
ZPA hides private apps behind the Zero Trust Exchange, but SOC teams still need traffic capture on allowed sessions to correlate user context and catch compromised identities or devices.
The Outcome
Your NDR team gains a forensic-ready view that maps malicious network behaviour to authenticated users and devices, cutting detection and response from hours to minutes.
Identify abnormal east–west communications and prioritize high-risk activity for automated containment.
Analysts get continuous monitoring and deep packet-level insights to validate access policies and respond to internal threats.
Empowered SOC With Full SASE Visibility
ZIA and ZPA feed the same NDR platform, so internet, SaaS, and private-app traffic resolve into one timeline instead of three separate tools.
The Outcome
Your SOC works high-confidence detections bound to real users and devices, not IP addresses, and pushes enforcement to the Zscaler edge on both paths.
Score beaconing, tunneling, DNS exfiltration, and low-and-slow staging over time, with every detection tied to identity through LSS records.
A correlated detection revokes internet and private-app access against the user, shortening dwell time without another console.
Benefits
See what the cloud leaves invisible
Extend packet-level visibility to selected remote and internet-bound traffic that traditional corporate sensors may never see.
Maximize NDR investments with cloud-native SASE visibility
Feed enriched captures to NDR partners to surface early indicators of lateral movement, slow and hidden C2 traffic, account compromise, and privilege escalations that may bypass traditional tools.
Investigate with evidence, not fragments
Give NDR analysts replayable captured traffic and rich forensic context to confirm attacks, cut false positives, and build stronger playbooks.

Bring Zscaler traffic and Zero Trust telemetry into supported NDR and analytics
platforms to deepen visibility and accelerate security operations across distributed environments.
USE CASES
Turn traffic evidence into SOC action
Correlate internet and private-app activity to spot reconnaissance and lateral movement while the attacker is still probing.
Retain traffic over extended windows for threat hunting and incident response — validating detections and ruling out false positives.
Hunt using TLS fingerprints and behavioral signals to catch evasive C2 traffic that rotates infrastructure to slip past destination-based controls.
Tie abnormal identity behavior to the apps a user is touching to stop fileless SaaS attacks before data leaves.
Retain packet-level evidence in your own cloud to satisfy HIPAA, PCI DSS, and federal retention mandates.
Learn and explore resources
Frequently Asked Questions
A cloud-native capability in Zscaler Internet Access that provides continuous traffic capture based on rich policy criteria—by user, application, service, country or IP. Packets are packaged as PCAPNG files and written to your cloud storage for an NDR platform to ingest for AI-based evidence and playbooks.
Zscaler acts as a cloud-native, policy-driven switchboard to collect traffic. It de-encapsulates Zscaler headers at the cloud and Private Edge, transforms the captured packets into PCAPNG files, and streams them to your cloud storage with enriched metadata for user, device name, and location info. Your NDR platform then ingests them, eliminating the need for manual correlation to identify the user, device, or location that generated the traffic of interest for the SOC.
No, packet capture and streaming run asynchronously and out-of-band. The heavy lifting of post-processing and transformation is handled by Zscaler’s distributed global and private edges, ensuring no latency impact on active user connections or application performance.
Traditional NDR sensors only see raw, rotating IP addresses. Zscaler enriches the captured packets with ZIA/ZPA identity context, instantly tying every NDR alert to a real, authenticated user and device. This eliminates manual IP-to-user correlation during incident response.
You own and store all of your data. Zscaler writes PCAPNG files directly to your private cloud storage (such as AWS, Azure, or GCP). Zscaler never stores, caches, or retains any of your packet data—ensuring total privacy and seamless regulatory compliance.