Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Storm-1811 exploits RMM tools to drop Black Basta ransomware
Storm-1811’s latest help desk scam begins with email bombing and ends with Black Basta ransomware
This article was originally published by Red Canary, which is now part of Zscaler.
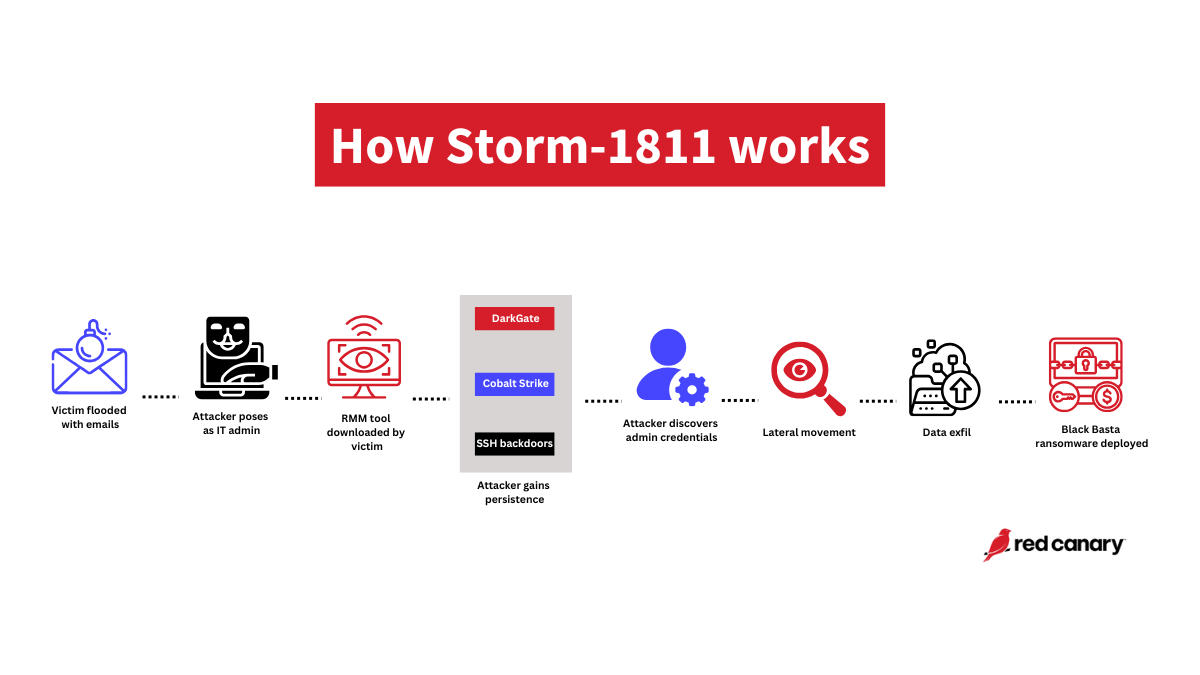
Red Canary has detected likely Storm-1811 activity in multiple customers in the past few weeks. Storm-1811 is Microsoft’s name for a financially motivated threat actor that uses social engineering to impersonate help desk employees or other IT admins to gain initial access to environments via remote monitoring and management (RMM) tools—in this case Microsoft Quick Assist—on victim endpoints. Without prompt response, this activity can lead to Black Basta ransomware in your environment.

Storm-1811’s attack path
Consistent with the Storm-1811 activity we reported in our June 2024 Intelligence Insights, the recently observed activity began with email bombing to flood a victim’s inbox with spam, followed by the adversary, posing as an IT admin offering to help with the email problem, contacting the user via phone or a link to join a Microsoft Teams call. Once in contact, the adversary guided the user into running Microsoft Quick Assist or downloading and running AnyDesk or TeamViewer to provide remote access. The attack continued with reconnaissance, lateral movement, and the establishment of an SSH tunnel backdoor.
Take action
We recommend taking the following precautions to prevent this activity from reaching your environment.
Enhance endpoint visibility
- Deploy detection and response sensors across systems
- Unmonitored endpoints = attacker playground; visibility limits adversary freedom
Monitor RMM tools
- Maintain an approved tools list and monitor or deny unauthorized RMM tools
- Legitimate tools can be exploited—know what’s in your environment
Secure Microsoft Teams usage
- Disable external access by default
- Allowlist trusted partner domains
- Limit file-sharing capabilities to reduce risks from unauthorized tools
You can find more information on Black Basta ransomware in CISA’s recent #StopRansomware advisory.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.

