Zscaler 部落格
訂閱 Zscaler 部落格,第一時間獲取最新資訊!
Storm-1811 exploits RMM tools to drop Black Basta ransomware
Storm-1811’s latest help desk scam begins with email bombing and ends with Black Basta ransomware
This article was originally published by Red Canary, which is now part of Zscaler.
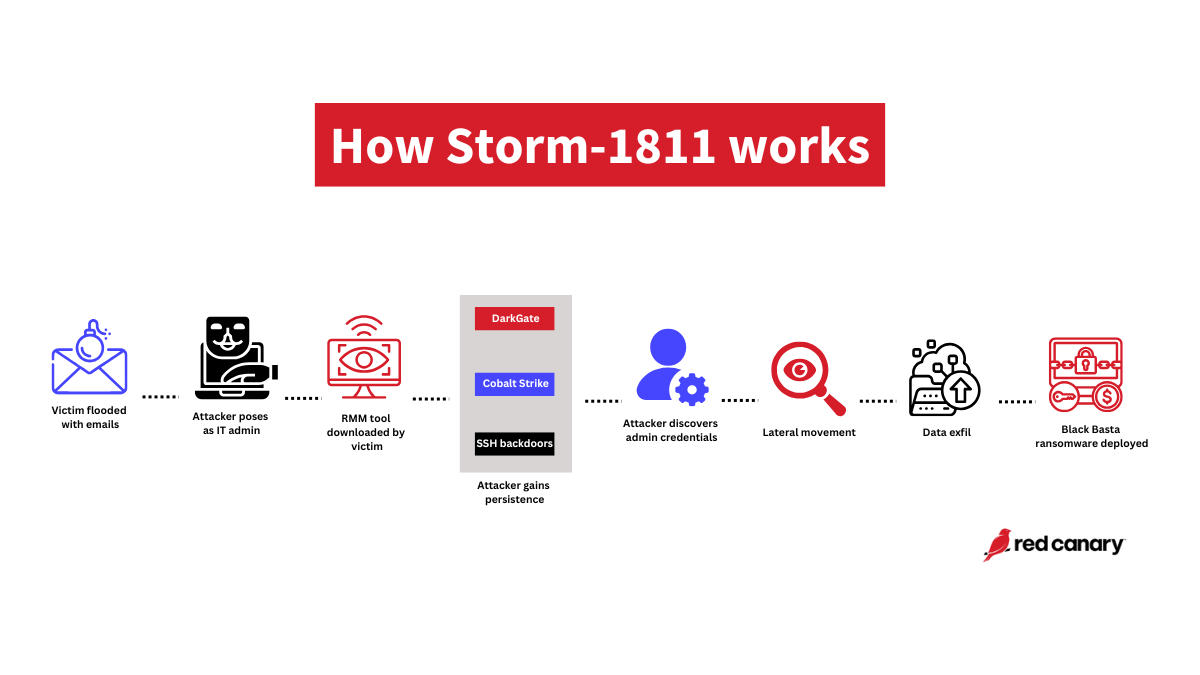
Red Canary has detected likely Storm-1811 activity in multiple customers in the past few weeks. Storm-1811 is Microsoft’s name for a financially motivated threat actor that uses social engineering to impersonate help desk employees or other IT admins to gain initial access to environments via remote monitoring and management (RMM) tools—in this case Microsoft Quick Assist—on victim endpoints. Without prompt response, this activity can lead to Black Basta ransomware in your environment.

Storm-1811’s attack path
Consistent with the Storm-1811 activity we reported in our June 2024 Intelligence Insights, the recently observed activity began with email bombing to flood a victim’s inbox with spam, followed by the adversary, posing as an IT admin offering to help with the email problem, contacting the user via phone or a link to join a Microsoft Teams call. Once in contact, the adversary guided the user into running Microsoft Quick Assist or downloading and running AnyDesk or TeamViewer to provide remote access. The attack continued with reconnaissance, lateral movement, and the establishment of an SSH tunnel backdoor.
Take action
We recommend taking the following precautions to prevent this activity from reaching your environment.
Enhance endpoint visibility
- Deploy detection and response sensors across systems
- Unmonitored endpoints = attacker playground; visibility limits adversary freedom
Monitor RMM tools
- Maintain an approved tools list and monitor or deny unauthorized RMM tools
- Legitimate tools can be exploited—know what’s in your environment
Secure Microsoft Teams usage
- Disable external access by default
- Allowlist trusted partner domains
- Limit file-sharing capabilities to reduce risks from unauthorized tools
You can find more information on Black Basta ransomware in CISA’s recent #StopRansomware advisory.


免責聲明:本部落格文章由 Zscaler 製作,僅供資訊參考,並以「現狀」提供,不保證其準確性、完整性或可靠性。Zscaler 對任何錯誤或遺漏,或基於所提供的資訊而採取的任何行動不承擔任何責任。本部落格文章中連結的任何第三方網站或資源僅為方便起見而提供,Zscaler 對其內容或做法概不負責。所有內容如有變更,恕不另行通知。存取此部落格,即表示您同意這些條款,並承認您有責任自行驗證並根據您的需求適當使用資訊。

