Zscaler 블로그
Zscaler 블로그의 최신 업데이트를 이메일로 받아보세요
Zero Trust Meets Multicloud: A Guide to Secure Workload Segmentation

As businesses migrate applications from traditional data centers to the cloud, they face new challenges in securing them effectively. The attack surface and potential blast radius have expanded, compliance and regulatory requirements have become more stringent and lateral threat movement is still unabated.
Much of this chaos can be attributed to the reliance on old architectures being extended to the cloud. Legacy tools like firewalls and VPNs were not designed to support the dynamic nature of workloads being spun up and down in the cloud. Workloads can span various infrastructure boundaries—cross-cloud, cross-regions, cross-VPCs/VNETs—making it difficult to provide consistent security policies for workloads in the data center.
Workload Segmentation with the Zscaler Zero Trust Cloud
To restore order amidst this chaos, Zscaler has unveiled new innovations to segment workloads across multiple clouds, regions, availability zones, and processes. With expanded support for architectural components that bring zero trust to Azure, GCP, and AWS environments, these advancements empower customers to secure workloads in a true hybrid cloud setting.
- Workload visibility: Realtime discovery service is now expanded to cover AWS/Azure and GCP. With support for multiple accounts across multiple regions in a public cloud, customers can truly think of a cross-cloud global namespace to write security policies
- Workload identity: Security teams working with Azure can now identify workloads by applying User-defined tags along with other cloud metadata attributes and network constructs (FQDN/ Subnets)
- Workload authentication: Coming soon to the portfolio is the capability to support workload authentication based on JSON web tokens!
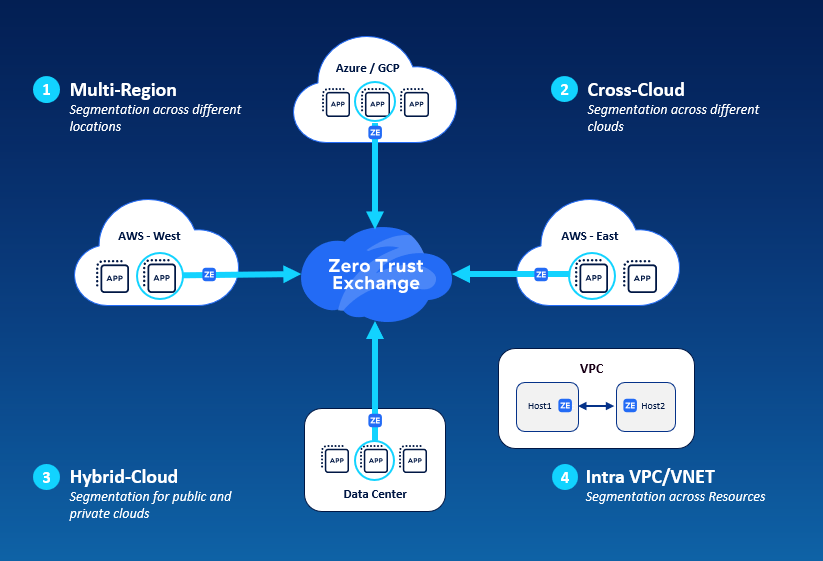
It is imperative that a modern segmentation solution should be built ground up based on cloud-first principles. Watch this short video from Brian Deitch (Chief Technology Evangelist, Zscaler) on how this works.
Segment Processes Inside a Host with Zscaler Microsegmentation
A host based approach now extends the Zscaler platform to segment processes deployed within a VPC/VNET. Customers can now extend the Zscaler zero trust architecture to segment processes deployed in the hybrid cloud.
- Real-time visibility: Zscaler delivers unparalleled visibility into traffic flows, allowing businesses to understand the interactions between hosts, initiators, and receivers of traffic. This traffic flow-based analysis is crucial for identifying potential vulnerabilities and ensuring that workloads are properly segmented.
- Intelligent segmentation: Leveraging AI-driven assistance, Zscaler provides intelligent configuration recommendations. The platform groups resources based on various attributes and traffic flows. Once these groups are identified, Zscaler recommends which groups can communicate with each other, ensuring optimal segmentation and security.
- Policy enforcement across hybrid cloud deployments: Zscaler's policy enforcement capabilities extend across hybrid cloud environments, including multiple cloud regions. This ensures that security policies are consistently applied, regardless of where workloads are hosted. By enforcing policies uniformly, Zscaler helps businesses maintain a strong security posture and comply with regulatory requirements.
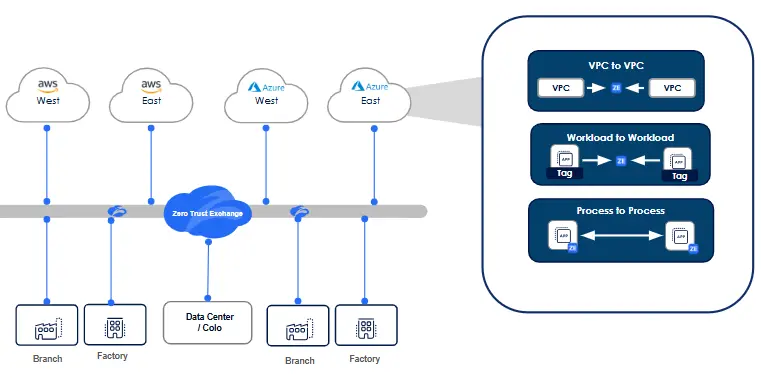
Watch this video from Daniel Perkins, Principal Product Specialist, Zscaler Microsegmentation, to learn more.
As businesses continue to migrate applications to the cloud, the need for effective workload segmentation has never been greater. New innovations from Zscaler deliver a comprehensive solution that offers visibility, intelligent configuration recommendations, and robust policy enforcement. Click here to learn more about Zero Trust Cloud from Zscaler.
Learn more about Zero Trust Cloud at our launch page.

이 게시물이 도움이 되었나요?


면책 조항: 이 블로그 게시물은 정보 제공만을 목적으로 Zscaler에서 작성하였으며, 정확성, 완전성 또는 신뢰성에 대한 어떠한 보증도 없이 "있는 그대로" 제공됩니다. Zscaler는 제공된 정보를 기반으로 수행된 조치나 오류 또는 누락에 대해 어떠한 책임도 지지 않습니다. 이 블로그 게시물에 링크된 제3자 웹사이트나 리소스는 편의를 위해서만 제공되며, Zscaler는 해당 웹사이트의 콘텐츠나 관행에 대해 책임을 지지 않습니다. 모든 콘텐츠는 예고 없이 변경될 수 있습니다. 이 블로그에 접속함으로써 귀하는 본 약관에 동의하며 귀하의 필요에 따라 정보를 확인하고 사용할 전적인 책임이 귀하에게 있음을 인정합니다.