Zscaler 部落格
訂閱 Zscaler 部落格,第一時間獲取最新資訊!
Zero Trust Meets Multicloud: A Guide to Secure Workload Segmentation

As businesses migrate applications from traditional data centers to the cloud, they face new challenges in securing them effectively. The attack surface and potential blast radius have expanded, compliance and regulatory requirements have become more stringent and lateral threat movement is still unabated.
Much of this chaos can be attributed to the reliance on old architectures being extended to the cloud. Legacy tools like firewalls and VPNs were not designed to support the dynamic nature of workloads being spun up and down in the cloud. Workloads can span various infrastructure boundaries—cross-cloud, cross-regions, cross-VPCs/VNETs—making it difficult to provide consistent security policies for workloads in the data center.
Workload Segmentation with the Zscaler Zero Trust Cloud
To restore order amidst this chaos, Zscaler has unveiled new innovations to segment workloads across multiple clouds, regions, availability zones, and processes. With expanded support for architectural components that bring zero trust to Azure, GCP, and AWS environments, these advancements empower customers to secure workloads in a true hybrid cloud setting.
- Workload visibility: Realtime discovery service is now expanded to cover AWS/Azure and GCP. With support for multiple accounts across multiple regions in a public cloud, customers can truly think of a cross-cloud global namespace to write security policies
- Workload identity: Security teams working with Azure can now identify workloads by applying User-defined tags along with other cloud metadata attributes and network constructs (FQDN/ Subnets)
- Workload authentication: Coming soon to the portfolio is the capability to support workload authentication based on JSON web tokens!
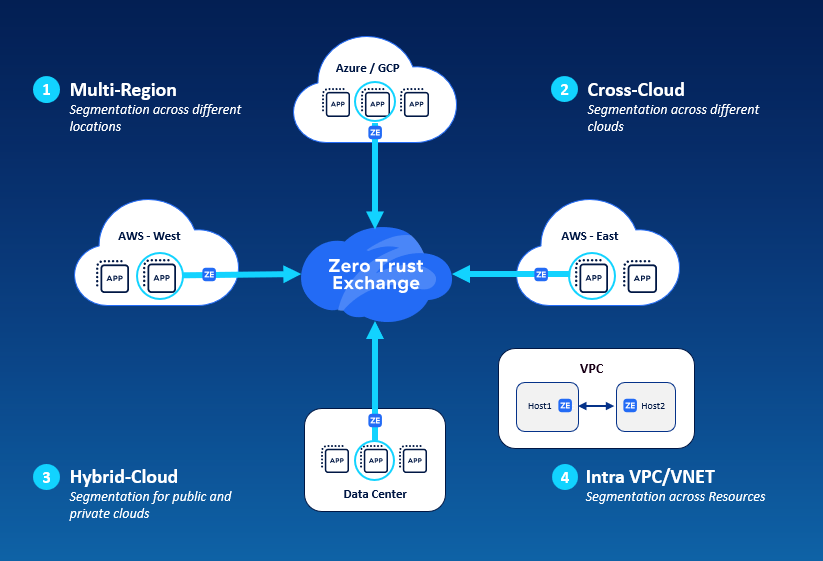
It is imperative that a modern segmentation solution should be built ground up based on cloud-first principles. Watch this short video from Brian Deitch (Chief Technology Evangelist, Zscaler) on how this works.
Segment Processes Inside a Host with Zscaler Microsegmentation
A host based approach now extends the Zscaler platform to segment processes deployed within a VPC/VNET. Customers can now extend the Zscaler zero trust architecture to segment processes deployed in the hybrid cloud.
- Real-time visibility: Zscaler delivers unparalleled visibility into traffic flows, allowing businesses to understand the interactions between hosts, initiators, and receivers of traffic. This traffic flow-based analysis is crucial for identifying potential vulnerabilities and ensuring that workloads are properly segmented.
- Intelligent segmentation: Leveraging AI-driven assistance, Zscaler provides intelligent configuration recommendations. The platform groups resources based on various attributes and traffic flows. Once these groups are identified, Zscaler recommends which groups can communicate with each other, ensuring optimal segmentation and security.
- Policy enforcement across hybrid cloud deployments: Zscaler's policy enforcement capabilities extend across hybrid cloud environments, including multiple cloud regions. This ensures that security policies are consistently applied, regardless of where workloads are hosted. By enforcing policies uniformly, Zscaler helps businesses maintain a strong security posture and comply with regulatory requirements.
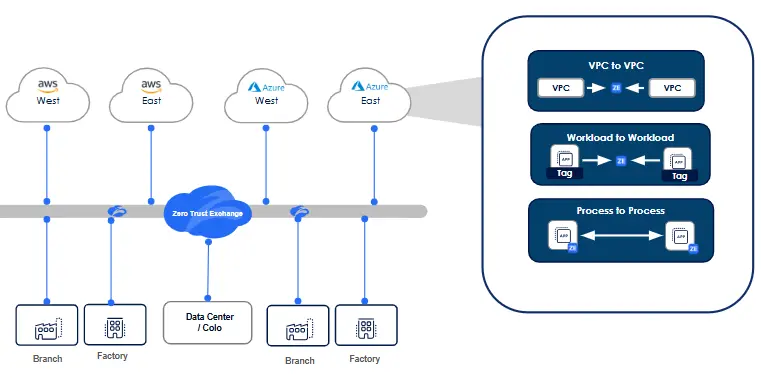
Watch this video from Daniel Perkins, Principal Product Specialist, Zscaler Microsegmentation, to learn more.
As businesses continue to migrate applications to the cloud, the need for effective workload segmentation has never been greater. New innovations from Zscaler deliver a comprehensive solution that offers visibility, intelligent configuration recommendations, and robust policy enforcement. Click here to learn more about Zero Trust Cloud from Zscaler.
Learn more about Zero Trust Cloud at our launch page.


免責聲明:本部落格文章由 Zscaler 製作,僅供資訊參考,並以「現狀」提供,不保證其準確性、完整性或可靠性。Zscaler 對任何錯誤或遺漏,或基於所提供的資訊而採取的任何行動不承擔任何責任。本部落格文章中連結的任何第三方網站或資源僅為方便起見而提供,Zscaler 對其內容或做法概不負責。所有內容如有變更,恕不另行通知。存取此部落格,即表示您同意這些條款,並承認您有責任自行驗證並根據您的需求適當使用資訊。