Zscaler 部落格
訂閱 Zscaler 部落格,第一時間獲取最新資訊!
How Siemens Healthineers Secured a Complex RISE with SAP Migration with Zero Trust

Modernizing enterprise applications is a monumental undertaking. Doing so in the midst of a corporate divestiture raises the stakes exponentially. For Siemens Healthineers (SHS), migrating to SAP S/4HANA via RISE with SAP was not just a technical upgrade; it was a foundational step in establishing its independent IT infrastructure, separate from its former parent company, Siemens AG.
The Challenge: Securing a Diverse and Constrained Ecosystem
Migrating to SAP S/4HANA involved moving to a fully managed subscription hosted by SAP in Microsoft Azure. While this simplified management, the "black box" nature of the environment created unique constraints. Conventional security models couldn't provide the granular control and flexible access SHS required.
SHS faced three primary challenges in securing this new environment:
1. Securing Internet-Bound Traffic
By default, traffic from SAP S/4HANA exits directly to the internet. As a security-conscious enterprise, SHS required all egress traffic to be inspected according to corporate policy—a capability not natively offered within the managed SAP environment.
2. Enabling Hybrid Cloud Workflows
As a global organization with numerous remote offices, SHS relies on SAP for critical business processes, including generating print jobs. They needed a secure way to connect their cloud-based SAP applications to physical printers and other devices located on-premises around the world.
3. Providing Secure Third-Party Access
SHS collaborates with a network of business partners and solution providers across the globe. Granting these third parties secure, least-privileged access to the new SAP environment was a mandatory requirement, but doing so without introducing legacy network complexities or security risks was crucial.
The Architectural Blueprint: A Zero Trust Control Plane in Azure
Following SAP's official recommendation for customers with advanced security requirements, SHS engineered an innovative solution using the Zscaler Zero Trust Exchange.
First, they established their own Azure tenant to act as a secure "landing zone" and created a VNet peering connection to their RISE with SAP subscription. Then, they made a critical change: instead of allowing traffic from the SAP environment to go directly to the internet, they redirected it through their Azure tenant for inspection.
This architecture provided a central point of control for all traffic, effectively creating a security control plane for their critical applications and laying the foundation for a true Zero Trust model.
The Zero Trust Solution in Action: A Multi-Faceted Approach
With the foundation in place, SHS deployed the Zscaler platform to address each of their unique access challenges.
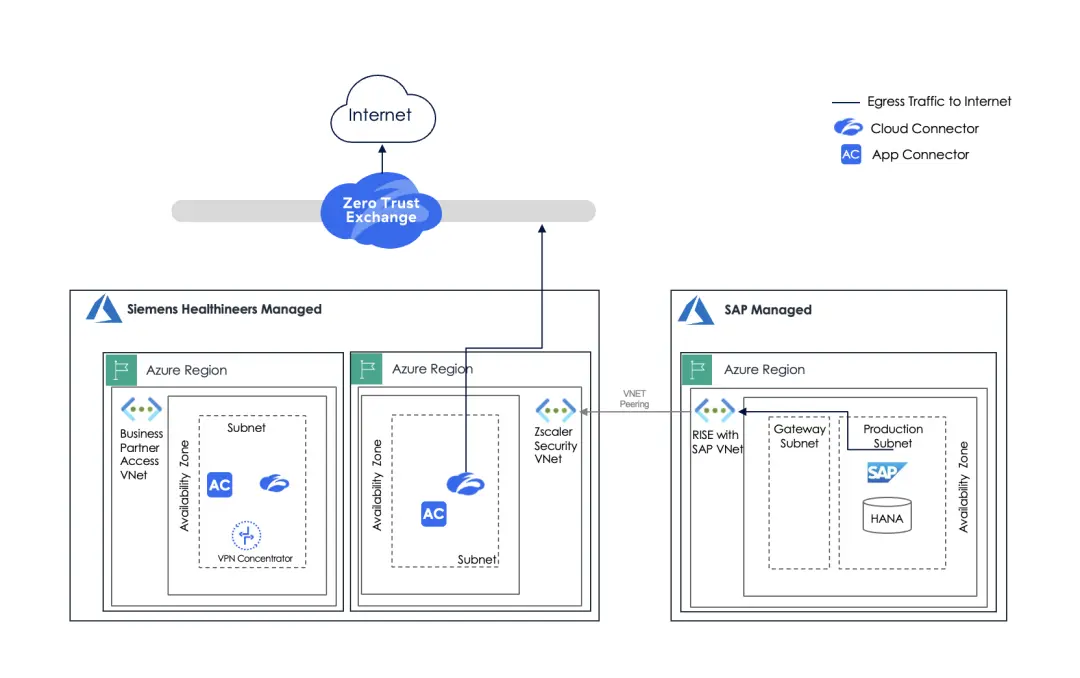
1. Securing Egress Traffic from SAP RISE
Deployed within the SHS tenant, Zscaler Zero Trust Cloud Connectors solve the egress traffic challenge. They intercept all internet-bound requests from the SAP RISE workloads, routing them through the Zscaler Zero Trust Exchange for full content inspection and policy enforcement. This ensures that all app-to-internet traffic is secure and compliant, creating a unified security posture for both user-to-app and app-to-web communications.
2. Bridging the Gap for Healthineers Business Partners
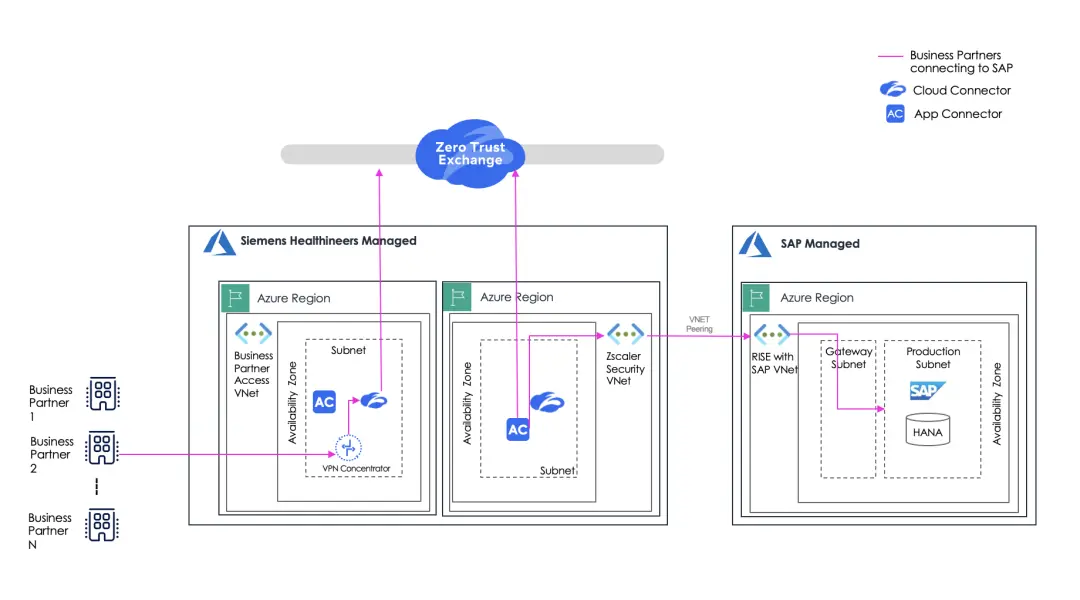
Migrating Healthineers business partners to a new connectivity model was not an option. Instead, SHS created a brilliant hybrid solution. They established a dedicated "Business Partner Access" area in another Azure subscription with a new VPN concentrator. Partners simply repointed their existing IPsec tunnels to this new cluster, requiring no changes on their end.
Once a partner’s traffic arrives at the VPN concentrator, it is immediately handed off to Zscaler Private Access (ZPA). App Connectors deployed in the Azure tenant then broker a secure, inside-out connection to the specific SAP application—never the network.
This innovative approach allowed SHS to:
- Maintain existing partner connectivity without disruption.
- Segment and isolate partner traffic completely.
- Provide granular, least-privileged access to applications, not the network.
3. Solving the Physical Edge: The Printer Problem
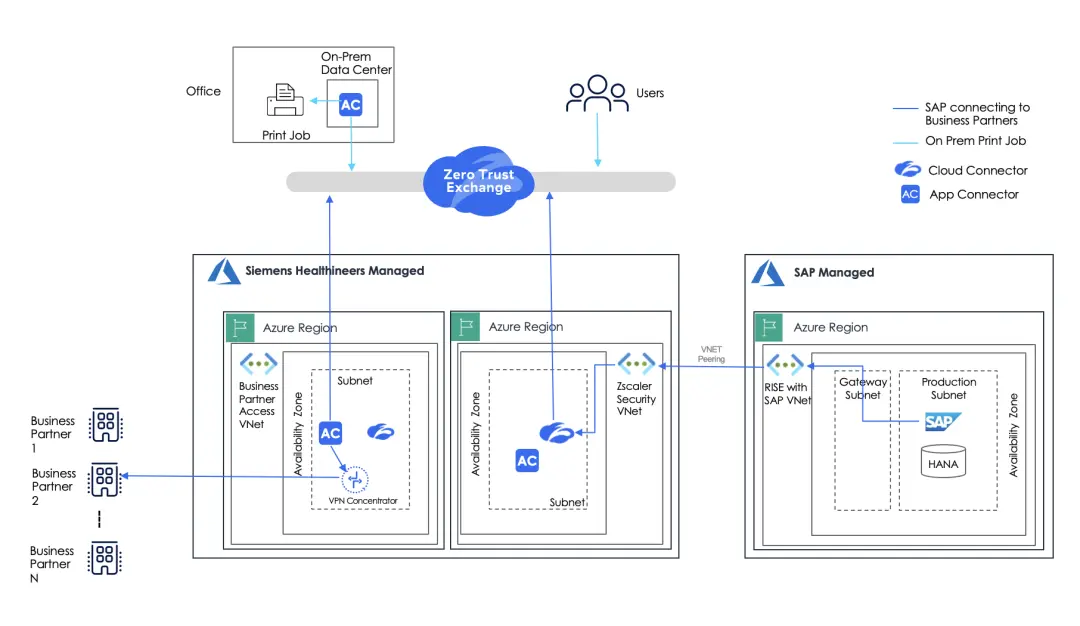
The solution’s flexibility extends all the way to the physical edge. To solve the challenge of printing from a cloud application to an on-premises device, SHS deployed Zscaler Branch Connectors in their remote locations. When a user initiates a print job from the cloud-based SAP RISE environment, ZPA securely routes the request through the Zero Trust Exchange to the Branch Connector, which then delivers it to the physical printer. This elegant solution bridges the hybrid cloud gap without requiring complex legacy networking or firewall rules.
Conclusion: From a Daunting Migration to a Modern Security Showcase
Through its strategic partnership with Zscaler, Siemens Healthineers transformed a daunting migration and divestiture project into a showcase for modern IT security. By embracing Zero Trust Cloud for their SAP cloud migration project, SHS not only secured its mission-critical environment but also established a flexible, scalable, and future-proof foundation for its newly independent infrastructure. The result is a more agile, secure, and efficient enterprise, ready to innovate and grow.
To learn more about Zscaler Zero Trust Cloud, click here.


免責聲明:本部落格文章由 Zscaler 製作,僅供資訊參考,並以「現狀」提供,不保證其準確性、完整性或可靠性。Zscaler 對任何錯誤或遺漏,或基於所提供的資訊而採取的任何行動不承擔任何責任。本部落格文章中連結的任何第三方網站或資源僅為方便起見而提供,Zscaler 對其內容或做法概不負責。所有內容如有變更,恕不另行通知。存取此部落格,即表示您同意這些條款,並承認您有責任自行驗證並根據您的需求適當使用資訊。


