Zscaler 部落格
訂閱 Zscaler 部落格,第一時間獲取最新資訊!
Exposing the Dark Side of Public Clouds - Combating Malicious Attacks on Workloads

Introduction
This article compares the cybersecurity strategies of a company that does not use Zscaler solutions with one that has implemented Zscaler's offerings. By exploring two different scenarios, we will highlight the advantages of Zscaler zero trust for workload communications and its specific use of data loss prevention.
Threat Propagation Without Zscaler Integration
Lateral Movement Between Workloads
In the following scenario, you’ll see that without Zscaler’s integration, the organization is unable to detect or prevent threats effectively. This allows attackers to move laterally and exfiltrate data undetected, leading to significant security risks.
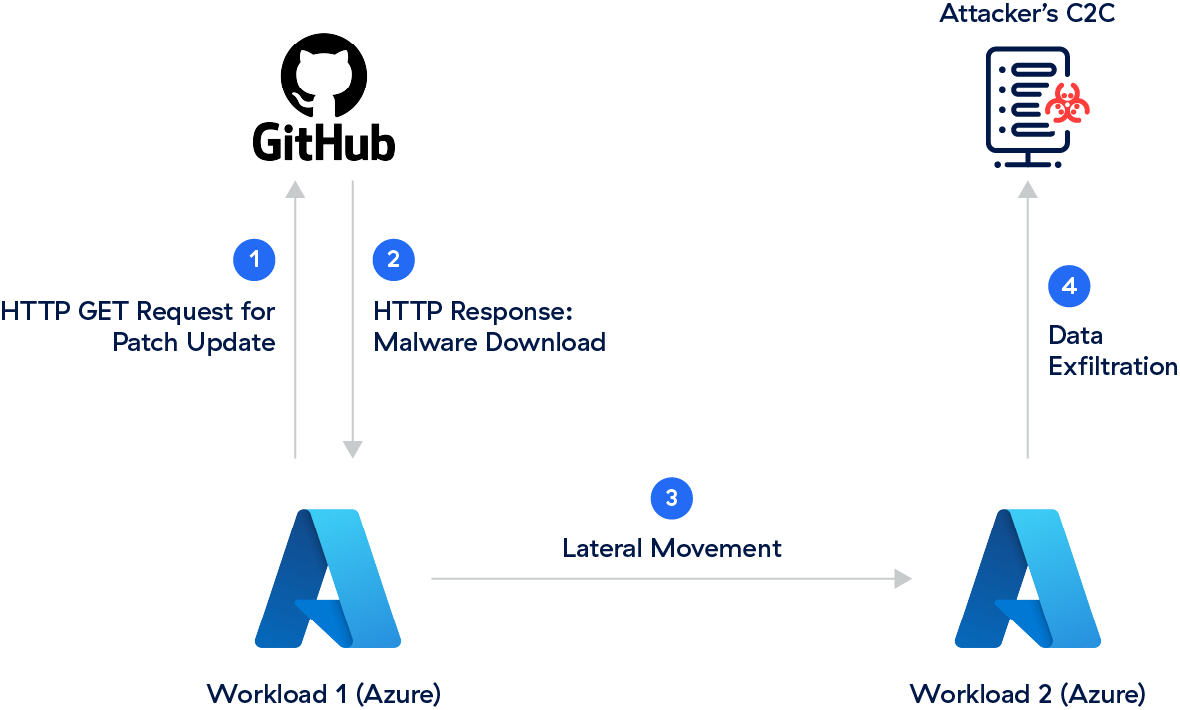
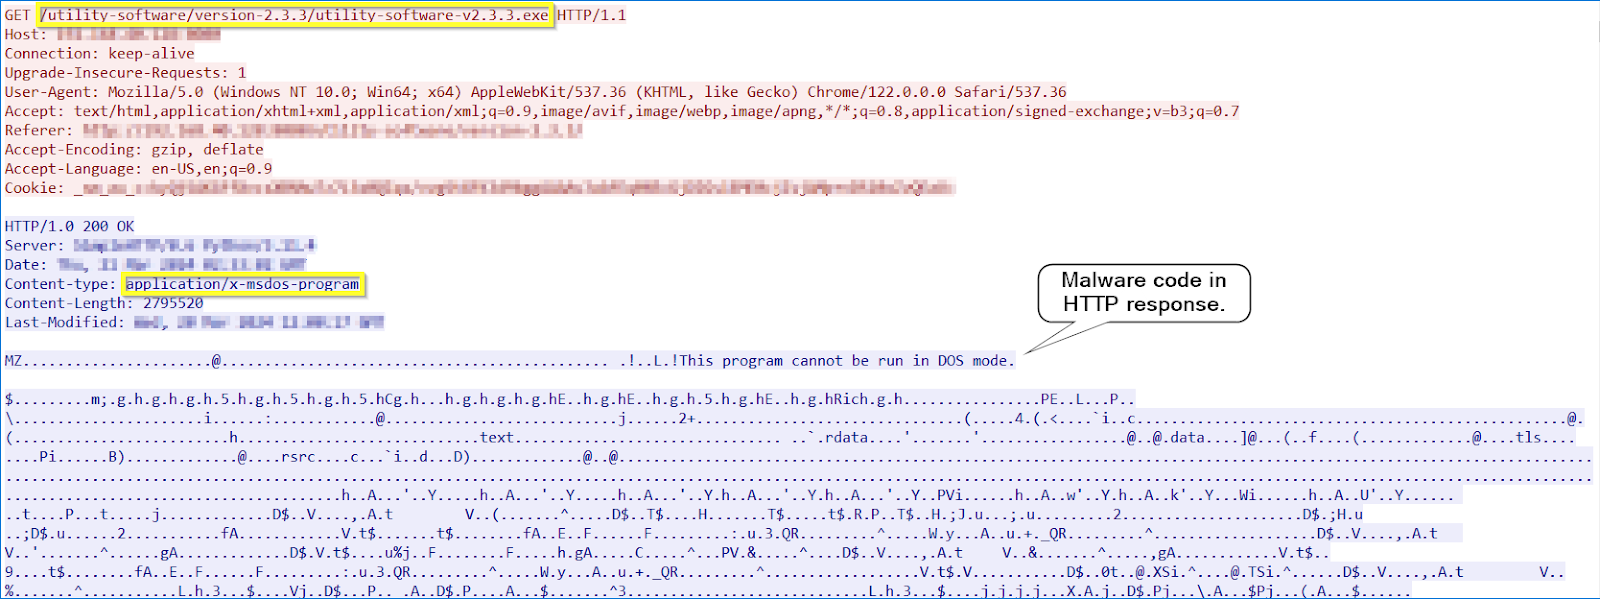
- Workload 1 in Azure West sends an HTTP GET request to GitHub for a patch update: Workload 1, deployed in Azure West, initiates an outbound connection to GitHub to fetch a required patch update. This HTTP GET request is sent to Github to download the patch:
- An HTTP response containing malware from GitHub: Unbeknownst to the organization, the HTTP response received from GitHub contains embedded malware.
- Attacker’s lateral movement to Workload 2: By exploiting the malware present in the HTTP response, an attacker gains access to Workload 1 and subsequently moves laterally to Workload 2 within the Azure West environment. From here, the attacker exploits vulnerabilities or misconfigurations in Workload 2 to achieve a network foothold and establish persistence in Workload 2 that further their malicious objectives.
- Data Exfiltration to a command-and-control (C2) server: With access to Workload 2, the attacker exfiltrates sensitive data from the organization’s environment to a remote C2 server.

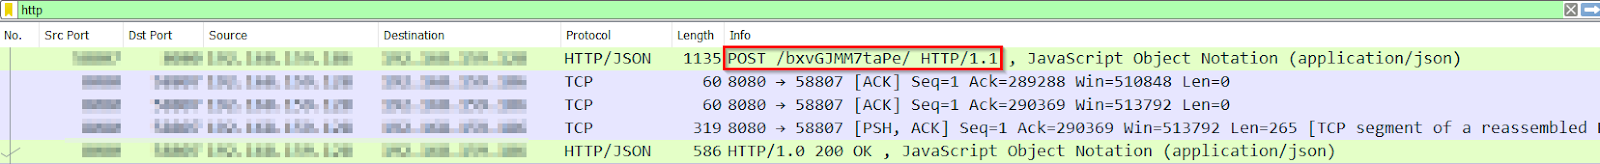
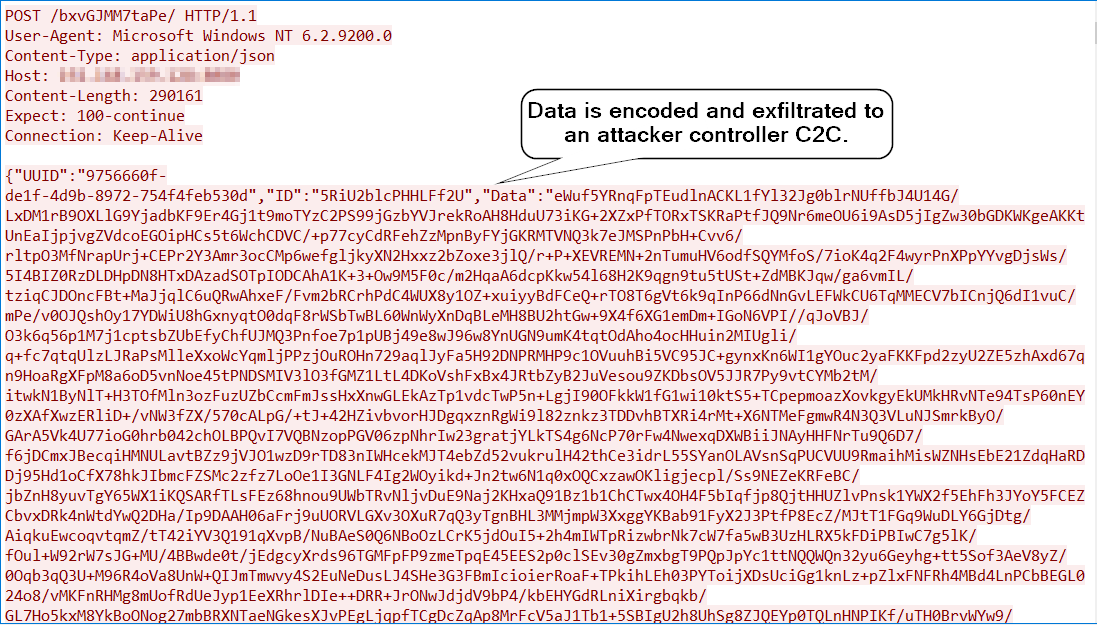
Threat Containment with Zscaler Integration
In the following scenario, Zscaler’s integrated security platform provides comprehensive protection against various stages of the attack life cycle. Organizations can use Zscaler Internet Access (ZIA), coupled with Zscaler Data Loss Prevention (DLP) and Zscaler Workload Communications to implement:
- Strict access controls
- Malware detection and prevention measures
- Workload segmentation
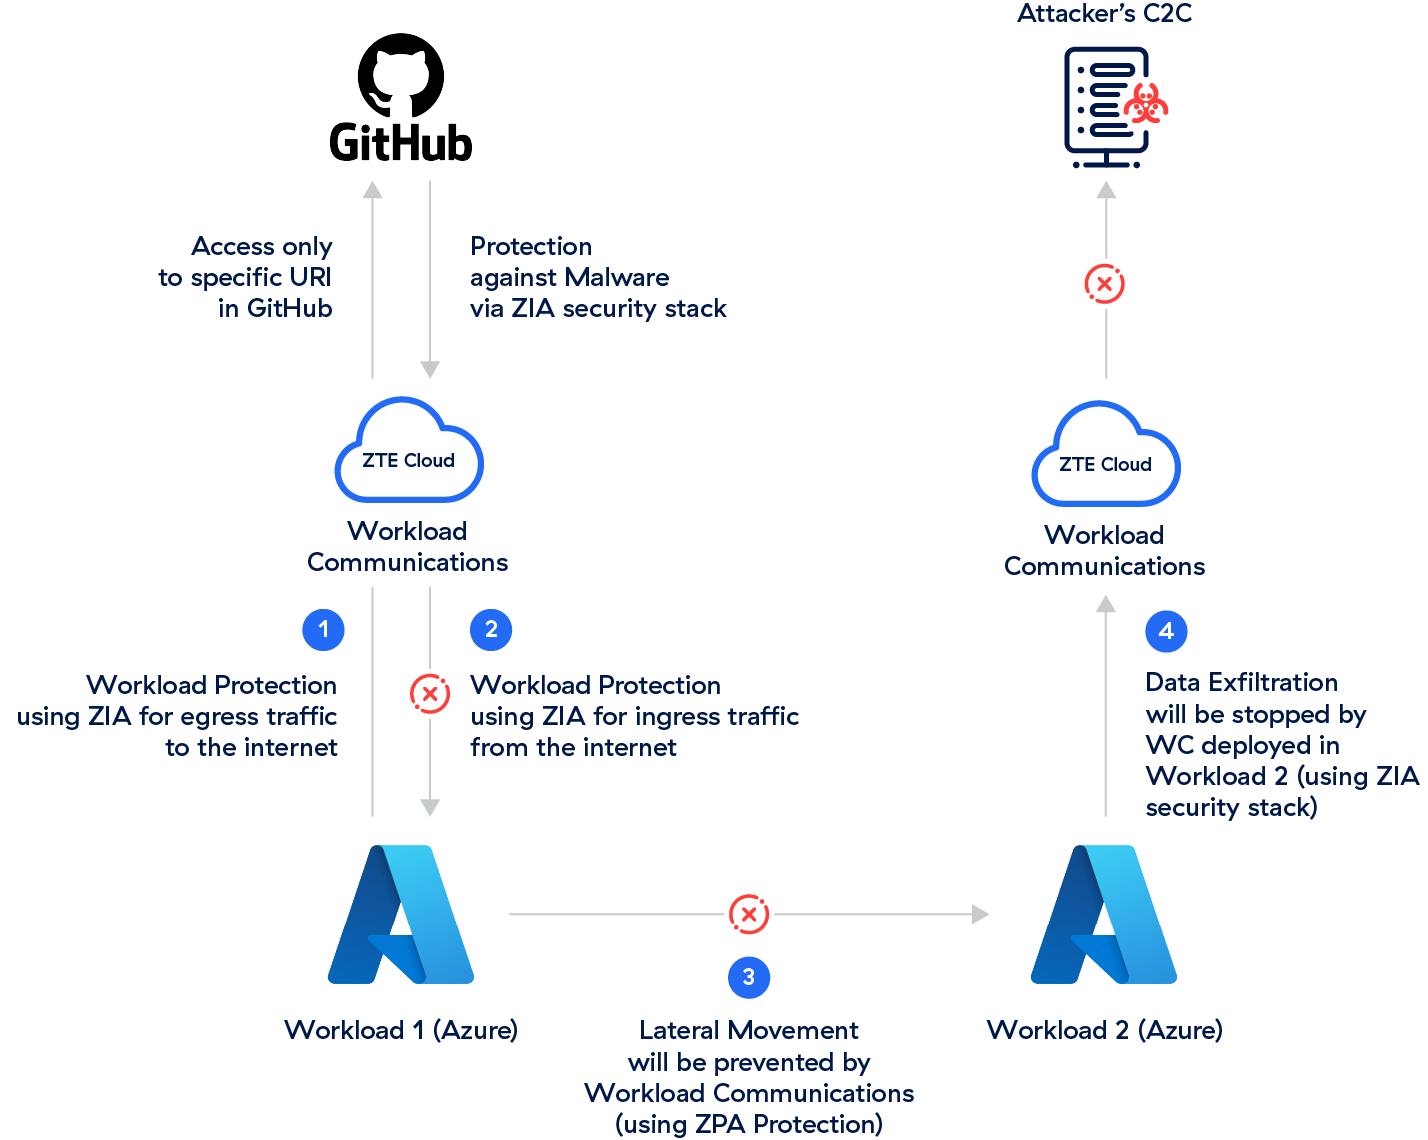
- Enhanced outbound security measures to GitHub (internet): With Zscaler integrated into the organization’s infrastructure, outbound traffic from Workload 1 to GitHub is subjected to stringent access control policies. Only approved URIs are permitted, which ensures communications are limited to trusted destinations. Any attempt to access unauthorized URIs is blocked.
- Malware detection and prevention: Zscaler’s security layers, including content inspection and advanced cloud sandbox features, intercept and inspect the HTTP response from GitHub in real time. Upon detecting malware, Zscaler halts transmission, preventing Workload 1 from being compromised.
- Workload segmentation to prevent lateral movement: Zscaler enforces strict segmentation policies ensuring that Workload 1 and Workload 2, which are deployed across two different regions, are treated as private applications with no direct communication allowed between them. Such segmentation effectively isolates these workloads, preventing any lateral threat movement between them.
- Egress traffic security from Workload 2 with advanced data protection: Egress traffic from Workload 2 is safeguarded using ZIA advanced protection capabilities. Zscaler ensures that sensitive data is not exfiltrated from the organization's environment. By enforcing DLP policies, Zscaler prevents unauthorized data transfers.
Conclusion
The deployment of Zscaler’s solutions significantly enhanced the organization’s ability to combat cyberthreats and safeguard public cloud workloads. Without Zscaler, companies face unmonitored outbound traffic, susceptibility to malware infiltration, and the risk of lateral movement and data exfiltration.
With Zscaler zero trust for workloads, organizations enjoy comprehensive protection, including access control policies, malware detection and prevention, segmentation to prevent lateral movement, and advanced data protection measures. Implementing Zscaler solutions enables organizations to bolster their cybersecurity defenses, mitigate risks, and protect their intellectual property from evolving threats in an interconnected digital environment.


免責聲明:本部落格文章由 Zscaler 製作,僅供資訊參考,並以「現狀」提供,不保證其準確性、完整性或可靠性。Zscaler 對任何錯誤或遺漏,或基於所提供的資訊而採取的任何行動不承擔任何責任。本部落格文章中連結的任何第三方網站或資源僅為方便起見而提供,Zscaler 對其內容或做法概不負責。所有內容如有變更,恕不另行通知。存取此部落格,即表示您同意這些條款,並承認您有責任自行驗證並根據您的需求適當使用資訊。