
Since the early days of the internet, web proxies have been an essential component of security stacks—and for lots of good reasons. For one thing, proxies provide performance benefits and offer deeper security, along with risk analysis for all types of traffic. The truth is, the analysis offered by proxies is much deeper than your standalone firewalls can possibly deliver. Web proxies have the advantage of being able to fully open and inspect traffic. And they do this with zero impact to users.
How is a proxy different from a firewall?
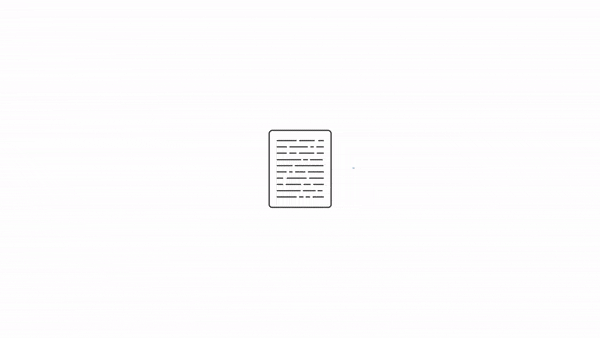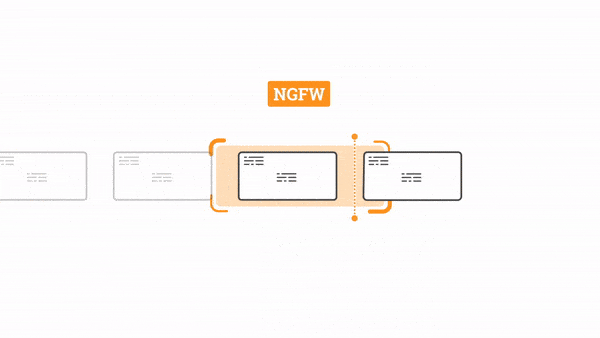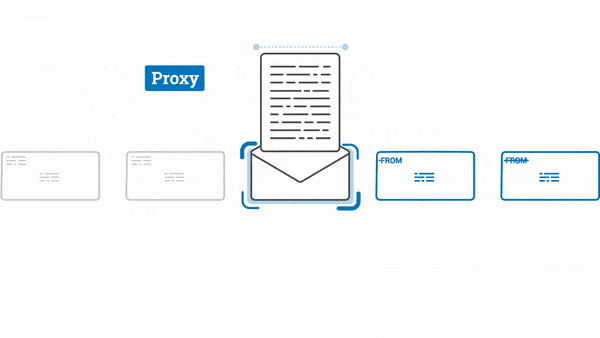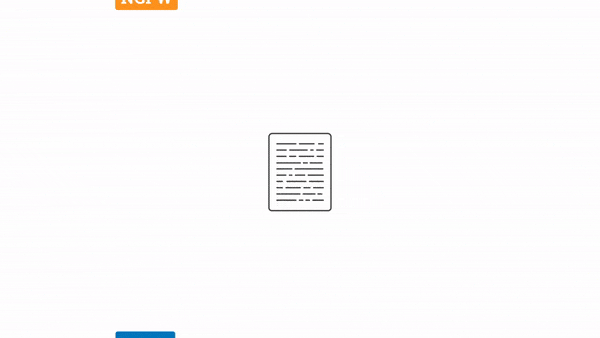
Let’s use a simple analogy to illustrate the differences between a firewall and a proxy. Say your organisation receives a package. The mailroom clerk first reads the label and then decides that more information is needed about what’s inside. So, the clerk puts the parcel through an x-ray machine to check its contents. Overall, x-ray machines work pretty well, but they are not 100% reliable. To really find out what’s inside the package, someone has to open it up and inspect the contents.
A firewall is similar to an x-ray machine in that sense. It works to a point, but it has limitations. To continue with the analogy, a web proxy is similar to a clerk actually opening up the parcel. Proxies provide a detailed look at the content of traffic packets—including payloads. Of course, a proxy unpacks, checks contents, and repacks a traffic packet at a much higher speed than a human being opening up a package.
Some firewall solution providers try to muddle the fundamentals of a proxy architecture with explicit-proxy and PAC file configurations, but that’s a narrow depiction. It’s true that proxies provide a range of methods for driving traffic to proxy security services that go beyond conventional routing, and these abilities provide a much deeper and more scalable solution for securing and directing traffic.
The entire internet is, in fact, built on proxy technology. Think content delivery networks (CDN) used by streaming companies like Netflix. These geographically distributed groups of servers work together to provide fast delivery of internet content to Netflix customers. Think enterprises using application delivery controllers (ADCs), which reside in a data center between the firewall and application servers to accelerate application performance and perform load balancing between servers. And think secure web gateways (SWGs), which provide at-scale protections and monitor user access to the internet.
Firewall technology has its limits
Firewalls help control traffic, applying policies on flows that are not typical proxy traffic. Proxy traffic, on the other hand, covers HTTP, HTTPS, and FTP—which make up the vast majority of internet traffic. Even next-generation firewalls lack the processing power to inspect all HTTPS (encrypted) traffic, which constitutes nearly 90% of web traffic. This limitation has become a major concern and raises a critical question: How can you protect what you can’t inspect? Today’s next-gen firewalls typically have multiple built-in security services (including data loss prevention) designed to prevent threats from entering your organization and sensitive data from leaking out. But you can’t take full advantage of these capabilities when they’re blind to the bulk of your traffic.
Web proxies and SASE to the rescue
Web proxies, on the other hand, are built to inspect encrypted traffic at scale and reliably apply all security and risk controls. Proxies funnel traffic to proxy security services, enabling enterprises to use alternate methods of directing traffic to the internet. As a result, they provide a highly scalable, highly secure solution for securing and directing traffic without impacting performance.
SWGs that are based on the secure access service edge (SASE) model can deliver on these capabilities. Multitenant SASE solutions delivered as a service, in particular, are both cost-effective and scalable—and you never have to worry about updating or scaling the infrastructure as your needs change.
All Zscaler customers, including some of the largest multinational conglomerates, receive the benefits of SWG as an essential part of the Zscaler SASE-based solution. Gartner not only affirms that SWG is an essential SASE component but also that it is the fundamental technology architecture on which a SASE platform should be built.
Learn more about Zscaler SASE or download SASE at a Glance (PDF)
Read the Gartner report on SASE: The Future of Network Security is in the Cloud
Scott Bullock is a Zscaler Global Technical Marketing Engineer based in Melbourne, Australia



