Zscaler 部落格
訂閱 Zscaler 部落格,第一時間獲取最新資訊!
Zscaler Achieves AAA Rating in CyberRatings 2024 SSE Test
When it comes to researching a potential investment, no source of information is more valuable than independent product testing. Every vendor will tell you that they are better than the other guys, but actual performance against an objective, public methodology cannot be faked or swayed by clever marketing.
That’s why we are proud to announce that today, Cyberratings.org (“CyberRatings”), the leading non-profit security testing organization, awarded the Zscaler Zero Trust Exchange an “AAA” rating in its 2024 Threat Protection Test. The highest possible rating, Zscaler’s AAA score represents an overall out-of-the-box security efficacy of 98%.
These results underscore Zscaler’s industry-leading threat protection and our tireless dedication to innovate and consistently improve security outcomes for our customers.
Download the CyberRatings Zscaler SSE Threat Protection Report to see the detailed Zscaler results.
Key Results
The importance of third-party, independent security testing
Cyberratings.org is a non-profit organization dedicated to independent, objective research and testing of cybersecurity products. Unlike many vendor-sponsored product tests that are tuned to show an individual vendor in a positive light, CyberRatings transparently applies the same methods to each security product in a given area.
The Cyberratings.org AAA score for the Zero Trust Exchange is a result that customers can trust. Moreover, given the breadth and depth of threat testing involved — covering thousands of diverse malware, exploit, and evasion samples, and more — these results provide independent validation that Zscaler delivers industry-leading cyber threat protection across the full range of cyber threats.
Comprehensive protection against cyber threats
The CyberRatings Threat Protection Report is designed to test SSE products around how accurately they block threats while allowing legitimate traffic. This test used their Threat Protection Methodology 2.1, which assesses SSE products in several areas, including:
- Threat Protection – How effectively does the SSE protect against threats (malware and exploits)?
- Resistance to Evasion – How effectively does the product handle techniques that would otherwise permit attackers to circumvent security controls?
- TLS/SSL Functionality — Does the SSE support the most widely used ciphers to decrypt and inspect TLS/SSL traffic?
Zscaler’s ability to inspect SSL and TLS traffic at scale unlocks the ability to perform advanced security measures, which was critical to Zscaler’s performance in this evaluation. This test called on capabilities across the Zscaler Zero Trust Exchange, including features such as Zscaler URL Filtering, Advanced Threat Protection, Browser Isolation, and the Cloud Sandbox.
Below, we dive deeper into some of the results.
100% of evasions blocked
Evasion detection is especially critical, as threat actors often seek to modify or disguise their attacks at the point of delivery to evade detection by traditional security controls. That is, a security product may detect a known malware sample, for instance, but it may not detect or block obfuscated traffic used to hide that malware. Moreover, even when a security tool detects an evasion technique, it still may be unable to decode this traffic and alert on the original attack. For this reason, evasion detection is particularly challenging — and yet, one successful evasion may be enough to compromise a system successfully.
As a result, any effective SSE must detect a broad range of evolving evasion techniques. An SSE must:
- Deliver the broadest possible coverage against evasion techniques
- Be highly resistant to evasion variants
- Decode obfuscated traffic and alert on the original attack payload, not just alert on the obfuscation itself
CyberRatings tested Zscaler with a variety of evasion techniques, including:
- HTTP Obfuscation
- HTTP Compression
- HTML Obfuscation
- Packers (binary obfuscation)
- Compressors
- Layered Evasions (multiple evasion techniques)
Over one thousand evasion techniques were tested and Zscaler blocked every single one, including complex, layered evasions that use multiple techniques.
Defending against the full range of exploits
It is essential for any SSE to block exploits, which threat actors use to compromise systems and devices, bypass security controls, and move laterally on the network. Crucially, exploits also include zero-day attacks, for which many enterprises lack defenses. Throughout the first half of 2024, we have seen numerous successful and high-impact exploits on internet-facing devices and systems such as VPNs or firewalls, which are increasingly targeted as entry points by adversaries. In general, exploits typically target:
- Protocols
- Products and Applications
- Operating Systems
When tested against 205 unique exploits, including in scenarios both with and without network load, Zscaler stopped 98.05% of threats inline. To accomplish this, Zscaler uses an unmatched defense-in-depth approach that includes full TLS/SSL inspection of traffic at scale, Advanced Threat Protection, IPS, and more.
Preventing wild and handcrafted malware
The CyberRatings malware test included a range of payloads that organizations must defend against, including:
- Ransomware
- Adware
- Spyware
- Information stealers
- Botnets
- Polymorphic ransomware
CyberRatings not only tested the Zscaler Zero Trust Exchange against a full range of wild malware samples, but also handcrafted, targeted malware payloads to test unknown threats against the Cloud Sandbox. Facing more than seven thousand unique malware payloads, Zscaler blocked over 99.9% of samples — an astounding rate of protection. To achieve such a high level of malware prevention, Zscaler again leverages a defense-in-depth approach that includes:
- Full SSL/TLS inspection at scale to unlock the advanced security capabilities of our Secure Web Gateway, Zero Trust Cloud Firewall, Browser Isolation and more
- The Zscaler “cloud effect,” which draws on the more than 9 billion threats blocked per day across the Zscaler ZTE
- An array of cutting-edge malware engines that stay perpetually up-to-date against the full range of malware threats
- An AI-powered Advanced Cloud Sandbox that intelligently identifies, quarantines, and prevents unknown or suspicious threats inline
Performance and TLS/SSL inspection
In general, enterprises struggle with implementing security solutions that impede performance. Zscaler benefits tremendously from being a cloud-native platform that is delivered across over 150 edge locations worldwide. Zscaler peers directly with major internet providers and SaaS applications like Microsoft 365 to ensure minimal network hops to cloud services. Moreover, our Single-Scan, Multi-Action™ (SSMA) engine allows all security inspection engines to inspect the same TLS/SSL packet contents in one pass, at the same time. All of this contributes to best-in-class SLAs maintained by the Zscaler Zero Trust Exchange.
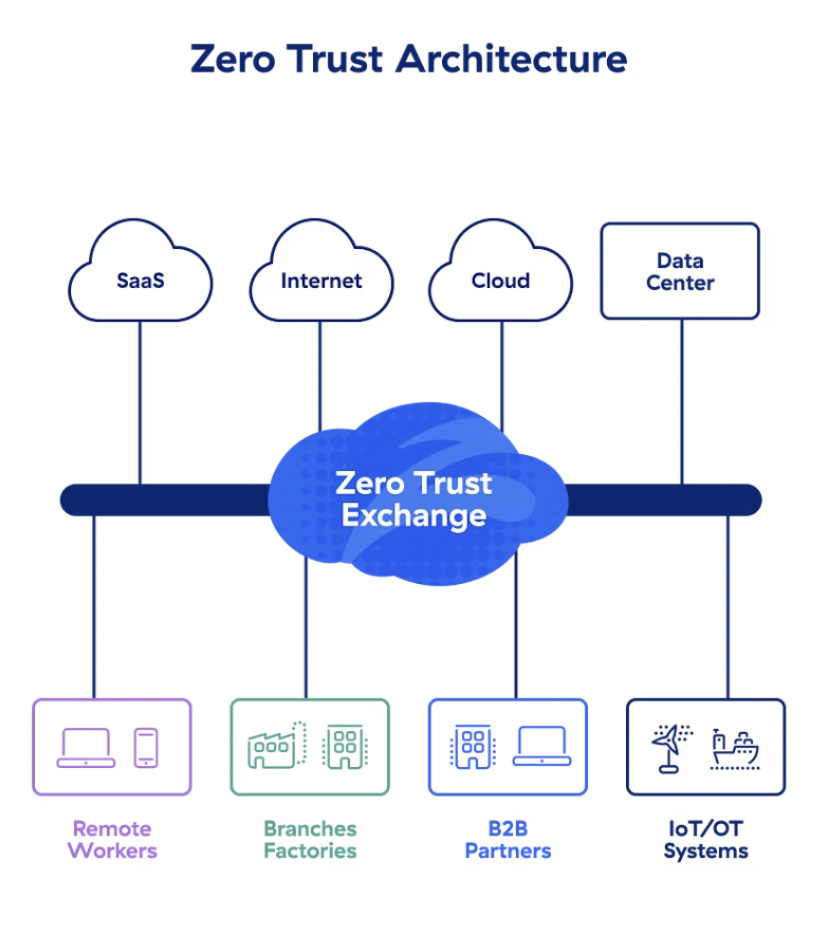
To explore the full report findings, download the CyberRatings Zscaler SSE Threat Protection Report.


免責聲明:本部落格文章由 Zscaler 製作,僅供資訊參考,並以「現狀」提供,不保證其準確性、完整性或可靠性。Zscaler 對任何錯誤或遺漏,或基於所提供的資訊而採取的任何行動不承擔任何責任。本部落格文章中連結的任何第三方網站或資源僅為方便起見而提供,Zscaler 對其內容或做法概不負責。所有內容如有變更,恕不另行通知。存取此部落格,即表示您同意這些條款,並承認您有責任自行驗證並根據您的需求適當使用資訊。


