The recent ransomware attack on the Colonial Pipeline abruptly halted operations on the largest refined products pipeline in the United States, impacting fuel availability across the eastern half of the country. In this attack, the criminal group Darkside utilized a “double extortion” attack -- exfiltrating nearly 100GB of data and threatening to publish it to the internet in addition to encrypting data. DarkSide has been notable for recent enhancements to their double extortion strategies, including threats to target companies listed on the NASDAQ stock exchange to negatively influence stock prices if ransoms are not paid.
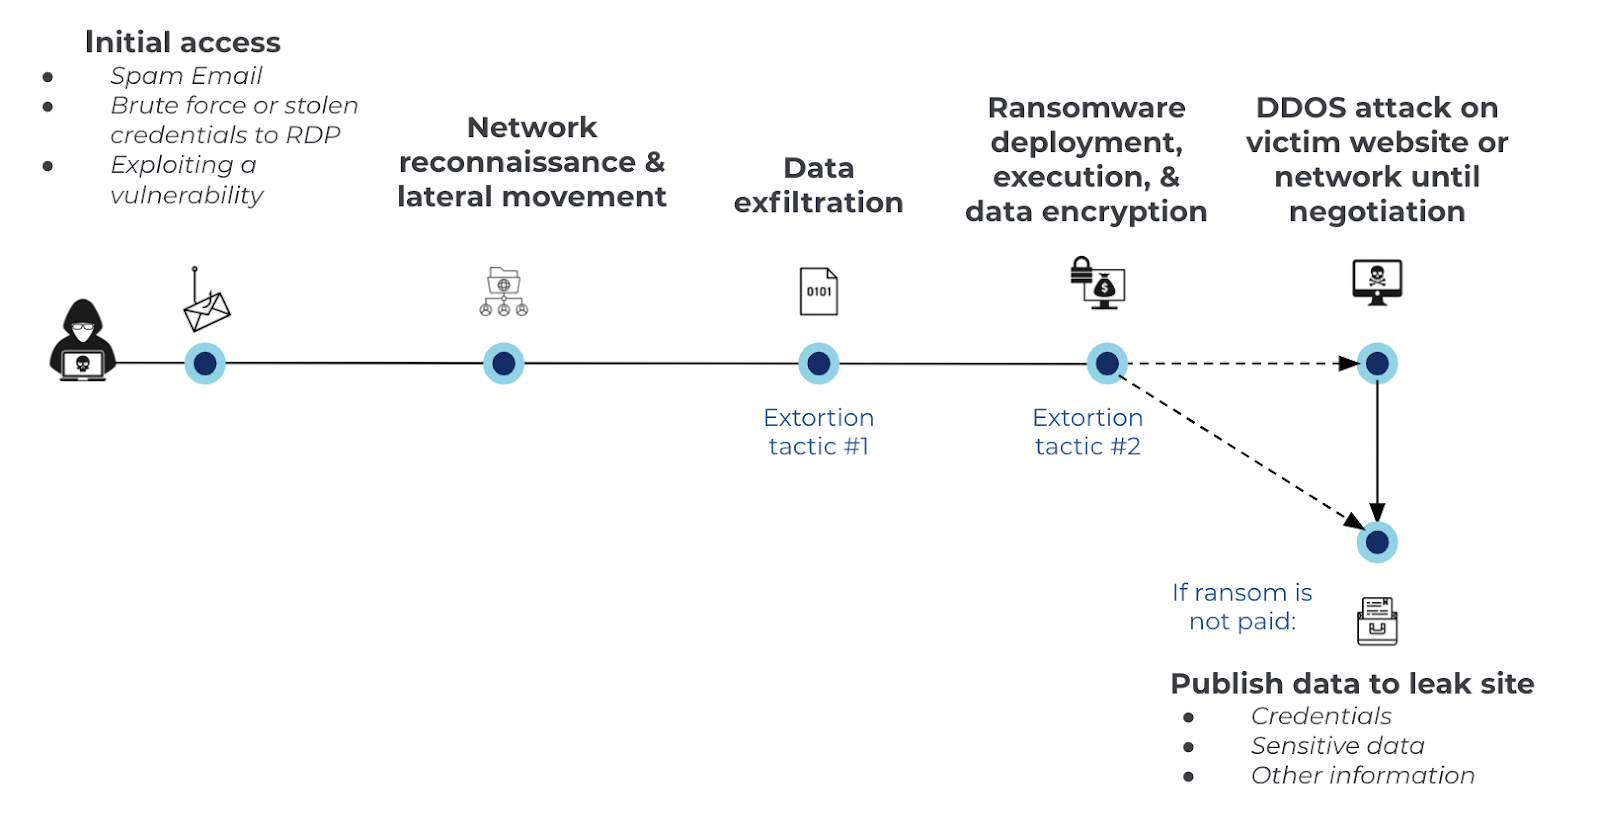
In the new report “ThreatLabZ Ransomware Review: The Advent of Double Extortion,” the Zscaler ThreatLabZ research team analyzed threat intelligence and data from 150B+ daily transactions on the Zscaler cloud to detail the sharp rise in double extortion ransomware attacks since late 2019, along with other ransomware trends, including DDoS and third-party supply chain attacks. Double extortion gives cyberattackers additional leverage, resulting in larger ransoms and higher success rates. The attack chain of a double extortion attack looks like this:
In this report, ThreatLabZ dives deep into the attack sequences, victim profiles, and business impact of a number of notable ransomware families that have utilized these tactics over the past year, including:
- Maze / Egregor
- Sodinokibi/REvil
- Doppelpaymer
- Ragnar Locker
- Avaddon
- Conti
- DarkSide
How to protect yourself against ransomware
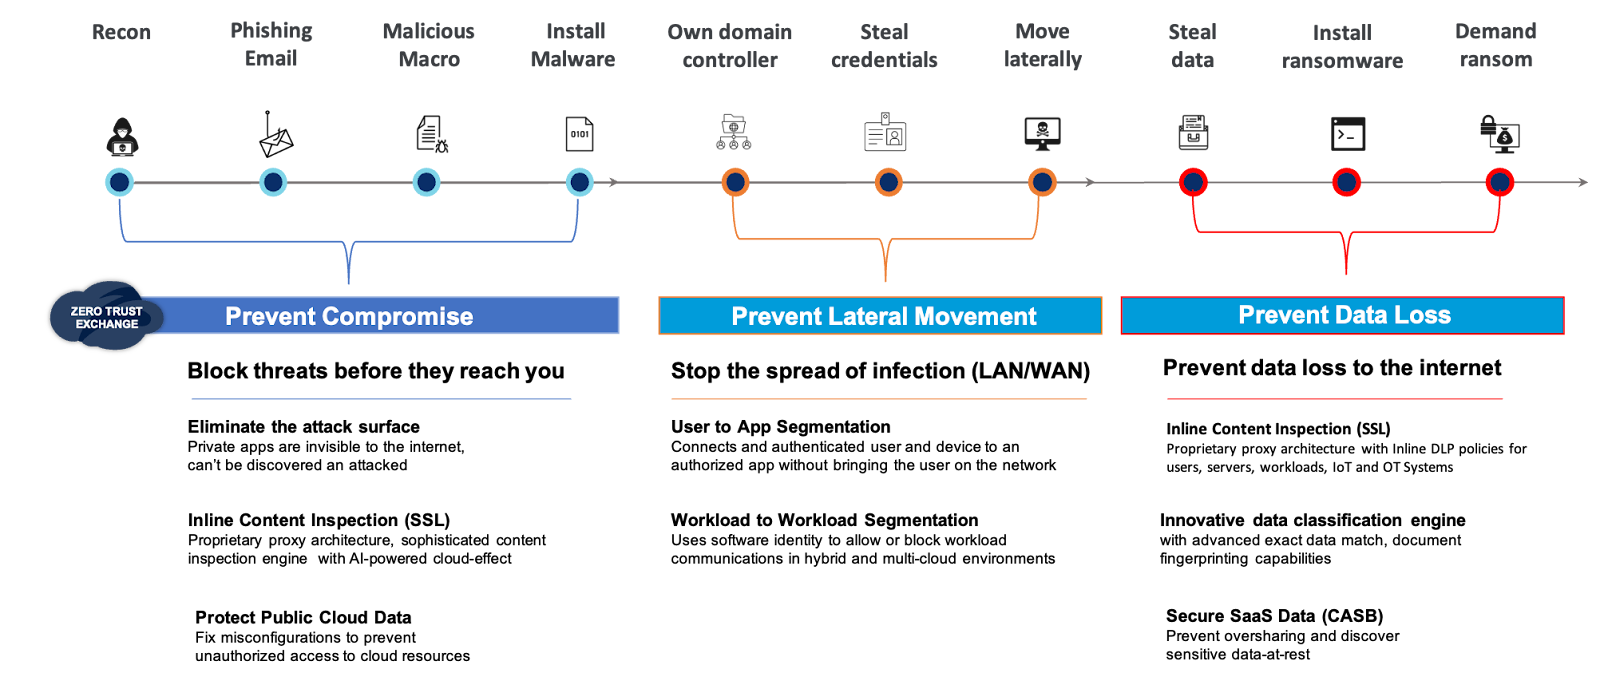
Protection against ransomware is rooted in the principles of Zero Trust: reducing your attack surface as much as possible, implementing consistent authentication and context-based access control policies, and monitoring your traffic both to prevent infiltration and exfiltration. The report offers several best practices recommendations to safeguard your organization against ransomware, such as:
- Enforce a consistent security policy to prevent initial compromise. With a distributed workforce, it is important for organizations to implement a secure access service edge (SASE) architecture that can enforce consistent security policy no matter where the users are working (in-office or remotely).
- Implement zero trust network access (ZTNA) architecture. Segment environments as granularly as possible and implement dynamic least-privileged access controls to eliminate lateral movement and reduce the external attack surface.
- Deploy in-line data loss prevention. Prevent exfiltration of sensitive information with trust-based data loss prevention tools and policies to thwart double-extortion techniques.
- Keep software and training up-to-date. Apply software security patches and conduct regular security awareness employee training to reduce vulnerabilities that can be exploited by cybercriminals.
- Have a response plan. Prepare for the worst with cyber-insurance, a data backup plan, and a response plan as part of your overall business continuity and disaster recovery program.
Zscaler’s cloud native proxy-based architecture provides a unique advantage by safely connecting users and entities directly to applications -- not networks -- and by making internal apps invisible to the internet. Here is how organizations can leverage Zscaler’s Zero Trust Exchange to safeguard against targeted ransomware attacks:
To learn more about today’s top ransomware threats and how to protect your organization against them, download a free copy of “ThreatLabZ 2020 Ransomware Review: The Advent of Double Extortion.”
To hear more from the ThreatLabZ team about ransomware take an even deeper look at DarkSide, join the “Advances in Ransomware” session at Zenith Live, Zscaler’s virtual event happening June 15th. Register for free today.