Zscalerのブログ
Zscalerの最新ブログ情報を受信
CVE-2026-114938: OpenJDK Base64 Decoder Vulnerable To Pre-Authentication RCE (Java4Shell)

Introduction
On November 17, 2026, security researchers from Calif.io publicly disclosed Java4Shell (CVE-2026-114938, CVSS v4.0: 9.2 Critical), a severe heap memory-corruption vulnerability in OpenJDK’s hardware-accelerated (intrinsic) Base64 decoder on certain CPUs. The disclosure coincided with coordinated advisories from the OpenJDK Vulnerability Group and Oracle’s November 17, 2026 security patch release.
Because Base64 decoding is foundational to network protocols, this runtime-level vulnerability can be reached in enterprise applications that pass attacker-controlled input to the affected decoder. Calif.io demonstrated pre-authentication Remote Code Execution (RCE) in default configurations of Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins, and PingFederate. Additionally, post-authentication RCE was achieved in Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, and Netflix Spinnaker, as well as a client-side TLS exploit affecting Java clients connecting to a malicious server.
Immediate patching for affected environments is strongly recommended, alongside other mitigation steps outlined in this advisory.
Zscaler’s security team is actively analyzing this issue across both production and corporate environments. We will continue to update the Zscaler Trust post and this advisory as new information becomes available.
Recommendations
Organizations running Java workloads on x86-64 infrastructure should take the following actions:
- Apply vendor patches immediately: Upgrade OpenJDK, Oracle Java SE, Oracle GraalVM, and all downstream OpenJDK distributions to the patched builds released on or after November 17, 2026 (such as Oracle Java SE 17.0.21.1, 8u513, 21.0.13.1, 25.0.5.1, and 27.0.1.1 security updates) and restart all running JVM processes and containers.
- Apply JVM flag workarounds where patching is delayed: If an immediate JDK upgrade is not feasible, defenders can completely disable the vulnerable assembly code path by passing either of the following flags at JVM startup (e.g., via
JAVA_TOOL_OPTIONSorJDK_JAVA_OPTIONS): -XX:-UseBASE64Intrinsics(Recommended): Disables hardware-accelerated Base64 encoding and decoding intrinsics across all architectures, falling back to safe Java bytecode execution.-XX:UseAVX=2(x86-64 hosts only): Restricts HotSpot to AVX2 instructions, preventing the use of AVX-512 VBMI instructions. Warning: Use this flag only on x86-64 machines; OpenJDK on ARM64 does not recognize this flag and will fail to start.- After adjusting startup command lines and parameters, restart all running JVM processes and containers.
- Check Host CPUs for AVX-512 VBMI Exposure: Because CVE-2026-114938 is hardware-dependent, administrators can determine if the CPU of a Linux system is capable of executing the vulnerable Base64 decoder by inspecting the /proc/cpuinfo file and determining if all four of the following flags are present:
avx512f,avx512bw,avx512vbmi, andbmi2. If a system is not susceptible, the JVM patches should still be applied in accordance with local policy and best practices. - Eliminate public exposure: Place internet-facing Java applications (such as Keycloak, Jira, Confluence, Jenkins, Artifactory, and PingFederate) behind Zscaler Private Access (ZPA).
- Enable reverse-proxy request buffering (Defense-in-Depth): Many remote heap grooming techniques rely on partial HTTP requests to prepare the heap for successful exploitation. Enabling full HTTP request-body buffering at the reverse proxy (e.g., Nginx
proxy_request_buffering on;) disrupts multi-connection timing alignment—though note this is not a complete mitigation for single-request chains (such as Elasticsearch) or upgraded WebSocket tunnels.
Affected JDK Distributions And Versions
CVE-2026-114938 affects OpenJDK 17.0.6 and newer, as well as specific performance/patch builds across Oracle Java SE and downstream OpenJDK distributions as shown in the table below:
Vendor / Category | Affected Products & Versions | Remediation / Patch |
|---|---|---|
OpenJDK (Upstream) | 8.5.0 – 8.5.11 | Apply OpenJDK 2026-11-17 advisory patches, or if patching is delayed, use |
Oracle Java SE / Oracle GraalVM | 8.4.0 – 8.4.26 | Upgrade to the applicable Oracle November 17, 2026 patch (e.g., Java SE 17.0.21.1). |
Downstream OpenJDK Distributions | Amazon Corretto, Eclipse Temurin, Microsoft Build of OpenJDK, Azul Zulu, BellSoft Liberica, SAP SapMachine, Red Hat OpenJDK, Oracle OpenJDK | Upgrade to a build that fixes CVE-2026-114938, or if patching is delayed, apply |
Table 1: Affected JDK distributions and versions.
Hardware prerequisites
The vulnerable assembly routine is only emitted by the HotSpot C2 JIT compiler on x86-64 processors that support AVX-512 VBMI (avx512f, avx512bw, avx512vbmi, bmi2):
- Vulnerable Intel server CPUs: Intel Xeon Ice Lake, Sapphire Rapids, Emerald Rapids, and Granite Rapids
- Vulnerable AMD server and desktop CPUs: AMD EPYC and Ryzen Zen 4 or newer (e.g., EPYC Genoa / Bergamo / Turin, Ryzen 7000/9000 series)
- Not affected: ARM64 processors (e.g., AWS Graviton, Apple Silicon, Ampere Altra) and older x86-64 CPUs lacking AVX-512 VBMI.
Technical Analysis
How it works
While Java is traditionally regarded as a memory-safe language that abstracts raw pointer arithmetic away from developers, the OpenJDK HotSpot Virtual Machine itself relies heavily on C, C++, and hand-rolled assembly intrinsics to maximize throughput on modern hardware. Specifically, OpenJDK’s C2 Just-In-Time (JIT) compiler includes an optimized x86-64 Base64 decoding routine leveraging AVX-512 VBMI vector instructions. Due to an arithmetic underflow when calculating the store mask for improperly padded Base64 tails, malformed Base64 input can be used to trigger a 62-byte heap out-of-bounds write.
Base64 decoding sits at the foundation of many network protocols including HTTP authentication, cookies, authorization tokens, TLS certificate parsing, REST API payloads, and file uploads. Thus, the attack surface for this vulnerability is significant. The figure below shows how malformed input can lead to heap corruption.
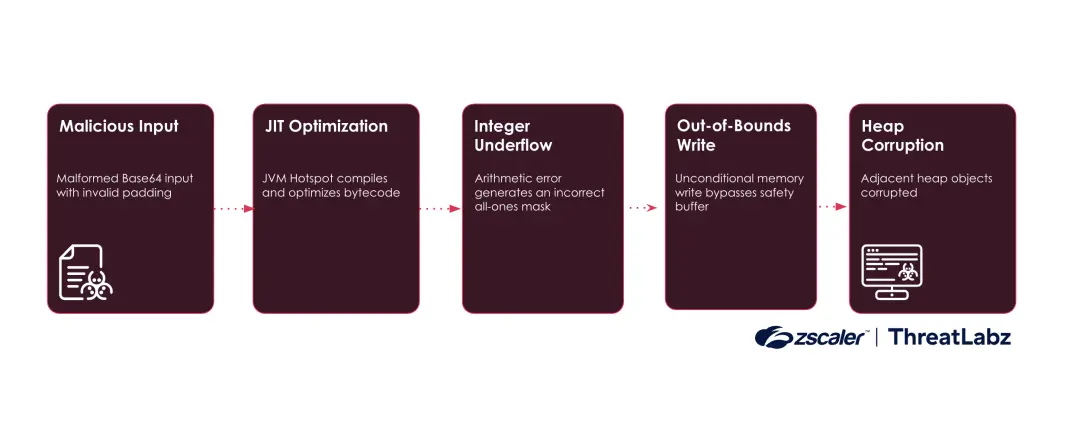
Figure 1: CVE-2026-114938: Java4Shell Exploit Workflow
Conclusion
CVE-2026-114938 (Java4Shell) demonstrates that even memory-safe managed runtimes like Java are susceptible to classic memory corruption when low-level assembly intrinsics miscalculate bounds. Organizations running affected Java builds on x86-64 processors with the required instruction support should patch immediately . Where immediate patching is not possible, restart affected JVMs with -XX:-UseBASE64Intrinsics to temporarily disable the vulnerable code path.
Zscaler Coverage
Zscaler has deployed the following protections for CVE-2026-114938:
Zscaler Deception
Zscaler Deception customers can deploy Private Threat Intelligence decoys for the following applications to detect Java4Shell exploitation attempts and generate high-fidelity alerts:
- Apache Solr
- Jenkins
- Atlassian Confluence
- Atlassian Jira
- Elasticsearch
Customers can configure an orchestration rule to add any IP addresses interacting with these decoys to a firewall block list.
How Zscaler Can Help
The following table outlines typical attack stages for CVE-2026-114938 and the mitigations recommended by Zscaler:
Attack Stage | Recommended Mitigation |
|---|---|
Minimize the external attack surface |
|
Prevent compromise |
|
Prevent lateral threat movement |
|
Prevent data loss |
|
Indicators Of Compromise (IOCs)
Network-level indicators
- JIT warm-up floods: High volumes of rapid, repetitive requests containing valid Base64 fields targeting endpoints that invoke
java.util.Base64.Decoder. - Connection parking (remote heap grooming): Multiple concurrent TCP/HTTP connections from the same source IP delivering partial HTTP request bodies, pausing awaiting TCP ACK, and releasing the final bytes simultaneously.
- Malformed Base64 tail triggers: Base64 strings whose length is a multiple of 64 bytes (64 or 128 characters) immediately followed by an invalid padded tail (
=,==,X=,X==,XY=,===), such asAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA=(64 bytes +=) or128 × "A" + "=". - JavaBleed response anomalies: Abnormally large HTTP responses returned immediately after a spike in
IllegalArgumentExceptionerrors.
Host-level indicators
- Spikes in
java.lang.IllegalArgumentException: High rates ofIllegalArgumentException: Illegal base64character or invalid padding exceptions in application logs. - JVM crash logs (
hs_err_pid*.log): Repeated HotSpotSIGSEGVcrashes in G1 GC routines orStubRoutines::base64_decodeBlock. - Suspicious JVM child processes: Java process spawning unexpected OS shells or reconnaissance commands.


免責事項:このブログは、Zscalerが情報提供のみを目的として作成したものであり、「現状のまま」提供されています。記載された内容の正確性、完全性、信頼性については一切保証されません。Zscalerは、ブログ内の情報の誤りや欠如、またはその情報に基づいて行われるいかなる行為に関して一切の責任を負いません。また、ブログ内でリンクされているサードパーティーのWebサイトおよびリソースは、利便性のみを目的として提供されており、その内容や運用についても一切の責任を負いません。すべての内容は予告なく変更される場合があります。このブログにアクセスすることで、これらの条件に同意し、情報の確認および使用は自己責任で行うことを理解したものとみなされます。