Access decided per user, per app, per risk, across 3500+ AI tools, approve, isolate, or block. Without slowing anyone down

Security stops being the department of no: every team gets access to the AI tools they’re asking for, matched to the risk each tool actually carries

One living access policy across every AI application, instead of an allow list that’s outdated the week it ships

A middle path between approve and deny: risky apps can be isolated or used with caution instead of blocked outright, so work keeps moving while exposure doesn’t
Yes is a Policy, This is how
Access decided per user, per app, per risk, across 3500+ AI tools. Policy reflects who is asking, what they are asking for, and how risky the tool actually is.
Approve, isolate, or caution instead of blocking outright. Risky apps get a safer way to run, so work keeps moving while exposure doesn’t.
AI app risk classifications refresh continuously from live traffic across the Zscaler cloud. An allow list is outdated the week it ships. This is not a list.
ThreatLabz watched 18,000 TB of enterprise data move into AI tools in a single year
Every week your workforce finds a new AI tool, and every week the same question lands on security: yes or no? Blanket blocking pushes AI into the shadows. Blanket approval hands your data to tools nobody vetted. AI Guard for Users replaces the yes-or-no trap with access decided per user, per app, per risk, and a middle path between approve and deny. Security stops being the department of no, and the business gets the AI it is asking for, with exposure that stays inside the lines.

How it works
Access Decisions, Made in Real Time

Access decided per user
per app, and per risk, enforced inline on every AI interaction

Risk classifications
for 3500+ AI tools, refreshed continuously from live traffic

Four answers instead of two
allow, block, isolate, or caution the user in the moment

Separate policy
for corporate tenants and personal accounts of the same AI app

Coverage across web AI
SaaS AI, and the AI embedded inside the apps you already run

Usage telemetry feeds
your AI inventory, so every access decision makes the map more complete

Policy defined once in Zscaler
applied to AI access alongside everything else you govern
Use cases
Give everyone AI, on your terms
Your workforce is adopting AI faster than any review process can keep up with. AI Guard for Users turns that demand into governed access: the right AI, for the right people, at the right level of risk.
Marketing asks for the AI tool the whole industry is talking about. Instead of a month in review, access is approved with risk-matched controls, and the team is working the same week.
An unvetted tool mimics a popular AI app. Risk classification catches it, and policy isolates it instead of trusting it, so curiosity does not become exposure.
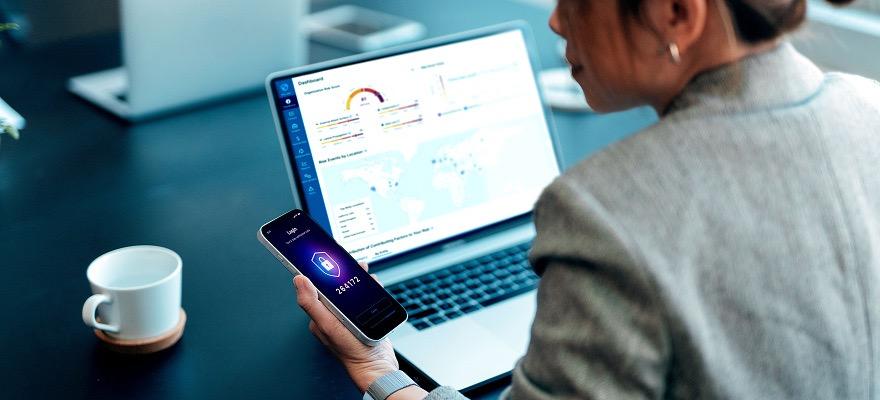
The same AI app, two contexts. The corporate tenant gets approved with controls; the personal account gets cautioned or contained. One app, two right answers.
When the audit asks who used what AI and under which policy, the answer is one report of decisions and usage, not a reconstruction from tickets.
Better together
Part of Zscaler AI Security
Access is the front door. The platform governs everything past it.

AI Guard for Apps
prompts and responses inspected in real time inside the tools you approve.

AI Endpoint Security
the same access policy reaches AI tools living on the device.

AI Access Graph
every approved app mapped to the data it can actually reach.

AI Gateway
when tools become agents, per-action authorization takes over.
Zscaler Security For AI Overview
Q&A
Access is decided per user, per app, and per risk, enforced inline on every AI interaction.
Risk classifications for 3,500+ AI tools, refreshed continuously from live traffic across the Zscaler cloud.
Yes. Access is decided per user and per app, so policy can be scoped to specific teams instead of applied as one blanket rule.
They get classified and risk-rated like everything else, and policy can isolate or caution them instead of blocking outright.
No. Access is approved with risk-matched controls in real time, so most tools reach a decision without a manual review cycle.