
Turn Zero Trust Traffic into Investigation-Ready Evidence with Cloud-Based Traffic Capture
Capture on-demand policy-driven traffic for your SOC, and stream enriched packet data to leading NDR platforms — no on-prem TAPs, no packet data retained in the Zscaler cloud.
Give your SOC the context to act faster
Give security practitioners and threat researchers easy access to policy-driven traffic captures and zero-trust telemetry for efficient security forensics and incident response—without requiring additional appliances.
Unified visibility across hybrid environments
Early threat detection with NDR
Improve compliance and forensic readiness
THE PROBLEM
The cloud edge that protects your traffic also shields it from sensors meant to inspect it
Cloud and remote traffic can create NDR blind spots
Remote and internet-bound traffic never reaches traditional corporate TAPs and sensors, limiting what NDR tools can analyze.
Fragmented context slows investigations
When packet data, identity, access, and security telemetry live in separate workflows, analysts spend time correlating evidence instead of investigating.
High capture and storage overhead drives up costs
Legacy PCAP solutions collect traffic indiscriminately, driving up bandwidth, storage, and infrastructure costs.
SOLUTION OVERVIEW
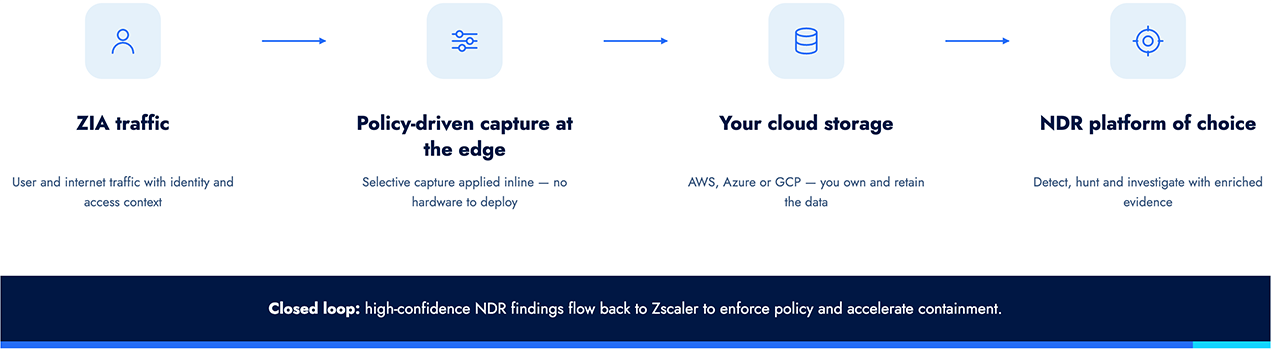
Using granular policies—by user, application, service, country, or destination IP—Traffic Capture forwards captured packets as PCAPNG files to your cloud storage, where supported NDR partners ingest them for deep analysis, threat hunting, and forensic investigation. No packet data is ever stored in the Zscaler cloud.
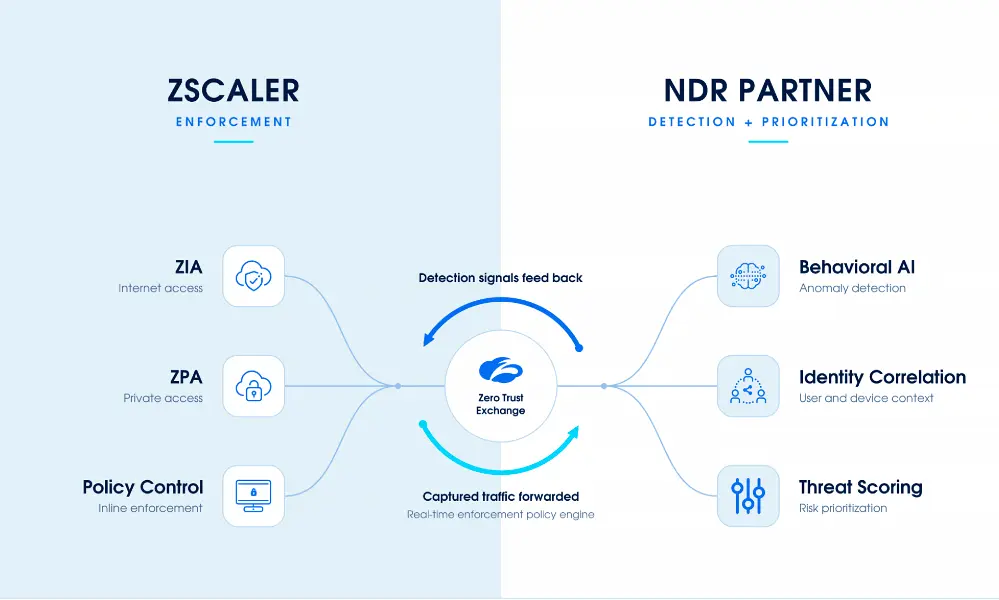
How Traffic Capture moves evidence without on-prem taps
By correlating this traffic with ZIA and ZPA context, your NDR platform detects the early threat indicators that need continuous traffic capture for anomaly and time series analysis—slow and hidden C2 traffic, lateral movement, and compromised identities—and associates detections with the relevant user and device context.
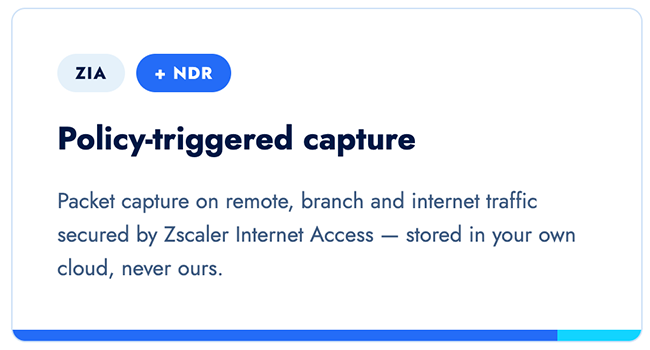
For teams without an NDR, policy-driven traffic captures from ZIA provide SOC and IR analysts with on-demand, replayable evidence for investigations and help support retention requirements—all from capture data you own.
BENEFITS
Turn SASE traffic into forensic-grade telemetry for the SOC team
Security teams need to understand the content traversing your environment to conduct effective forensic analysis, investigate incidents, and ensure compliance. Traditional PCAP solutions lose visibility when user traffic no longer crosses the physical sensors they depend on.
See what the cloud leaves invisible
Extend packet-level visibility to selected remote and internet-bound traffic that traditional corporate sensors may never see.
Maximize NDR investments with cloud-native SASE visibility
Feed enriched captures to NDR partners to surface early indicators of lateral movement, slow and hidden C2 traffic, account compromise, and privilege escalations that may bypass traditional tools.
Investigate with evidence, not fragments
Give NDR analysts replayable captured traffic and rich forensic context to confirm attacks, cut false positives, and build stronger playbooks.
Bring Zscaler traffic and Zero Trust telemetry into supported NDR and analytics platforms to deepen visibility and accelerate security operations across distributed environments.
Use Cases
Turn traffic evidence into SOC action
Conduct in-depth forensics
Retain traffic over extended windows for threat hunting and incident response to validate detections and rule out false positives.
Neutralize low-and-slow command-and-control
Hunt using TLS fingerprints and behavioral signals to catch evasive C2 traffic that rotates infrastructure to slip past destination-based controls.
Expose compromised identities and living-off-the-land activity
Tie abnormal identity behavior to the apps a user is touching to stop fileless SaaS attacks before data leaves.
Comply with regulations
Retain packet-level evidence in your own cloud to satisfy HIPAA, PCI DSS, and federal retention mandates.
Frequently Asked Questions
A cloud-native capability in Zscaler Internet Access that provides continuous traffic capture based on rich policy criteria—by user, application, service, country or IP-Packets are packaged as PCAPNG files and written to your cloud storage for an NDR platform to ingest for AI-based evidence and playbooks.
Zscaler acts as a cloud-native, policy-driven switchboard to collect traffic. It de-encapsulates Zscaler headers at the cloud and Private Edge, transforms the captured packets into PCAPNG files, and streams them to your cloud storage with enriched metadata for user, device name, and location info. Your NDR platform then ingests them, eliminating the need for manual correlation to identify the user, device, or location that generated the traffic of interest for the SOC.
No, packet capture and streaming run asynchronously and out-of-band. The heavy lifting of post-processing and transformation is handled by Zscaler’s distributed global and private edges, ensuring no latency impact on active user connections or application performance.
Traditional NDR sensors only see raw, rotating IP addresses. Zscaler enriches the captured packets with ZIA/ZPA identity context, instantly tying every NDR alert to a real, authenticated user and device. This eliminates manual IP-to-user correlation during incident response.
You own and store all of your data. Zscaler writes PCAPNG files directly to your private cloud storage (such as AWS, Azure, or GCP). Zscaler never stores, caches, or retains any of your packet data—ensuring total privacy and seamless regulatory compliance.