Overview
Give your team every AI tool they need
Protect your organization with the only platform built to see every asset and secure every connection in the path of AI.
Trusted by the Most Demanding Teams
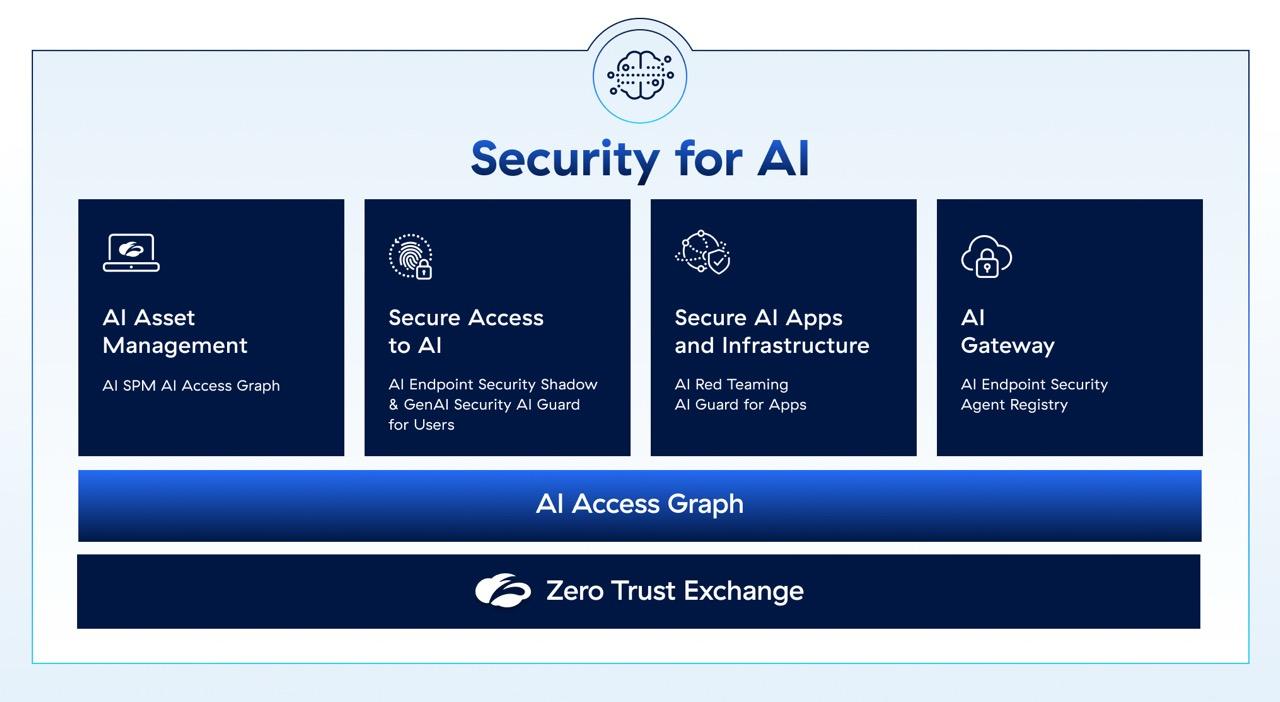
Auto-discover every AI asset – models, agents, MCP servers, shadow AI – and trace data-to-AI lineage across 2,900+ apps in one unified view.

Control who uses AI and how: block access by role in real time, filter sensitive data from LLMs, and govern agent-to-agent traffic.

Test 5,000+ attack scenarios across text, image, voice, and documents, then fix gaps directly – mapped to MITRE ATLAS, NIST, and EU AI Act.

Route, secure, and govern every AI transaction from one central control plane – with inline DLP and Zero Trust applied to every model, agent, and API call in real time.

Customer Success Stories




FAQ
AI red teaming tests and secures AI systems, especially large language models (LLMs), by simulating real-world attacks and vulnerabilities like prompt injection or data poisoning. This approach ensures AI models are robust, safe, and aligned with regulations. Organizations use it to reduce risks, improve model reliability, and protect against threats as AI becomes crucial for business and innovation. Learn more.
Zscaler AI Security protects the full AI life cycle by combining automated red teaming, dynamic risk assessment, and advanced guardrails. It identifies vulnerabilities, fixes risks with real-time remediation, and hardens prompts to prevent exploits like data leaks. Tools like Policy Generator align AI systems with compliance standards, ensuring safe development, deployment, and operation in enterprise environments.
AI Security prevents generative AI data leakage by blocking unauthorized tools, monitoring risky interactions, and enforcing strict data loss prevention (DLP) policies. Hosting AI tools privately and controlling access with zero trust measures protect sensitive data from being shared or exposed. With these controls, organizations can safely use AI while staying compliant and preventing breaches.
AI security posture management (AI-SPM) secures AI models, data, and infrastructure by identifying risks like misconfigurations, data leaks, or adversarial attacks. It provides visibility into AI assets, enforces compliance with regulations, and mitigates vulnerabilities throughout the AI life cycle. AI-SPM ensures safer AI adoption by protecting sensitive data, managing risks, and maintaining secure, well-governed AI operations.