
Eliminate Lateral Movement with OT/IoT Segmentation
Extend zero trust inside the factory and hospital—with no forced upgrades or outages.

Zero lateral movement. Zero attack surface.
Agentless zero trust segmentation eliminates the risk of lateral movement inside your factory by isolating production lines and individual endpoints without adding software.

Easily segment IT from OT and IoT

Eliminate east-west firewalls and NAC

Deploy in hours with no downtime, agents, or VLAN readdressing

Legacy infrastructure mixed with modern systems
Decades-old OT devices can’t be patched or upgraded, leaving critical vulnerabilities.

More third-party access
Partners, vendors, and outsourced support demand secure, seamless communications.

Flat, complex networks
Traditional architectures make it easy for threats to spread once inside.

Rising cyberattacks
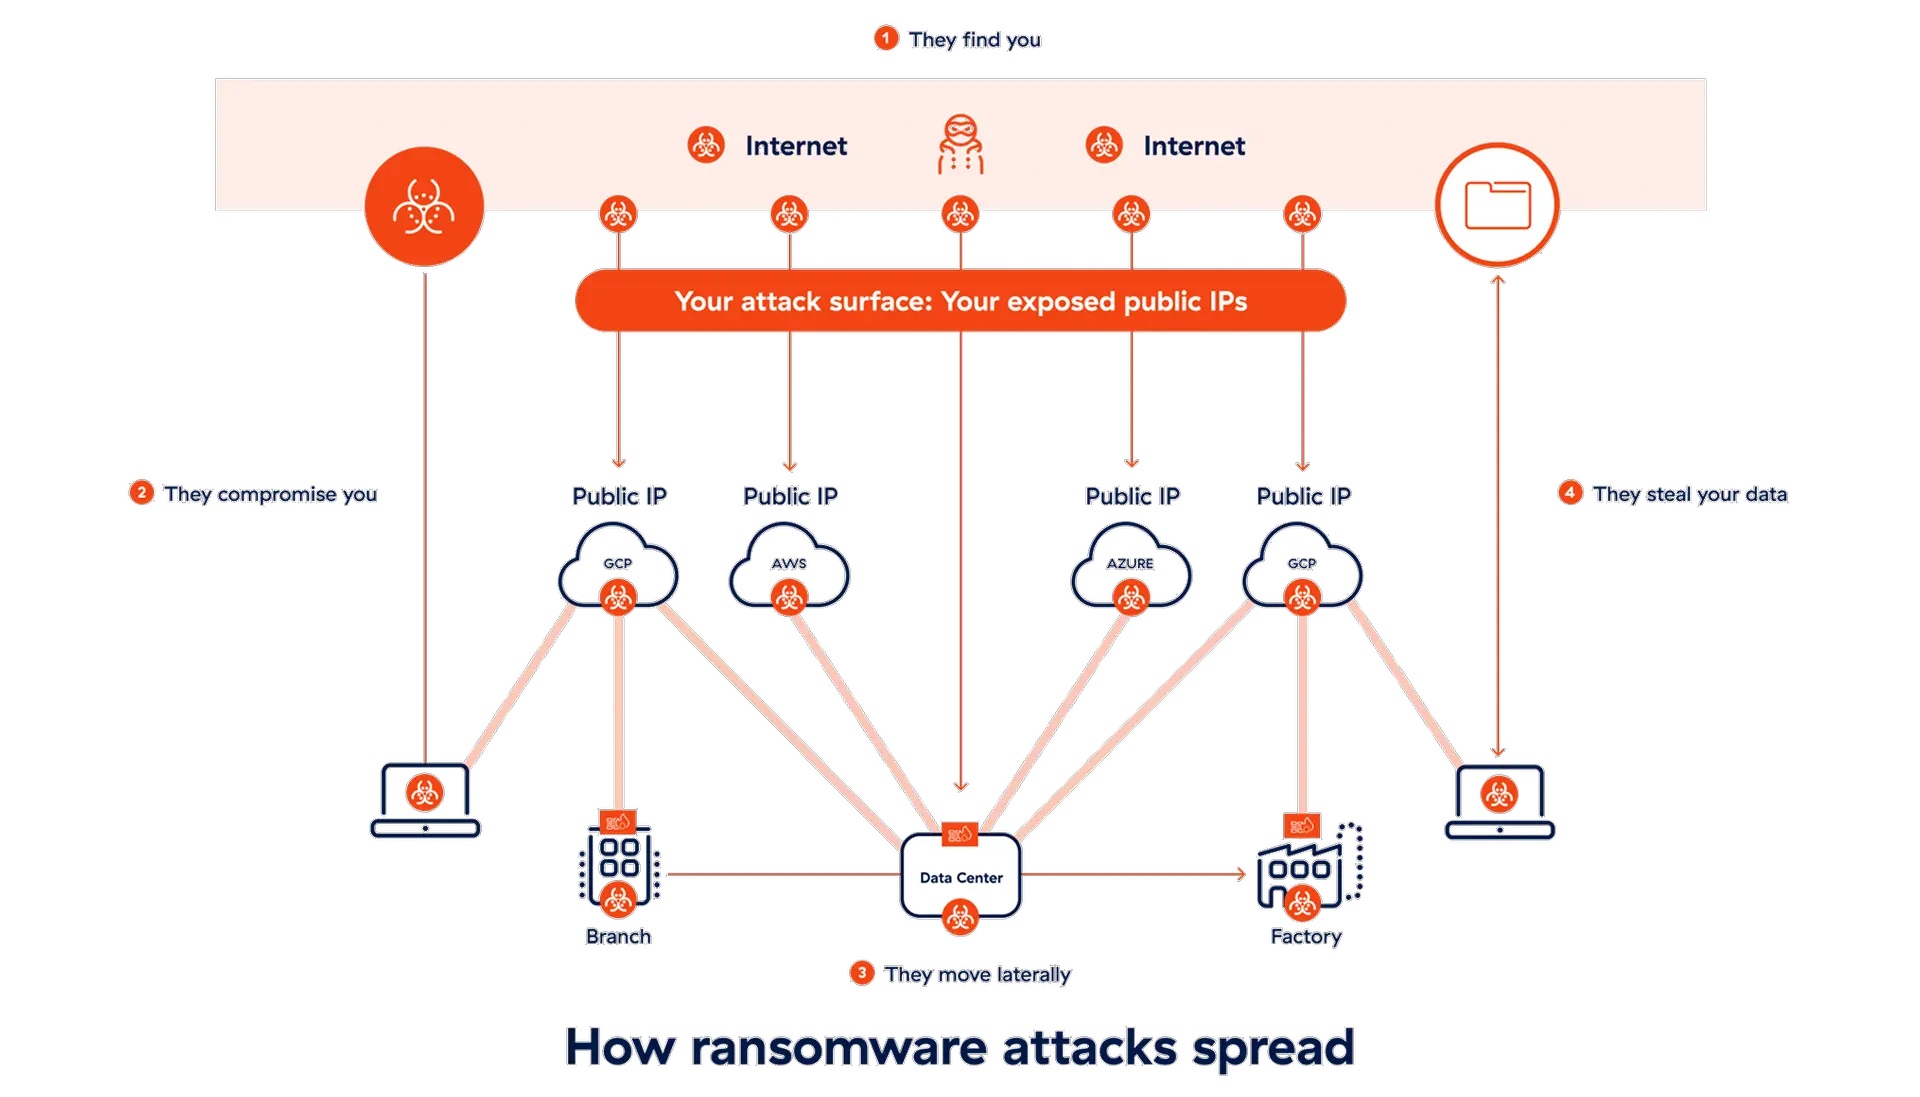
Industrial sectors, including manufacturing, were subject to 22% of ransomware attacks last year.
Solution Overview
Zscaler OT/IoT Segmentation is an agentless solution that replaces firewalls, NAC, and manual VLANs. Fully isolate your devices without agents, upgrades, or downtime. Keep legacy machines and headless systems safe and operational. With automated policies, you get security that’s simple and works seamlessly, without slowing down production.

Solution Details
Improve uptime and simplify operations
Eliminate manual configuration errors. Empower local OT teams to handle routine problems, easing trouble ticket pressure on your IT team.

CAPABILITY
Isolate every device into a segment of one (using /32).
Group devices, users, and apps for policy enforcement automatically.
Enforce dynamic policy for east-west traffic and IT/OT and Purdue layer separation.
Eliminate east-west firewalls, NAC appliances, and agent-based software.
Ransomware Kill Switch
Automate incident response with simple, user-selectable attack surface reduction. Just choose a pre-set severity level to progressively lock down known vulnerable protocols and ports.

Capability
Align protection to real-time risk with four selectable policy levels based on severity.
Restrict critical infrastructure access to known MAC addresses only.
Integrate seamlessly with your existing SIEM and SOAR for automated response.
Instantly block the protocols most favored by ransomware, like RDP/SMB and SSH.
Start by discovering every OT device
Discover and classify all device assets in real time, with full east-west visibility and control. Take back control with no endpoint agents to deploy or manage.

Capability
Automatically discover and classify devices in east-west LAN traffic.
Baseline your traffic patterns and device behaviors as well as identify authorized and unauthorized access.
Gain accurate network insights to support performance management and threat mapping.
Leverage third-party integrations for querying, tagging, and alert monitoring.
Benefits
What sets our OT/IoT Segmentation solution apart?

No endpoint agents
Fully segment legacy servers, headless machines, and IoT/IoMT devices that can't accept agents.

A unified solution
Seamlessly deploy integrated OT/IoT Segmentation, Zero Trust SD-WAN, and Privileged Remote Access (PRA).

Maximum uptime
Deploy quickly and with no hardware upgrades or VLAN readdressing. Extend the life of legacy equipment.
Customer Success Stories


Kingston Technology reduces overall risk with OT/IoT Segmentation


Tillys deploys OT/IoT Segmentation nationwide in four days


Request a demo
See and secure your entire critical OT/IoT Segmentation with Zero Trust Device Segmentation. Let our experts show you how.