
Secure Developer Workflows Without Slowing Innovation
Gain visibility into traffic that developer tools generate and control it with granular inspection policy.
The problem
Developer environments generate high-value traffic that often goes uninspected
Implementing SSL/TLS inspection in developer environments is challenging because developers use many tools and apps that may not trust the default system certificate store or perform certificate pinning, leading to unexpected errors. As a result, many organizations bypass inspecting traffic for developer apps.
Yet inspecting traffic in developer environments remains critical to enterprise security: Over 87% of threats are delivered over encrypted channels1 yet most development environments go uninspected because applying TLS/SSL inspection to developer tools breaks them.

The inspection problem is structural
Developer tools like Python, Docker, and Git maintain their own custom certificate trust stores instead of using the system default. When a proxy-based solution like Zscaler Internet Access attempts SSL/TLS inspection, these tools can't validate the proxy-generated certificate, causing connections to fail and apps to break.

Third-party and open source code is a primary attack vector
Developers routinely pull packages, scripts, libraries, and installer files from external repositories. Malicious code, backdoors, and malware can be embedded in these files, including in file types and oversized files specifically crafted to evade traditional security tools.

Speed-to-market pressure amplifies risk
DevOps teams under pressure to release rapidly often prioritize velocity over security hygiene. Without automated controls in place, a developer unknowingly introducing a compromised dependency can push a backdoor straight into your production codebase.
Benefits
Inspect and manage developer-tool generated traffic

Inspect encrypted developer traffic at scale
Automate TLS/SSL inspection across 30+ popular developer tools and frameworks without connectivity errors or workflow disruption. Policy-based controls apply inspection broadly while maintaining targeted exemptions where needed.

Stop threats before they reach your codebase
AI-powered cloud sandboxing analyzes scripts, packages, and files from third-party repositories in real time to catch malware, backdoors, and hidden malicious code before it's embedded in your applications.

Enable developers without creating blind spots
Zscaler integrates with existing MDM and endpoint management workflows to deploy certificates automatically so developers keep working in their preferred tools while security teams gain the visibility they've been missing.

Full visibility plus granular policy control
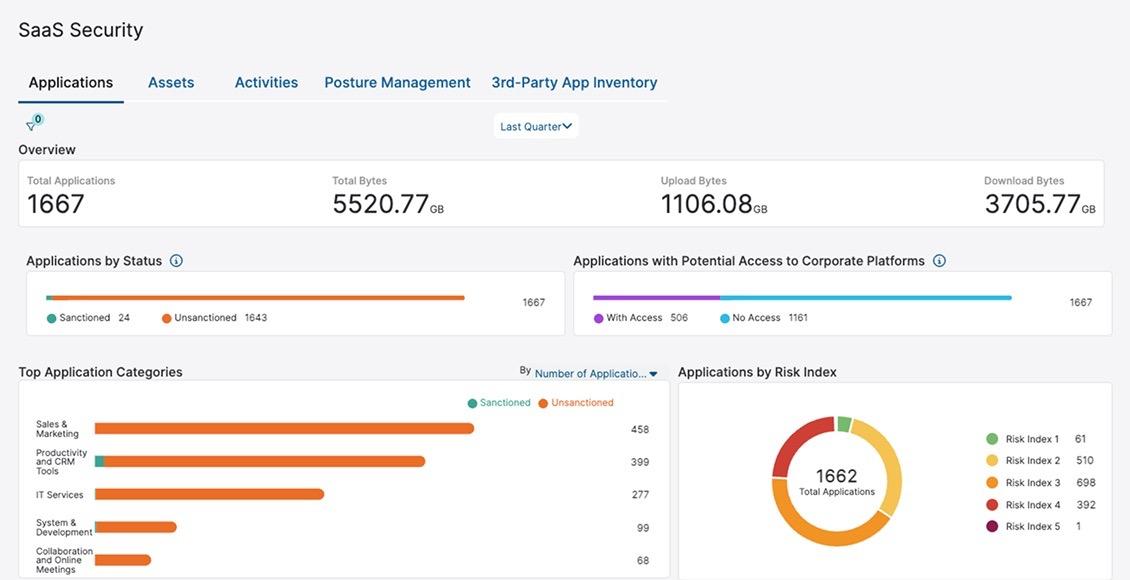
Pre-defined developer app categories, risk scoring, and SaaS security reporting give security architects and cloud ops teams the data they need to distinguish sanctioned from shadow IT developer tooling.
USE CASES
Integrate Zscaler with developer workflows to release rapidly and stay secure
Leverage Zscaler’s pre-generated report of all developer apps with associated Risk Score
Use built-in developer app and URL categories and distinguish sanctioned vs. unsanctioned apps with granular risk-based controls
Secure rapid deployments with automated certificate deployment to enable SSL/TLS inspection without connectivity errors using mobile device management (MDM) solutions
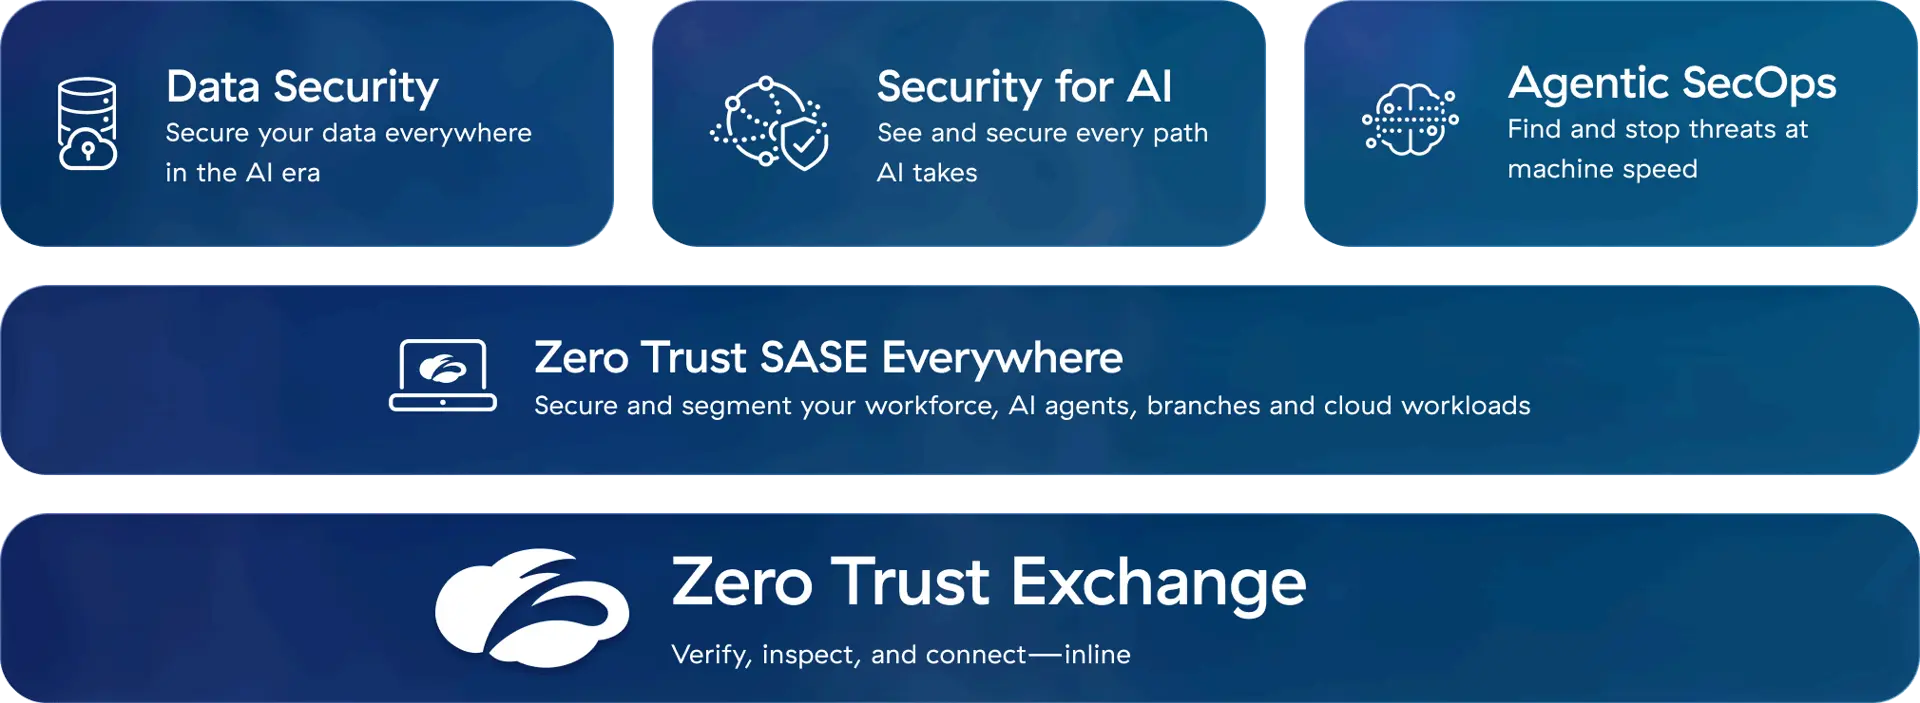
La plate-forme Zscaler
La plateforme de cybersécurité adaptée à l’ère de l’IA, bâtie sur le Zero Trust pour protéger les utilisateurs, les workloads, les sites distants et les appareils grâce au plus grand cloud de sécurité inline au monde.
Learn and explore resources
Frequently Asked Questions
Over 86% of all threats are delivered over encrypted traffic: not inspecting traffic in developer environments increases risk and leaves your organization vulnerable. Moreover, development teams release often and rapidly so your organization remains competitive and gains market share—but that speed can also lead to an oversight that causes a security incident. In this context, inspecting traffic and new files before they are embedded in the developer’s code base is paramount to maintaining a strong, resilient security posture.
In the past integrating encrypted traffic inspection has proven problematic for development teams: their code does not reference the correct certificate store or they design their app to employ “certificate pinning,” a security technique that prevents man-in-the-middle (MITM) attacks and secures access to your organization’s applications. Unfortunately, both scenarios prevent traffic TLS/SSL inspection via proxy.
Zscaler now provides the means for your security or IT teams to empower developer teams with scalable, policy-based TLS/SSL inspection or, in the case of certificate-pinned apps, easily bypass inspection for this category of apps.
Outright blocking means your developers can’t directly introduce risk during development, prior to releasing new code to production in your environment. That said, without other DLP policy they could inadvertently introduce third-party code into the overall code base, resulting in malicious code with a backdoor or other threat being introduced into a production app.
From a productivity standpoint, blocking access to other developer resources puts your software engineers at a competitive disadvantage: with ZIA’s SSL/TLS inspection integrated with their workflows, they can still remain competitive while preventing threats from compromising your organization’s security.