
FedRAMP Authorized US Federal Security
Securing federal government agencies with the power and scale of the cloud.


Confidently embrace the cloud with a zero trust architecture that enables the seamless, secure exchange of sensitive data.

Federal civilian agencies
Protect agency and citizen data with our FedRAMP High JAB and Moderate Agency Authorized solutions, serving 14 of the 15 US Cabinet-level agencies.

Department of War/Intelligence
DoW IL5 authorized. From the test lab to the tactical edge, extend secure access to data and applications for employees, contractors, and allies from any device or location.

Federal systems integrators
Meet stringent FedRAMP and CMMC requirements for systems integrators and the Defense Industrial Base to work with the federal government.
Public Sector Summit 2026
Missed the Zscaler Public Sector Summit 2026? Watch the on-demand sessions now!

Solution Overview
The Zscaler Zero Trust Exchange™ platform helps agencies secure, simplify, and transform their operations. With a cloud native architecture delivered from 160+ PoPs worldwide, we support civilian agencies, DoW, Intelligence, and contractors in their mission to protect the United States.
- Protect and enable users with fast, secure, reliable access.
- Secure workloads against sophisticated threats and data loss.
- Secure OT/IoT devices to increase adoption and productivity.

Benefits
Keep your agency efficient and secure

Reduce costs and complexity
by replacing legacy VPNs, firewalls, and more with cloud native zero trust architecture

Improve user experiences
by providing fast, secure access from anywhere while eliminating security bottlenecks

Simplify compliance
with a unified platform, authorized and accredited at the highest levels of federal requirements
Use Cases
Modernize confidently with a zero trust architecture

Deliver user- and app-aware threat protection and risk-based policy enforcement as close to the user as possible, providing identical protection from any device or location.

Give users and devices secure access to the internet and cloud applications, supporting guidance from CISA, DISA, NIST, IPv6, and TIC 3.0.

Secure data and prevent cyberattacks across all cloud channels—inline, at rest, BYOD, SaaS, and public clouds—with a single, unified platform.

Provide secure access to the internet, internal applications, and compute resources for DoW and military components. Give warfighters and mission partners access to critical data without compromising the security of the underlying architecture.

Enforce controls that fully map to CMMC 2.0. Our platform also supports CMMC Level 3 controls and NIST 800-172 with FedRAMP Moderate, FedRAMP High, DoW IL5, and other accreditations.
Customer Success Stories

FCC replaces TIC with zero trust, with 70% cost savings

US govt. civilian agency replaces VPNs and MPLS


Compliance Achievements
Transform securely while meeting the highest standards of government compliance
The world's most accredited cloud platform for US federal security

FedRAMP
Zscaler Private Access™ and Zscaler Internet Access™ have both achieved official Federal Risk and Authorization Management Program (FedRAMP) High Authority to Operate (ATO) status.

AICPA
We have received Service Organization Control (SOC) 2, Type II Certification, validating that our security controls are in accordance with the American Institute of Certified Public Accountants’ applicable Trust Services Principles and Criteria.

GovRAMP
Zscaler Private Access and Zscaler Internet Access have both achieved Authorized status with the GovRAMP Authorized Product List.

ISO 27001
The Zscaler Zero Trust Exchange platform is fully compliant with the ISO 27001 security standard for its cloud services and operations.

ISO 27018
The Zero Trust Exchange platform is fully compliant with the ISO 27018 for cloud privacy protection.

FIPS 140-2
Zscaler is compliant with the Federal Information Processing Standard (FIPS 140-2), meeting NIST requirements for cryptographic modules.

Impact Level 5 (IL5)
Zscaler Private Access has achieved a Provisional Authorization (PA) at Impact Level 5 (IL5), as published in the Department of War Cloud Computing Security Requirements Guide.

VPAT/Section 508
In recognition and support of the Electronic and Information Accessibility Standards defined by Section 508 of the Rehabilitation Act, we publish accessibility self-assessments of our products using Voluntary Product Accessibility Templates (VPATs).
Federal Government
Alliances


Channel


Service Providers


Federal System Integrators


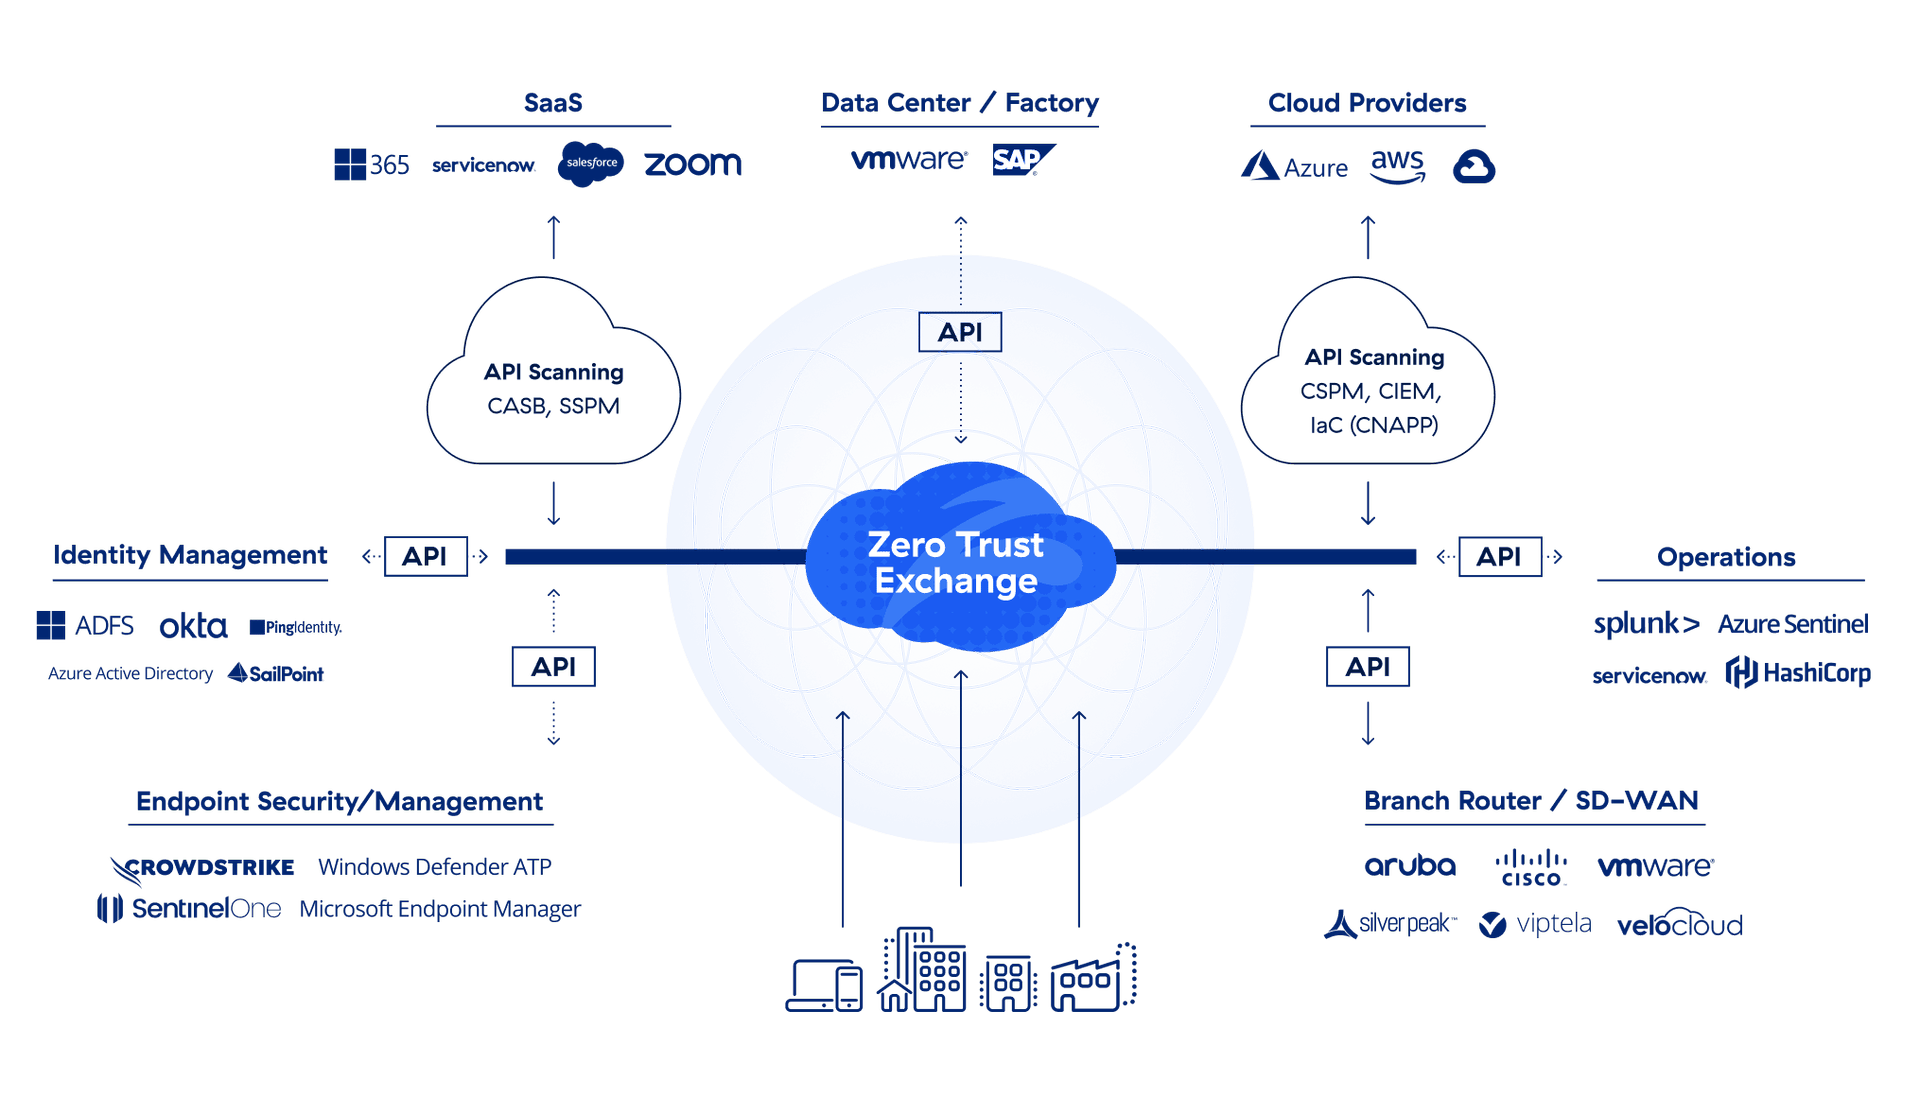
Technology Ecosystem
Ecosystem of best-of-breed platforms
FAQ
FedRAMP High and FedRAMP Moderate are US govt cybersecurity designations for systems that handle data of different sensitivity levels. FedRAMP Moderate is for less sensitive data (e.g., personal or proprietary data), and requires 325 security controls. FedRAMP High mandates nearly 100 further security controls to protect highly sensitive data such as Controlled Unclassified Information (CUI).
The third major version of Cybersecurity Maturity Model Certification (CMMC 3.0) is effective as of December 16, 2024. The DoW expects to begin including CMMC 3.0 requirements in contracts in phases, starting in mid-to-late 2025. CMMC 3.0 will be part of all DoW contracts as early as October 1, 2026.
Request a Demo
See why a zero trust architecture is the most effective approach to transforming federal government cybersecurity.