Overview
Detect more threats and respond faster around-the-clock
Activate AI-powered detection engineering, threat intelligence, research, and hunting teams to keep you ahead of emerging and advanced threats. Enrich investigations with ZIA context and automatically enforce ZIA policies to contain threats faster.

Eliminate noise
and focus on real threats

Maintain 24/7 coverage
so your team can sleep at night

Rely on a trusted partner
when you need experience and expertise
Product Overview
Managed Detection & Response (MDR) taps our in-house experts to detect, manage, respond to, and remediate threats at scale for your organization, freeing your team to focus on other things.
Leveraging our Agentic SecOps platform and supported by agentic workflows and deep ZIA integration, our experts deliver high-fidelity, actionable detections with comprehensive response catered to your organization, so you can move faster from detection to containment with the employees you already have.

Benefits
Focus on active threats and business-specific risks

Detect 4x more threats
Find threats your point solutions miss.

Reduce noise by 99%+
Eliminate false positives to focus on signals (not noise).

Act on clear insights and intelligence
Take precise next steps with threat intel and ZIA network and user insights.

Respond 10x faster
Contain threats with expert guidance, automation, and hands-on-keyboard support.
Solution Details
AI agents
AI agents perform triage, enrichment, investigation, and more so your team can move from alert to action faster.

Enrich alerts with device context, user login history, IP intelligence, and more before triaging.
Filter out difficult-to-tune alerts with short natural language prompts.
Automatically ask and answer critical investigative questions before they get to your team.
Provide guidance for containment, eradication, and hardening specific to each threat detected.
Elite expertise
Activate a 24/7 team of detection and response specialists who validate threats, reduce noise, and help you handle advanced attacks without adding headcount.

Continuously develop analytics for high-fidelity detections and optimize processes for efficient responses.
Translate attacker tactics and trends into clear detection priorities and practical guidance, with context your analysts can act on immediately.
Augment ZIA-focused hunting with threat hunting across your clouds, endpoints, and identities, receiving scoped findings with evidence and next steps.
Track new techniques, tools, and campaigns, and feed learnings back into detection and response engineering processes.
Automation

Automatically block URLs and IoCs via ZIA, isolate endpoints via EDR, suspend users via your IDP, and more.
Configure triggers and actions in minutes without scripting.
Have the option for team oversight to initiate specific response actions—or choose to automate.
Send MDR alerts to your SIEM, SOAR, or ITSM platform to align with your existing workflows.
Reporting
Visualize detection, response and hunting outcomes and how you compare to similar organizations.
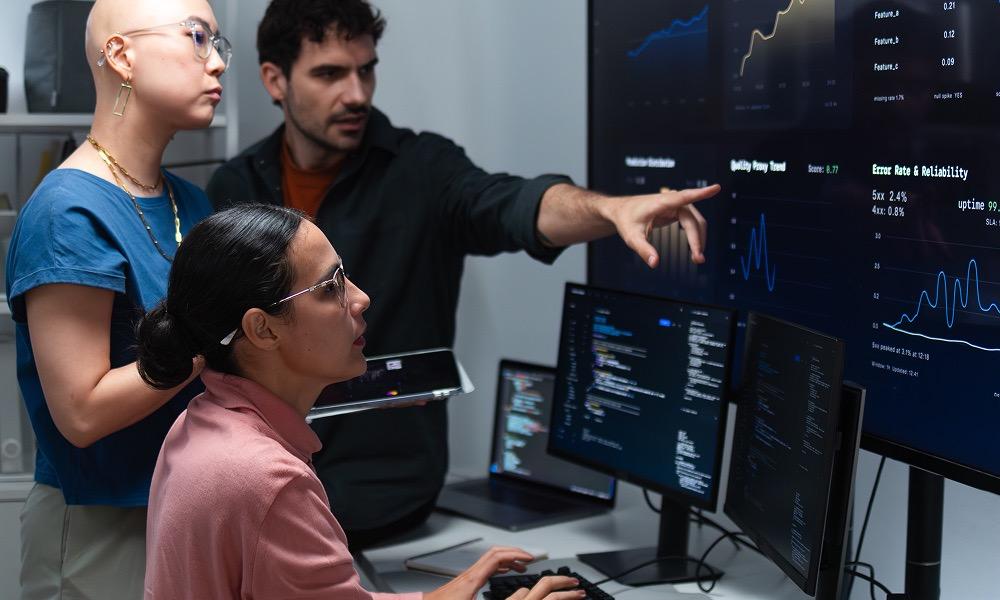
Understand how fast and accurate your detection and response program is, and how it’s changed over time
View writeups of every threat hunt’s hypothesis, observations, recommendations, and findings
Learn how your threat posture compares to similar organizations across industry, employee count, and the entire MDR customer base
Determine the adversaries and tools most commonly targeting your organization and compare those trends to MDR customers from your industry
Use Cases
Proven protection that never clocks out

Stay ahead of modern ransomware. See how MDR provides high-fidelity detection of ransomware precursors, rapid containment and remediation of threats before impact, transparent threat hunting, and reporting on threat group and tool prevalence in your environment.
Streamline your response to user-reported phishing attempts. See how Zscaler combines AI and human expert analysis to analyze reported phishing emails, as well as how we make it easy to analyze reported phishing trends and send customized user feedback automatically.

Simplify cloud threat detection in complex environments. Zscaler MDR unifies data from AWS, GCP, Azure, and leading cloud security tools like Wiz to detect and stop cloud threats before impact. Our comprehensive integrations and 24×7 cloud security expertise help you manage your entire cloud attack surface—from control plane to workload—proactively addressing both active threats and risks like vulnerable software, misconfigurations, and toxic combinations.

Gain cost-effective storage that improves your security posture. See how you can store MDR data or other raw data (JSON, syslog messages, anything line delimited that you can write to an S3 bucket) for any length of time specified by you. You can query that data yourself or let Zscaler MDR leverage those sources for our threat investigations.
Get new insights from your ZIA telemetry and automatically update policies to contain threats. Take the quickest path from detection to protection by using your Zscaler telemetry and inline controls for detection, investigation context, and automated responses like adding domains, URLs, or IPs to deny lists and applying browser isolation or conditional access policies.
Key Domains
Defend against threats across your environment

Identity
Protect your users’ email, identities, and SaaS apps

Endpoint
24×7 endpoint threat protection across your organization

Cloud
Understand and manage your cloud-based attack surface

Prevent potential business and financial impact from email attacks

Network
Get new insights from your ZIA telemetry and automatically contain threats.

Dave Coughanour

Robert Williams

Jason Thomas
FAQ
MDR is a cybersecurity service that helps organizations rapidly detect, analyze, and mitigate cyber threats. It goes beyond simple monitoring, taking that extra step to investigate and remediate threats before they can have a negative impact.
MDR integrates with a wide range of security tools to provide comprehensive detection and response across your environment. Find the list of MDR integrations here.
No, MDR doesn’t replace your existing SOC. MDR complements and enhances your existing SOC. Think of us as your trusted partner, offering the expertise, tools, and support needed to make your SOC more efficient.
MDR can integrate with Zscaler Internet Access (ZIA) to automatically enrich investigations with web and firewall telemetry, including user and application context, so you can confirm threats faster without pivoting between tools. When a threat is confirmed, MDR can also trigger automatic response actions in ZIA—such as blocking malicious domains, URLs, or IPs—to help contain risk quickly and consistently across users.