Zscaler and Aruba automate optimal security policy enforcement for any user, application, or device across any location with true zero-touch provisioning.
WHY ZSCALER + ARUBA
As you migrate applications to the cloud, the change in traffic patterns drives a need for a new wide area network (WAN) architecture alongside a review of your security model. The process of configuring policies in a complex new model is often error-prone, and time-consuming, exposing your organization to security risks.

BENEFITS
Zscaler and Aruba: Enabling secure enterprise SD-WAN

Highest quality of experience
Empower your IT teams to be more responsive to business needs. Provision and secure new sites with zero-touch setup while increasing productivity and user experience with 99.999% availability.

Business-driven design
Leverage a SASE architecture to boost performance and enhance reliability. Streamline branch IT to improve economics and make your cloud investments count.

Automated connectivity, always-on security
Enable infrastructure to automatically adapt to changing business conditions. Centrally define security requirements once to deliver optimal connectivity and security to all users, guests, and devices anywhere.
HOW IT WORKS
Secure WAN access with Zscaler and Aruba
Centralized management
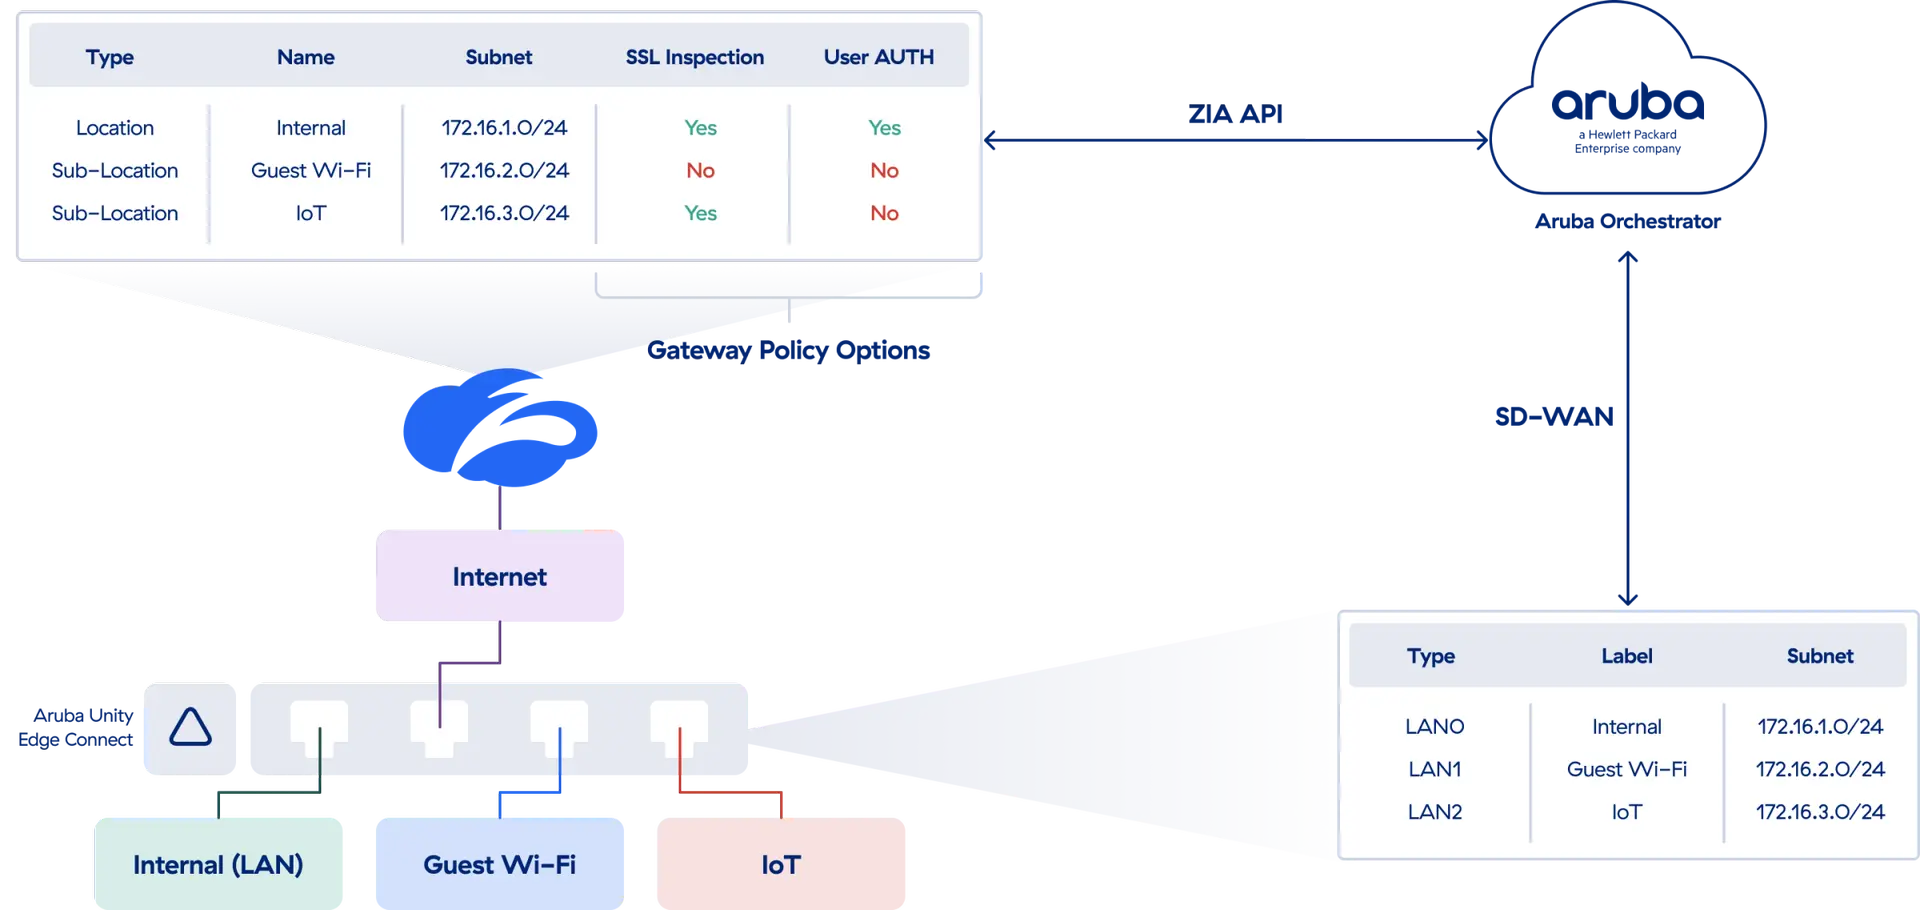
True zero-touch provisioning means all policies, including Gateway Options and location/sub-location rules, are defined once and pushed automatically to all sites. This lets you deploy new policies quickly across hundreds or even thousands of sites in a matter of minutes.
Fully automated onboarding
Fully automating IPsec tunnel configuration between Aruba EdgeConnect SD-WAN appliances and proximity-based ZIA Public Service Edge PoP eliminates the time-consuming task of manually defining IPsec tunnels at every branch site.
Application, user and device level control
With the Aruba and Zscaler API integration, you can specify a set of Zscaler security policies to be applied for branch locations. Different policy enforcement is occasionally required for specific applications, users, and devices in a branch location. The Gateway Options feature enables you to define exceptions for sub-locations.

